Mallory
← Back to News
identity-authentication-vulnerabilityai-platform-securitywidely-deployed-product-advisory

IBM ContextForge MCP Gateway Flaw Exposes Identity Data and Enables Claim Replay

Vulnerability Disclosure · 2 sources · Updated 1d ago · First seen Nov 16, 2026
IBM ContextForge MCP Gateway Flaw Exposes Identity Data and Enables Claim Replay

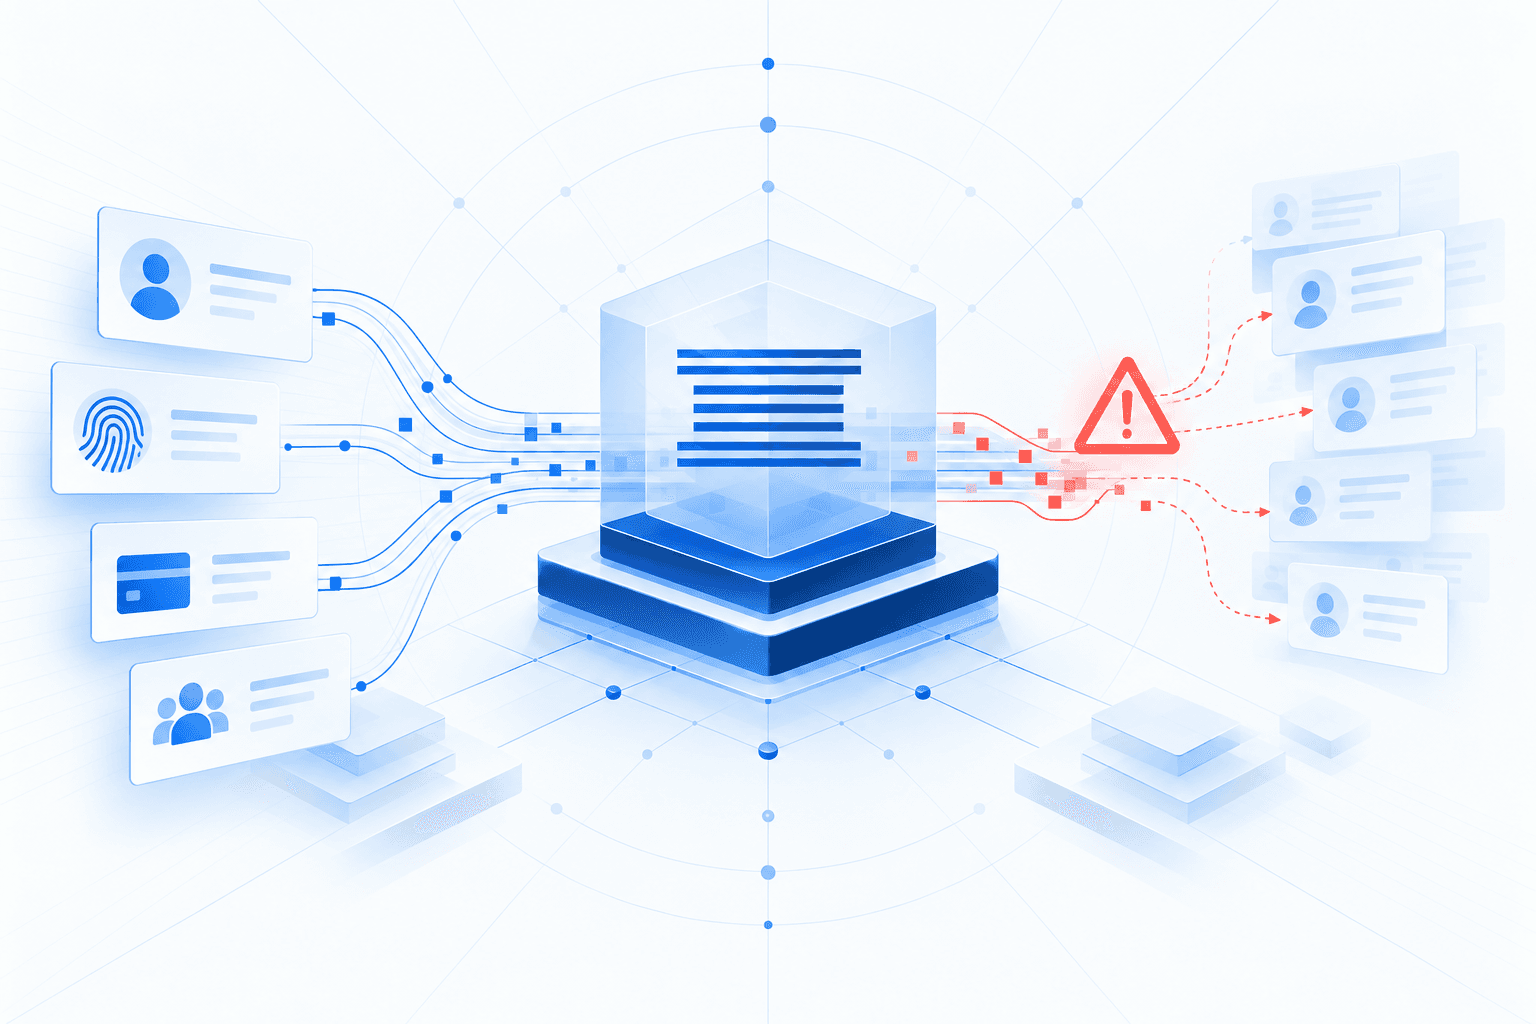
IBM disclosed CVE-2026-110278, an information exposure and identity-claim replay vulnerability affecting IBM ContextForge MCP Gateway versions 1.0.0 through 1.1.0. During tool invocations and resource reads, the gateway ignores per-server identity propagation settings, potentially sending user identity information to upstream MCP servers configured not to receive it. Static signature payloads also allow identity propagation claim signatures to be replayed. IBM assigned the vulnerability a CVSS v3.1 score of 7.4.

IBM recommends upgrading immediately to version 1.1.1. Organizations unable to upgrade should disable identity propagation globally and restrict gateway access to trusted users. The replay behavior aligns with MITRE’s CWE-294: Authentication Bypass by Capture-replay, which describes how reusing valid authentication messages can enable unauthorized access or identity impersonation. MITRE recommends cryptographically protected freshness mechanisms, such as signed sequence numbers or timestamps, to counter replay attacks.
Do you run this?See affected versions and whether adversaries are exploiting it.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

3 events · Nov 12, 2026
  1. Nov 12, 20266d ago

    IBM discloses ContextForge identity exposure and replay vulnerability

    On November 12, 2026, IBM disclosed CVE-2026-110278, rated CVSS 7.4, explaining that ignored per-server settings can expose user identities to upstream MCP servers and static signature payloads permit identity-claim signature replay. IBM recommended upgrading to version 1.1.1 or, if upgrading is not possible, disabling identity propagation globally and restricting gateway access to trusted users.

    Security Bulletin: IBM ContextForge MCP Gateway is affected by an information exposure vulnerability
  2. Reported Nov 12, 20266d ago

    IBM fixes CVE-2026-110278 in ContextForge MCP Gateway 1.1.1

    IBM identified ContextForge MCP Gateway 1.1.1 as the fixed release for the identity information exposure and claim-signature replay vulnerability affecting versions 1.0.0 through 1.1.0.

    Security Bulletin: IBM ContextForge MCP Gateway is affected by an information exposure vulnerability
  3. Reported Nov 12, 20266d ago

    Wolfgang Kriesel reports ContextForge identity propagation vulnerability to IBM

    Wolfgang Kriesel reported the vulnerability later designated CVE-2026-110278 to IBM.

    Security Bulletin: IBM ContextForge MCP Gateway is affected by an information exposure vulnerability
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

1 linked
Contextforge-Mcp-Gateway
Do you run this?See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
Check Your Exposure
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.