Mallory
← Back to News
industrials-sector-threatphishing-campaign-intelligenceremote-access-implantinitial-access-method

Three Cybercrime Campaigns Exploit US Freight Workflows to Steal Data and Deploy Backdoors

Sector Threat Intelligence · 5 sources · Updated 1h ago · First seen Nov 17, 2026
Three Cybercrime Campaigns Exploit US Freight Workflows to Steal Data and Deploy Backdoors

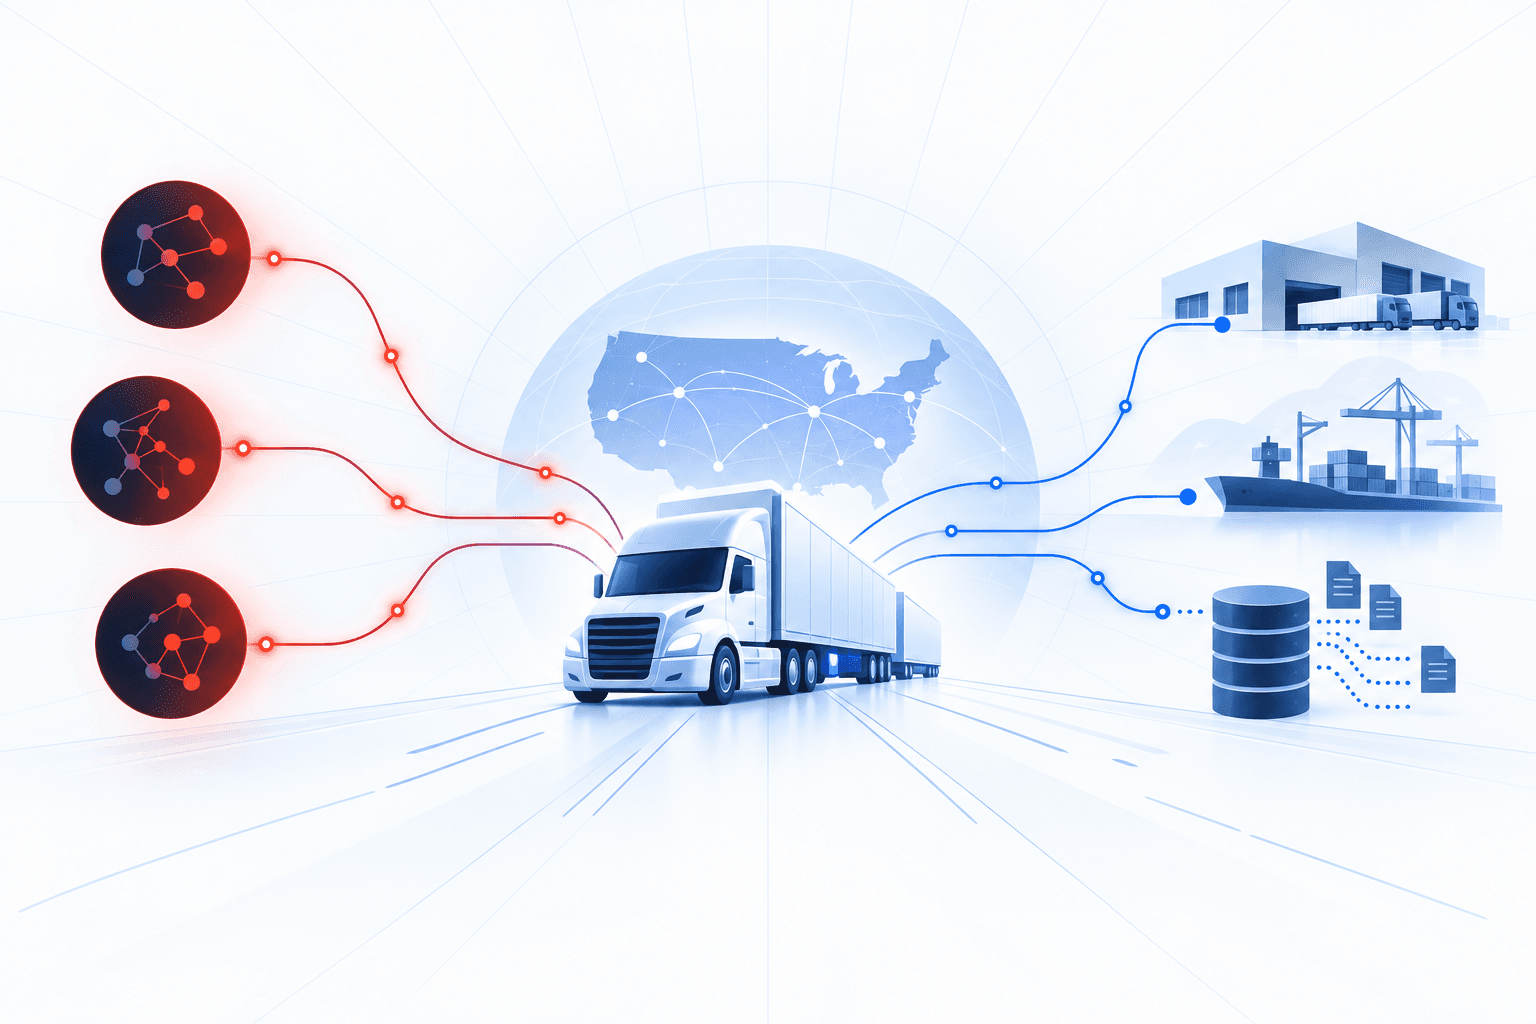
ANY.RUN researchers identified three cybercrime campaigns targeting US trucking and logistics organizations through routine carrier verification, broker onboarding, document exchange, and freight booking. HelloFriends impersonates carrier-verification services to steal sensitive business information, credentials, and one-time passwords, sending collected data through Telegram. NodeRemote uses malicious broker documents and social engineering to install a persistent Node.js-based backdoor.

Fake Freight Portals impersonates freight platforms and distributes malicious WebDAV shortcuts that deploy MeshCentral and CastleRAT. The campaign also attempts to obtain BitLocker recovery keys and weaken Microsoft Defender protections. Alongside commodity Microsoft 365 phishing and ClickFix activity, these campaigns illustrate how familiar freight transactions can become entry points for credential theft and persistent remote access. Logistics security teams should prioritize independent verification of onboarding requests, scrutiny of document and shortcut downloads, and alerts for unexpected remote-management tools or endpoint-protection changes.
Who's targeting your sector?See the actors and campaigns active against you right now.
See sector threats
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

5 events · Nov 2026
  1. Reported Nov 17, 20269h ago

    Researchers observe additional Microsoft 365 phishing and ClickFix activity

    ANY.RUN researchers also observed Microsoft 365 phishing and ClickFix activity affecting logistics-related websites and users. These attacks used broadly deployed infrastructure and social engineering rather than exclusively freight-specific targeting.

    3 Cybercrime Campaigns Targeting US Logistics: How Attackers Exploit Freight Workflows - Malware News - Malware Analysis, News and Indicators
  2. Reported Nov 17, 20269h ago

    Fake Freight Portals investigation exposes MeshCentral and CastleRAT infection chain

    ANY.RUN researchers identified freight-platform impersonation targeting logistics professionals, including an observed WebDAV-shortcut infection chain that deployed MeshCentral for unauthorized remote access. The chain also attempted to obtain BitLocker recovery keys, configure Microsoft Defender exclusions, and deploy CastleRAT.

    3 Cybercrime Campaigns Targeting US Logistics: How Attackers Exploit Freight Workflows - Malware News - Malware Analysis, News and Indicators
  3. Reported Nov 17, 20269h ago

    NodeRemote investigation reveals backdoor delivery through bogus broker documents

    ANY.RUN researchers observed malicious documents and social engineering deploying a persistent Node.js-based backdoor against logistics organizations. Infection chains involved ClickFix-style instructions, PowerShell, or VBS scripts, while relay-configuration mechanisms used blockchain, DNS, and GitHub to help maintain communications.

    3 Cybercrime Campaigns Targeting US Logistics: How Attackers Exploit Freight Workflows - Malware News - Malware Analysis, News and Indicators
  4. Reported Nov 17, 20269h ago

    HelloFriends campaign uncovered targeting US trucking companies

    ANY.RUN researchers identified fraudulent carrier-verification portals impersonating services including SAFER and Motus and personalized with company information. The portals collect sensitive business information, credentials, and one-time passwords, transmitting stolen data through Telegram.

    3 Cybercrime Campaigns Targeting US Logistics: How Attackers Exploit Freight Workflows - Malware News - Malware Analysis, News and Indicators
  5. Nov 2026

    NodeRemote introduces MSI installer delivered through load-tracking lure

    NodeRemote operators introduced an MSI installer delivered through a logistics load-tracking lure, adding another delivery method alongside existing PowerShell and VBS chains. Researchers identified the persistence name NodeRemoteWebServer- in the November variant.

    Fake FMCSA, DAT, and TIMOCOM Portals: 3 Cyberattacks Targeting US Logistics | by ANY.RUN | Nov, 2026 | Medium
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Observables

16 linked

Indicator values are masked on this page. View all 16 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
See Your Sector's Threats
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.