Mallory
← Back to News
search-ad-manipulationidentity-impersonation-fraudloader-delivery-mechanisminitial-access-method

Malicious Google Ads Push Fake Developer Tools Through Suspected Advertiser Account Abuse

Social Engineering & Fraud · 2 sources · Updated 2h ago · First seen Nov 19, 2026
Malicious Google Ads Push Fake Developer Tools Through Suspected Advertiser Account Abuse

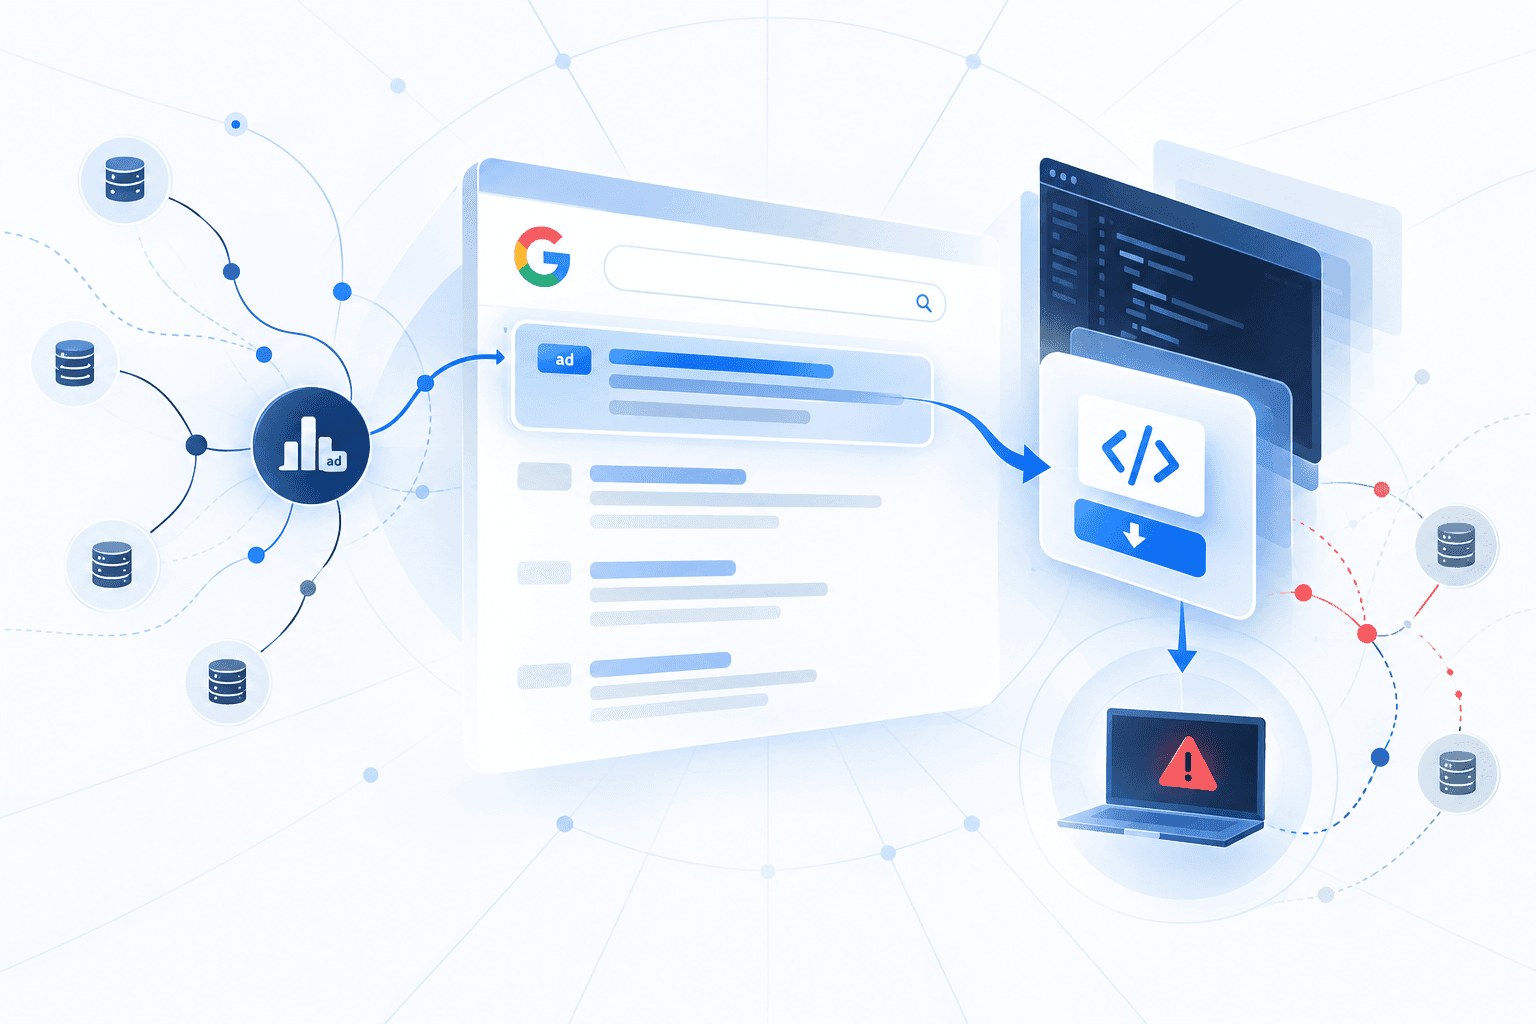
Malicious Google search advertisements impersonated Codex, Claude Code, and Homebrew to lure developers into running unsafe installation commands, Cato Networks reported. Shared downstream domains and encrypted loaders linked parts of the Claude and Codex activity to an Atomic macOS Stealer (AMOS)-associated delivery system, without establishing a single operator or confirming every final payload. Other investigated delivery chains used Claude-themed JavaScript for Automation and a malicious macOS application named DayNote distributed through Homebrew lookalikes. Advertiser identity mismatches suggested account or identity abuse, while selective redirects were consistent with traffic cloaking; neither finding established compromise of the legitimate tool providers.

The findings follow Malwarebytes’ earlier disclosure of a separate operation that used fake Google Ads advertisements and Google Sites landing pages to steal advertisers’ Google credentials. Attackers reused compromised accounts and victims’ advertising budgets to spread fraudulent ads, causing account takeovers, unauthorized administrator additions, lockouts, and fraudulent spending. That investigation demonstrates an advertiser-account abuse model, but does not establish a direct connection to the developer-tool campaigns. Defenders should correlate suspicious ad clicks and browser activity with shell execution and downloaded files, prioritize the identified malicious domains and repository paths rather than block shared infrastructure wholesale, and investigate unexpected Google Ads administrators or spending.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

13 events · Nov 6, 2026 – Nov 11, 2026
  1. Reported Nov 19, 20265h ago

    Claude installation lure reveals an AMOS-associated encrypted delivery chain

    A fake Claude page at parentpreneurx[.]com supplied a command that fetched an encrypted shell loader from vine-96[.]com, ultimately attempting to download and launch /tmp/helper. Reuse of grove-satin[.]com and similarities to earlier Codex loaders supported an AMOS-associated delivery assessment, but did not establish every final payload as AMOS or identify confirmed exfiltration destinations.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  2. Reported Nov 19, 20265h ago

    Cato uncovers malicious ads impersonating Codex, Claude Code, and Homebrew

    Cato investigated advertisements directing developers to fake installation pages and unsafe local commands, with unrelated advertiser identities suggesting account or identity abuse rather than proving compromise. Shared downstream domains connected portions of the Claude and Codex activity, while Homebrew redirect cases without recovered payloads remained separate.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  3. Reported Nov 19, 20265h ago

    Separate Claude lure delivers a counterfeit Finder application through JXA

    Analysis dated September 14 documented a claude-tools[.]com ClickFix chain that retrieved JavaScript for Automation, profiled the host, and downloaded a native macOS payload from kmtxyn[.]com/agent. The chain launched a counterfeit Finder.app while displaying a false installation error; neither its final malware family nor a connection to the linked Claude–Codex infrastructure was established.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  4. Reported Nov 19, 20265h ago

    Homebrew-lookalike investigation uncovers malicious DayNote application

    Analysis dated September 11 documented a disk-image delivery chain associated with nomeibrew[.]com and pirloz[.]com containing a malicious arm64 macOS application named DayNote. Its helper retrieved mutable update instructions through GitHub and jsDelivr, followed by encoded and encrypted stages that recovered final-payload retrieval instructions; the final malware family was not confirmed.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  5. Reported Nov 19, 20265h ago

    Earlier Codex investigations record installer, decoy, and delivery infrastructure

    Earlier observations documented swiftsaverfin[.]com serving a malicious installer and a fake TALLY decoy, alongside additional Codex script, payload-delivery, and telemetry infrastructure. These historical findings provided context for comparisons with subsequently investigated encrypted loaders.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  6. Nov 11, 20269d ago

    DayNote-linked repository and jsDelivr resource are recorded as unavailable

    Investigators recorded the referenced GitHub repository and jsDelivr update resource as unavailable. The report did not establish whether their unavailability resulted from provider enforcement.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  7. Nov 11, 20269d ago

    Akamai Cloud acknowledges an abuse submission

    Akamai Cloud/Linode acknowledged a portal submission concerning the investigated third-party service abuse. The acknowledgment did not establish compromise of the provider.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  8. Nov 6, 202614d ago

    Cato notifies M247 about Homebrew-lookalike infrastructure

    Cato notified M247 about nomeibrew[.]com and its historical association with 193.187.151[.]195. The notification concerned third-party infrastructure abuse, not an established compromise of the provider.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  9. Nov 6, 202614d ago

    Cloudflare restricts reported codex-notes URLs

    Cloudflare acknowledged the codex-notes[.]com abuse report, said it had forwarded the report to the website owner and hosting provider, and reported restricting access to the reported URLs.

    Malicious Google Ads Promote Fake Developer Tools | Cato Networks
  10. Reported Jan 15, 20252y ago

    Cloaked phishing campaign switches to a fake Google Authenticator site

    When researchers revisited the third campaign, its redirects led to a counterfeit Google Authenticator website likely intended to distribute malware. Earlier observations had connected its malicious advertisements to an advertiser-account phishing portal.

    The great Google Ads heist: criminals ransack advertiser accounts via fake Google ads | Malwarebytes
  11. Reported Jan 15, 20252y ago

    Malwarebytes reports more than 50 fraudulent advertisements to Google

    Researchers reported more than 50 fraudulent advertisements attributed to the Brazil-linked cluster to the Google Ads team. They observed malicious advertisements rapidly reappearing despite reporting.

    The great Google Ads heist: criminals ransack advertiser accounts via fake Google ads | Malwarebytes
  12. Reported Jan 15, 20252y ago

    Investigators identify distinct advertiser-phishing clusters

    Malwarebytes identified a prolific Portuguese-speaking cluster likely operating from Brazil and another using Hong Kong advertiser accounts and Chinese-language code. A third, possibly Eastern European campaign used fake CAPTCHA lures and cloaking rather than Google Sites.

    The great Google Ads heist: criminals ransack advertiser accounts via fake Google ads | Malwarebytes
  13. Reported Jan 15, 20252y ago

    Advertiser-account phishing operation abuses Google Ads to spread

    Malwarebytes uncovered fraudulent Google Ads advertisements that routed advertisers through Google Sites lookalikes to credential-stealing portals. Attackers used compromised advertiser accounts to propagate the operation, with victims reporting unauthorized administrator additions, fraudulent spending, and account lockouts.

    The great Google Ads heist: criminals ransack advertiser accounts via fake Google ads | Malwarebytes
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

2 linked

Affected products

2 linked
Claude CodeCodex

Observables

70 linked

Indicator values are masked on this page. View all 70 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.