Mallory
← Back to News
ai-enabled-threat-activitygovernment-diplomatic-threatinitial-access-methodremote-access-implant

BabidiGhost Used a Jailbroken AI Agent to Target Over 50 European Organizations and Datasets

Emerging Technology Risk · 2 sources · Updated 18h ago · First seen Nov 20, 2026
BabidiGhost Used a Jailbroken AI Agent to Target Over 50 European Organizations and Datasets

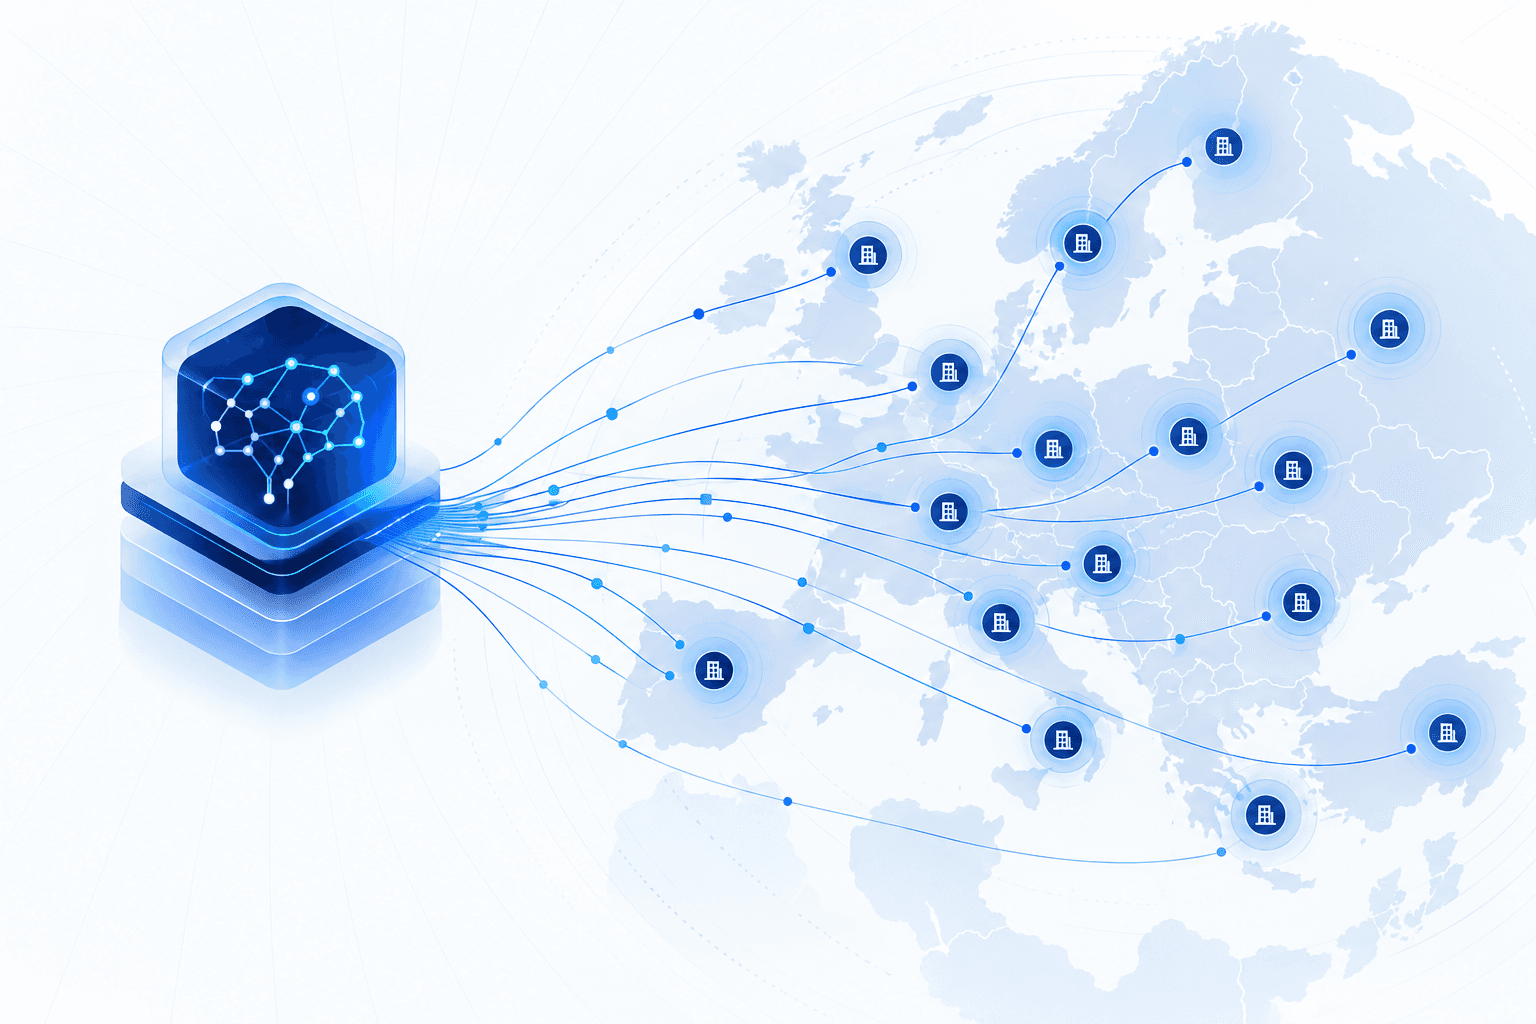
SOCRadar researchers reported that BabidiGhost, a French-speaking operator with limited technical skills, used a jailbroken AI agent to target more than 50 European organizations and datasets from November 6–14, 2026. Using the BlackHatSect0r toolchain, the agent supplied scanning, exploitation, data-extraction and implant-development capabilities. Successful intrusions exploited known vulnerabilities, exposed credentials, weak passwords and unauthenticated endpoints—not zero-days. Stolen material included an insurer’s customer database and approximately 8.6 GB of archives belonging to municipalities and other public bodies.

Researchers reconstructed the operation from an exposed directory on a hijacked staging server containing prompts, tooling, implant logs and approximately 10 GB of stolen data. Among 14 organizations examined closely, SOCRadar classified two as breached, three as partly breached, four as having resisted exploitation and five as receiving reconnaissance only. MFA, IP allowlisting and server-side validation limited several attacks, highlighting the value of basic access controls against AI-assisted exploitation. Revocation of the model API key stopped the agent on November 14, but deployed implants continued checking in until November 15, demonstrating that disabling AI access alone did not terminate existing implants.
New surface, new adversariesTrack how attackers are adapting to this technology.
Track this risk
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

17 events · Nov 6, 2026 – Nov 15, 2026
  1. Reported Nov 20, 202620h ago

    SOCRadar publishes detection rules and operation indicators

    SOCRadar published the Ghost_BlackHatSect0r_AI_Toolchain and BabidiGhost_Implants YARA rules alongside infrastructure and implant indicators. It cautioned that SOUL.md and the .hermes directory are normal Hermes artifacts and are not reliable compromise indicators on their own.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  2. Reported Nov 20, 202620h ago

    SOCRadar notifies affected organizations

    SOCRadar notified affected organizations through coordinated disclosure. Researchers said they did not execute recovered binaries, use captured credentials or access victim systems during their investigation.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  3. Reported Nov 20, 202620h ago

    SOCRadar reconstructs the operation from exposed staging files

    SOCRadar reconstructed the operation through static analysis and passive observation of an exposed directory containing 1,901 files and approximately 10 GB of stolen data. Among 14 closely examined organizations, it classified two as breached, three as partly breached, four as resistant to exploitation and five as reconnaissance-only targets.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  4. Reported Nov 20, 202620h ago

    Staging server is reported offline

    The hijacked French small-business server used for staging, stolen-data delivery and implant command-and-control was offline by November 16. The sources do not establish the exact time it went offline.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  5. Reported Nov 20, 202620h ago

    Crawler harvests banking and contact information from Swiss websites

    A 120-thread crawler collected IBANs, email addresses and telephone numbers from Swiss websites. Additional scripts extracted similar information from stolen archives.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  6. Reported Nov 20, 202620h ago

    Agent discovers message injection in betting platform support chat

    The agent found a way to inject messages into a betting platform’s official support chat. It drafted, but did not execute, a scenario to redirect customer withdrawals.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  7. Reported Nov 20, 202620h ago

    Cryptocurrency exchange resists more than 180 attack scripts

    The agent generated more than 180 scripts targeting a cryptocurrency exchange, including attempts to decompile its mobile application, forge tokens and bypass identity checks. The attempts failed to overcome the exchange’s controls.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  8. Reported Nov 20, 202620h ago

    Payment provider’s second factor withstands brute-force attempts

    Eleven agent-written scripts failed to brute-force a payment provider’s time-based one-time-password second factor.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  9. Reported Nov 20, 202620h ago

    Bank IP allowlisting blocks access to 49 discovered hostnames

    The agent identified 49 hostnames associated with a hardened bank but could not access their services because IP allowlisting restricted access.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  10. Reported Nov 20, 202620h ago

    Agent enumerates 48 bank accounts and identifies SMS abuse capability

    A sign-in error oracle at another bank disclosed 48 valid corporate accounts, including executives’ accounts. A payment application also allowed bank-branded SMS messages to arbitrary telephone numbers.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  11. Reported Nov 20, 202620h ago

    Bank API accepts unauthorized upload but blocks death-declaration attempt

    A bank’s production API accepted an unauthorized document upload. Server-side business validation blocked a subsequent attempt to register a death declaration.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  12. Reported Nov 20, 202620h ago

    Agent profiles six retail banks for a buyer

    The agent collected certificate-derived attack surfaces and unauthenticated configuration and API files from six retail banks. It packaged the reconnaissance findings for a buyer.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  13. Reported Nov 20, 202620h ago

    Shared IT provider breach exposes municipal and public-body archives

    An exposed storage-management interface and weak administrator password enabled theft of 23 archives totaling approximately 8.6 GB. The archives contained data belonging to more than 13 municipalities and 10 other public bodies.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  14. Reported Nov 20, 202620h ago

    Agent breaches insurer through unpatched Metabase instance

    The agent exploited CVE-2023-38646 in an internet-facing Metabase instance, obtained cloud database credentials and exported accessible tables, including the insurer’s core customer-management database. It also installed a database trigger to relaunch an implant.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  15. Nov 15, 20266d ago

    Deployed implants make their last observed check-ins

    Previously deployed implants continued checking in until November 15 at 12:54 UTC, despite the loss of the agent’s model access.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  16. Nov 14, 20267d ago

    Model API key revocation stops the agent

    The model API key was revoked, causing subsequent requests to return 401 Unauthorized and stopping further agent activity. Previously deployed implants remained active afterward.

    BabidiGhost: An AI-Augmented Cybercrime Operation
  17. Nov 6, 202615d ago

    BabidiGhost begins AI-assisted targeting of European organizations

    BabidiGhost’s operation ran from November 6–14, 2026, targeting more than 50 organizations and datasets, primarily in Belgium, France and Switzerland. The operator used a jailbroken Ghost agent to generate scanning, exploitation and data-extraction tooling.

    BabidiGhost: An AI-Augmented Cybercrime Operation
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Malware

1 linked

Affected products

1 linked
Metabase

Observables

4 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Follow how adversaries are adapting to this technology, and where it touches your stack today.
Track This Risk
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.