
Loading story…
Colt Technology Services is still recovering from a ransomware attack attributed to the Warlock group, with full restoration expected by late November. The attack, which began on August 12, disrupted customer platforms, billing, and service portals, and involved data exfiltration, possibly via SharePoint vulnerabilities. Colt has notified authorities in 27 countries and continues to prioritize restoration of critical services while monitoring for further risks.
Mallory correlates global threat intelligence with your attack surface — know if you’re exposed before adversaries strike.
1 event from the most recent confirmed update back to the earliest known activity.
Initial story creation
3 references tracked. Mallory keeps watching after this page renders.
scworld.com
Open sourcescworld.com
Open sourcego.theregister.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Sophos reported that the ransomware group **Warlock Group**, tracked as **GOLD SALEM**, has been compromising enterprise networks and deploying **Warlock ransomware** since March 2025, with 60 publicly named victims through mid-September across North America, Europe, and South America. The operation used a Tor-based leak site, activity on underground forums, and possibly relationships with initial access brokers to support intrusions and extortion. Observed attacks began with exploitation of the **SharePoint ToolShell** exploit chain, followed by deployment of an **ASPX web shell** and a Golang-based WebSockets backdoor for persistence. Sophos said the actors stole credentials with **Mimikatz**, moved laterally with **PsExec** and **Impacket**, deployed ransomware through **Group Policy Objects**, and disabled endpoint protection using a **bring-your-own-vulnerable-driver** technique involving a vulnerable **Baidu Antivirus** driver; investigators also observed abuse of **Velociraptor** to establish a **Visual Studio Code** network tunnel. Microsoft tracks the activity as **Storm-2603** and assesses it with moderate confidence as China-based, though Sophos said it could not independently confirm that attribution.
Jun 29, 2026
Warlock ransomware was deployed against US firms through the exploitation of a zero-day vulnerability in Microsoft SharePoint, identified as CVE-2025-53770. The attacks have been attributed to the China-based CamoFei APT group, with evidence indicating that the threat actor leveraged the ToolShell exploit to gain initial access and deploy both Warlock and LockBit ransomware payloads. The campaign is notable for its use of DLL sideloading and a custom command and control framework referred to as `ak47c2`, as well as the bundling of multiple ransomware payloads in a single attack. Security researchers have traced the origins of the Warlock ransomware to activity dating back to 2019, suggesting that the group behind it is not new but has evolved its tactics. The operation stands out because, unlike most ransomware campaigns typically associated with Russian actors, Warlock is linked to Chinese threat groups, including Budworm (APT27), Sheathminer (APT31), and Storm-2603. The attacks highlight a growing trend of Chinese APTs engaging in financially motivated ransomware operations targeting Western organizations.
Jun 29, 2026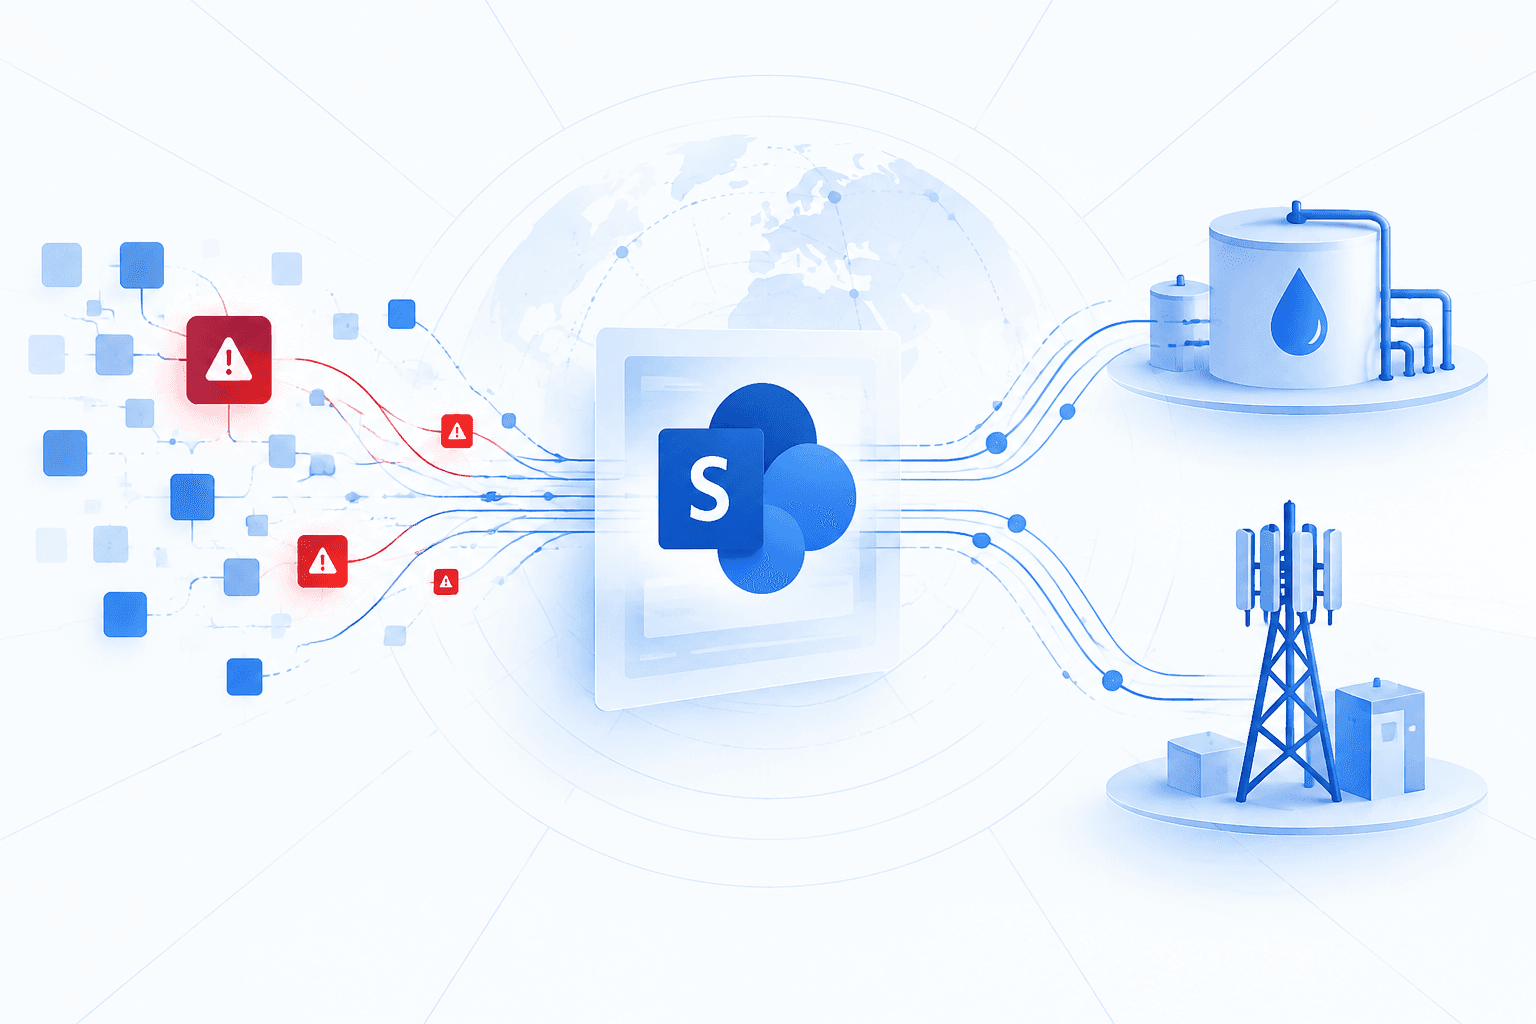
Symantec attributed a campaign using **Warlock ransomware** to the China-nexus Longlegs group, also tracked as Storm-2603. The group exploited on-premises Microsoft SharePoint Server vulnerabilities to target at least four Portuguese- and Spanish-speaking organizations in Europe, Africa, and Latin America, including water and telecommunications operators, a regional government body, and a university. Attackers used SharePoint web shells and forged machine-key-signed ViewState payloads to execute code, followed by reconnaissance, DLL sideloading, credential and domain enumeration, and lateral movement with legitimate or dual-use tools. Before encrypting systems, they distributed an AV/EDR-disabling utility consistent with **BYOVD** tradecraft and deployed Warlock to at least 33 systems through Active Directory's `SYSVOL` replication path, underscoring the ransomware risk posed by unpatched or inadequately mitigated SharePoint deployments.
Oct 2, 2026