
Loading story…
Russian-speaking threat actors have orchestrated a large-scale phishing campaign targeting the hospitality industry by registering over 4,300 domains that impersonate well-known travel and booking platforms such as Booking.com, Expedia, Agoda, and Airbnb. The campaign, active since at least February 2025, uses spam emails to lure hotel guests into clicking on links that redirect them to sophisticated fake websites. These sites are designed to appear legitimate, supporting 43 languages and employing brand logos, fake CAPTCHA checks, and customizations based on unique URL strings to increase credibility. Victims are prompted to enter their credit card details under the guise of confirming or paying for hotel reservations, with the sites even simulating 3D Secure verification processes to further the deception.
Analysis by Netcraft and security researchers has linked the campaign to Russian threat actors, citing language artifacts in source code and debugger output. The phishing infrastructure is highly organized, with domain names following consistent patterns such as "confirmation," "booking," and "reservation" to enhance the illusion of authenticity. The campaign's scale and technical sophistication pose a significant threat to travelers and the hospitality sector, with the potential for widespread theft of payment data and personal information. Security experts recommend heightened vigilance for unsolicited travel-related emails and verification of booking communications through official channels.

Get the infrastructure and lures behind it.
1 event from the most recent confirmed update back to the earliest known activity.
Security reporting in mid-November 2025 described an ongoing Russian-linked phishing operation using roughly 4,300 spoofed travel and hotel booking websites to steal guests' payment card data. The campaign targeted travelers by impersonating legitimate accommodation and travel services.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Attackers are exploiting hotel reservation systems and booking workflows in a fraud campaign dubbed the **Reservation Hijack Scam**, using stolen reservation details and compromised staff accounts to contact real travelers through trusted channels including Booking.com messaging, email, SMS, and WhatsApp. Researchers said the scam is especially effective because messages arrive in legitimate conversation threads or from authentic hotel accounts, making fake payment requests appear to be routine customer service. Victims are then directed to spoofed guest portals, branded PDFs, or typo-squatted payment sites designed to steal card details or induce bank transfers. In more advanced intrusions, attackers first phish hotel employees for credentials to hospitality platforms such as **Cloudbeds**, or gain persistent access by tricking partners into running malicious commands that deploy a remote access trojan. Cloudbeds said observed cases were caused by credential phishing rather than a breach of its platform. The activity has been reported most heavily in the **UK, France, Germany, the US, Brazil, and Australia**, prompting recommendations that travelers verify payment requests only through official hotel or booking channels, while hospitality organizations strengthen phishing-resistant authentication, access controls, monitoring, and incident response.
Jun 29, 2026
Finland’s National Cyber Security Centre warned that phishing campaigns targeting hotel reservations are abusing **Booking.com** and related accommodation services with messages that look legitimate because they contain real booking details. Victims have received messages shortly after making reservations, sometimes through **Booking.com’s own messaging channel** and sometimes via **WhatsApp**, with references to genuine hotel names, customer identities, and actual reservation information. The messages often begin as routine confirmations before claiming there is a problem with the booking, identity verification, or payment card. The fraudulent messages direct travelers to spoofed websites designed to mimic hotel or booking pages and steal payment-card data. Finnish authorities said the accuracy of the information strongly suggests attackers obtained access to hotel or reservation accounts, likely through phishing or other account compromise, allowing them to view reservation records and in some cases prior conversation history. Officials said similar incidents have been reported for years, with a notable rise in reported cases, and advised customers to verify any payment or identity requests through independent contact channels with the hotel or booking provider.
Jun 29, 2026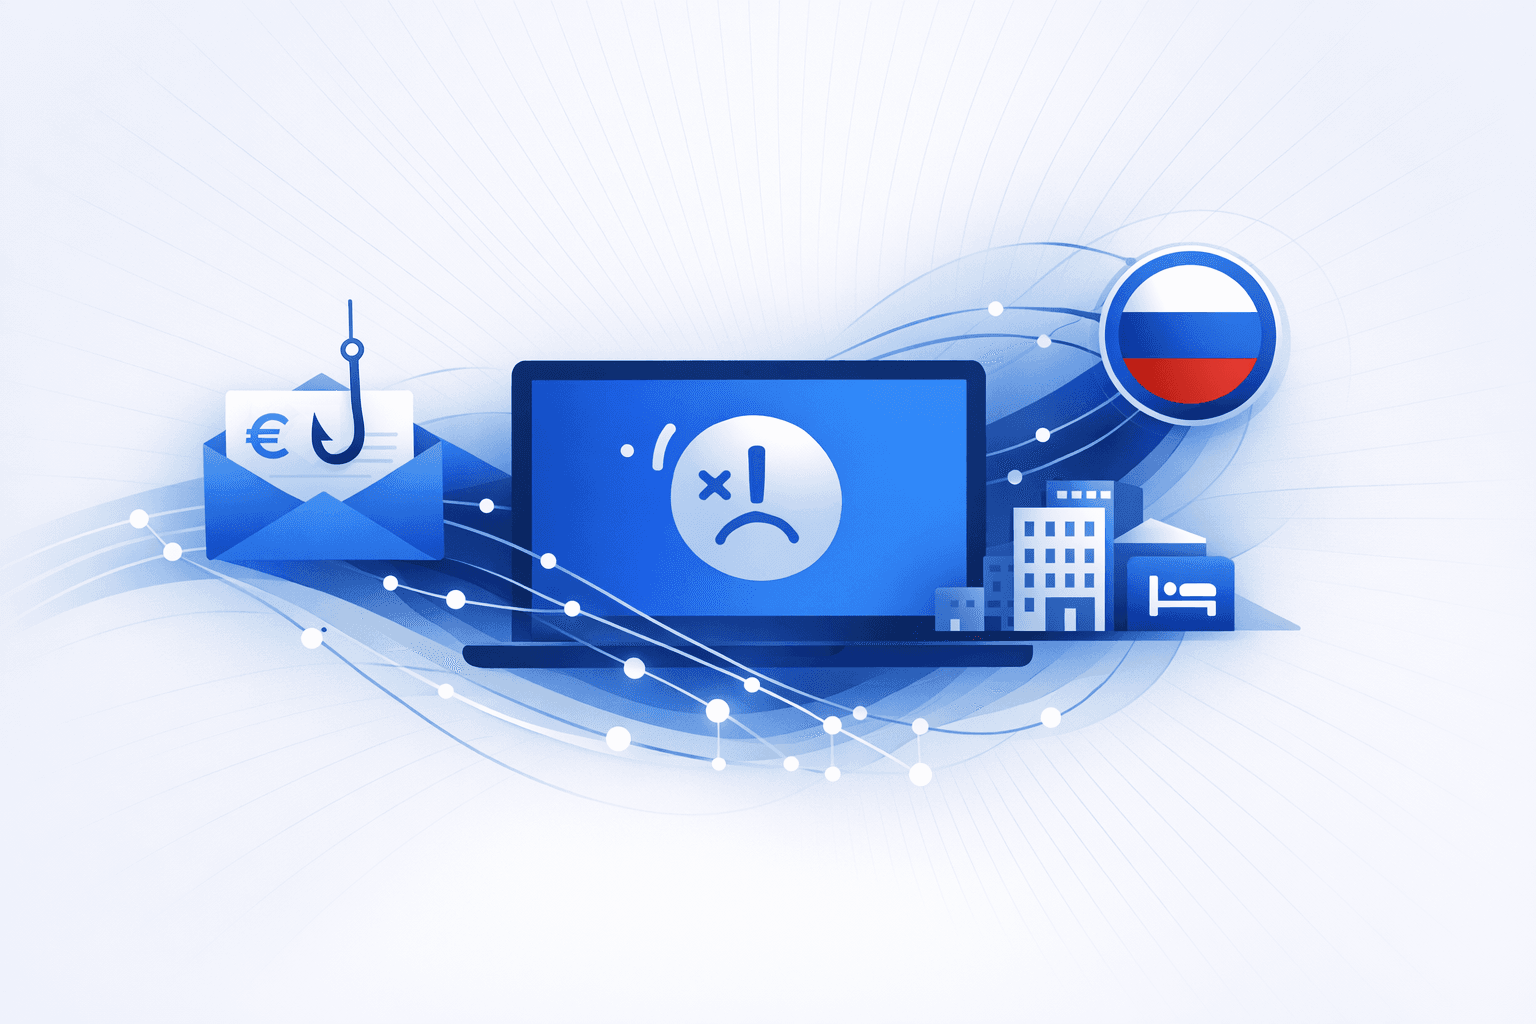
Suspected Russian cybercriminals have launched a sophisticated phishing campaign targeting the European hospitality industry, leveraging fake Windows Blue Screen of Death (BSOD) pages to distribute malware. The attack, tracked as "PHALT#BLYX" by Securonix researchers, begins with phishing emails impersonating popular booking platforms such as Booking.com, often using reservation cancellation lures with details in Euros to specifically target hotels, hostels, and inns in Europe. Victims are directed to high-fidelity cloned websites that mimic legitimate booking services, where they encounter fake error messages and BSOD screens designed to prompt them into executing malicious commands. The campaign employs the "ClickFix" technique, which manipulates users into manually running PowerShell or shell commands under the guise of resolving system errors. This process ultimately results in the installation of the DCRat malware, a remote access trojan capable of keylogging and other malicious activities. Technical indicators, including Russian-language debug strings and infrastructure geolocated to Russia, suggest a strong Russian connection. The campaign demonstrates a blend of social engineering and technical deception, exploiting human problem-solving instincts to compromise systems within the hospitality sector during its busiest season.
Jun 29, 2026