Remote Code Execution Vulnerabilities in Microsoft Update Services Exploited
Active Exploitation · 2 sources · Updated 4mo ago · First seen Nov 20, 2025
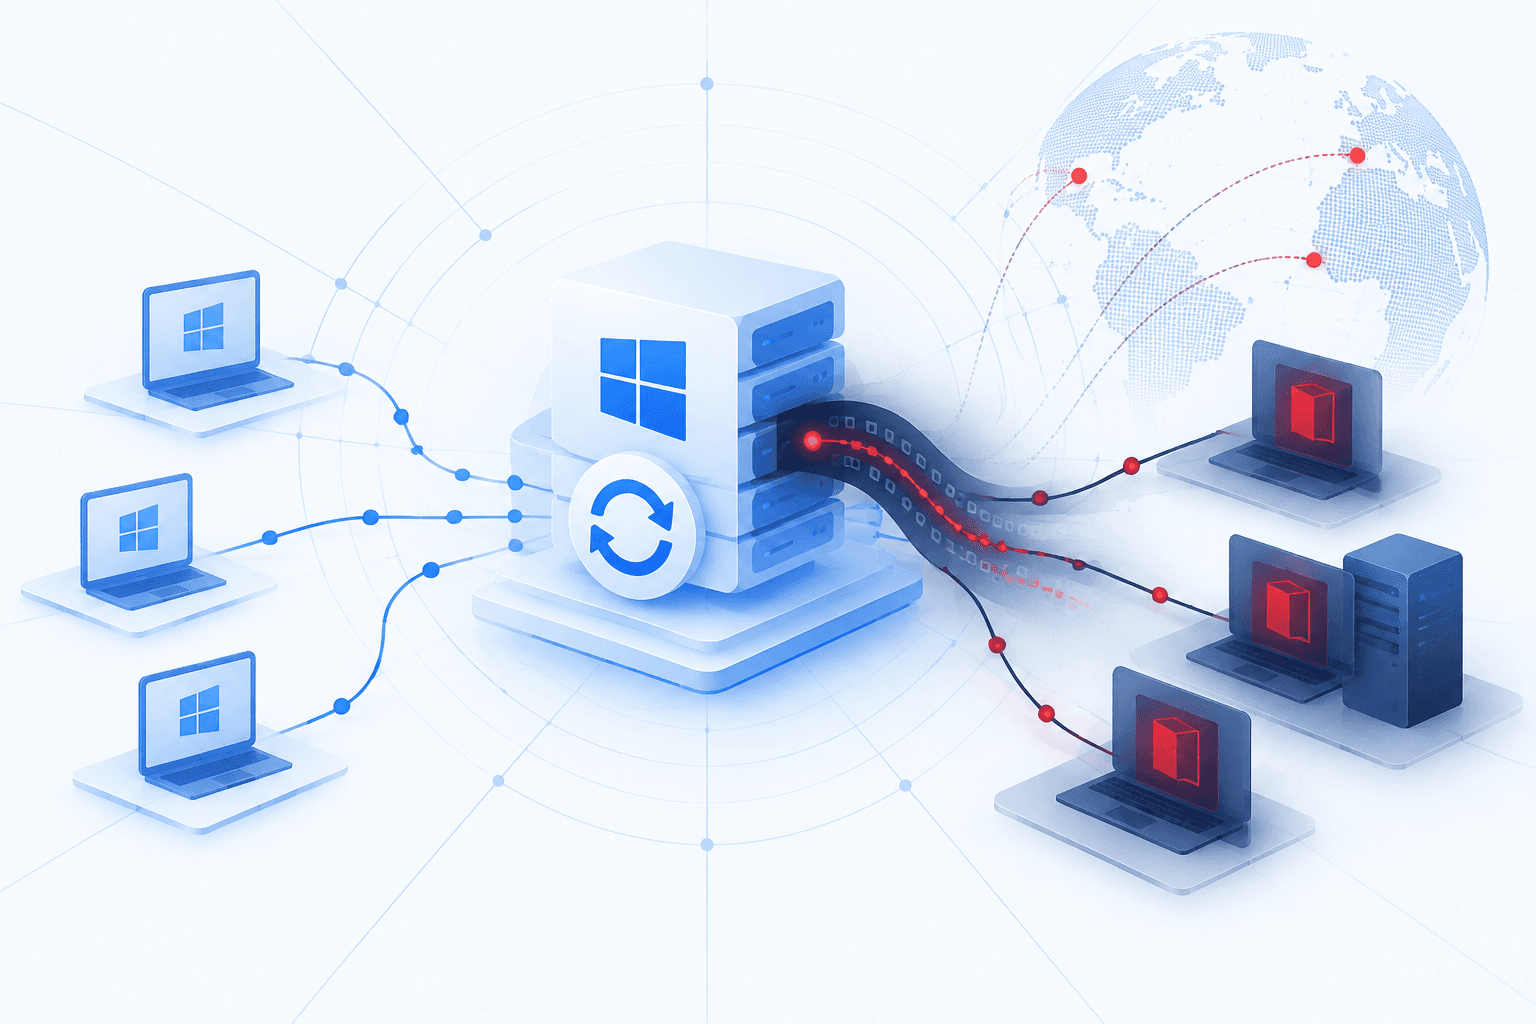
A critical remote code execution (RCE) vulnerability was discovered in Microsoft's Update Health Tools (KB4023057), a utility designed to facilitate rapid security updates via Intune. Researchers found that a misconfiguration involving abandoned Azure blob storage allowed attackers to register a storage account and receive requests from vulnerable devices worldwide, enabling arbitrary code execution. Microsoft has since responded to the disclosure, and newer versions of the tool have addressed the issue, but devices running the original version remain at risk if not updated.
Separately, a remote code execution vulnerability in Microsoft Windows Server Update Services (WSUS), tracked as CVE-2025-59287, was actively exploited by threat actors to deploy the ShadowPad backdoor malware. Attackers leveraged this flaw to gain system-level access using PowerCat and subsequently installed ShadowPad via certutil and curl. The exploitation of these vulnerabilities highlights the risks associated with update management tools and the importance of timely patching and secure configuration to prevent compromise by advanced persistent threats.