
Loading story…
The Black Cat cybercriminal group has launched a sophisticated malware campaign leveraging search engine optimization (SEO) poisoning to distribute trojanized installers of popular software such as Notepad++, Google Chrome, QQ International, and iTools. By manipulating search engine rankings, Black Cat positions convincing phishing websites at the top of search results, luring users to download malicious installers that deploy remote access backdoors. These fake sites often mimic legitimate repositories and employ multiple redirects, including pages styled to resemble GitHub, to enhance credibility and reduce suspicion. The malware delivered through these channels is designed to steal sensitive data, including browser information, keystrokes, and clipboard contents, posing significant risks to both individuals and organizations.
Analysts report that this campaign has compromised approximately 277,800 servers between early and late December 2025, with a particular focus on Chinese users, as indicated by the use of "cn" in the phishing domains. The infection process involves deceptive desktop shortcuts and covert backdoor installation, enabling attackers to exfiltrate data without user awareness. Black Cat has a history of using SEO poisoning for data theft and cryptocurrency fraud, and this latest campaign demonstrates their continued evolution in targeting users searching for trusted software through search engines like Microsoft Bing.
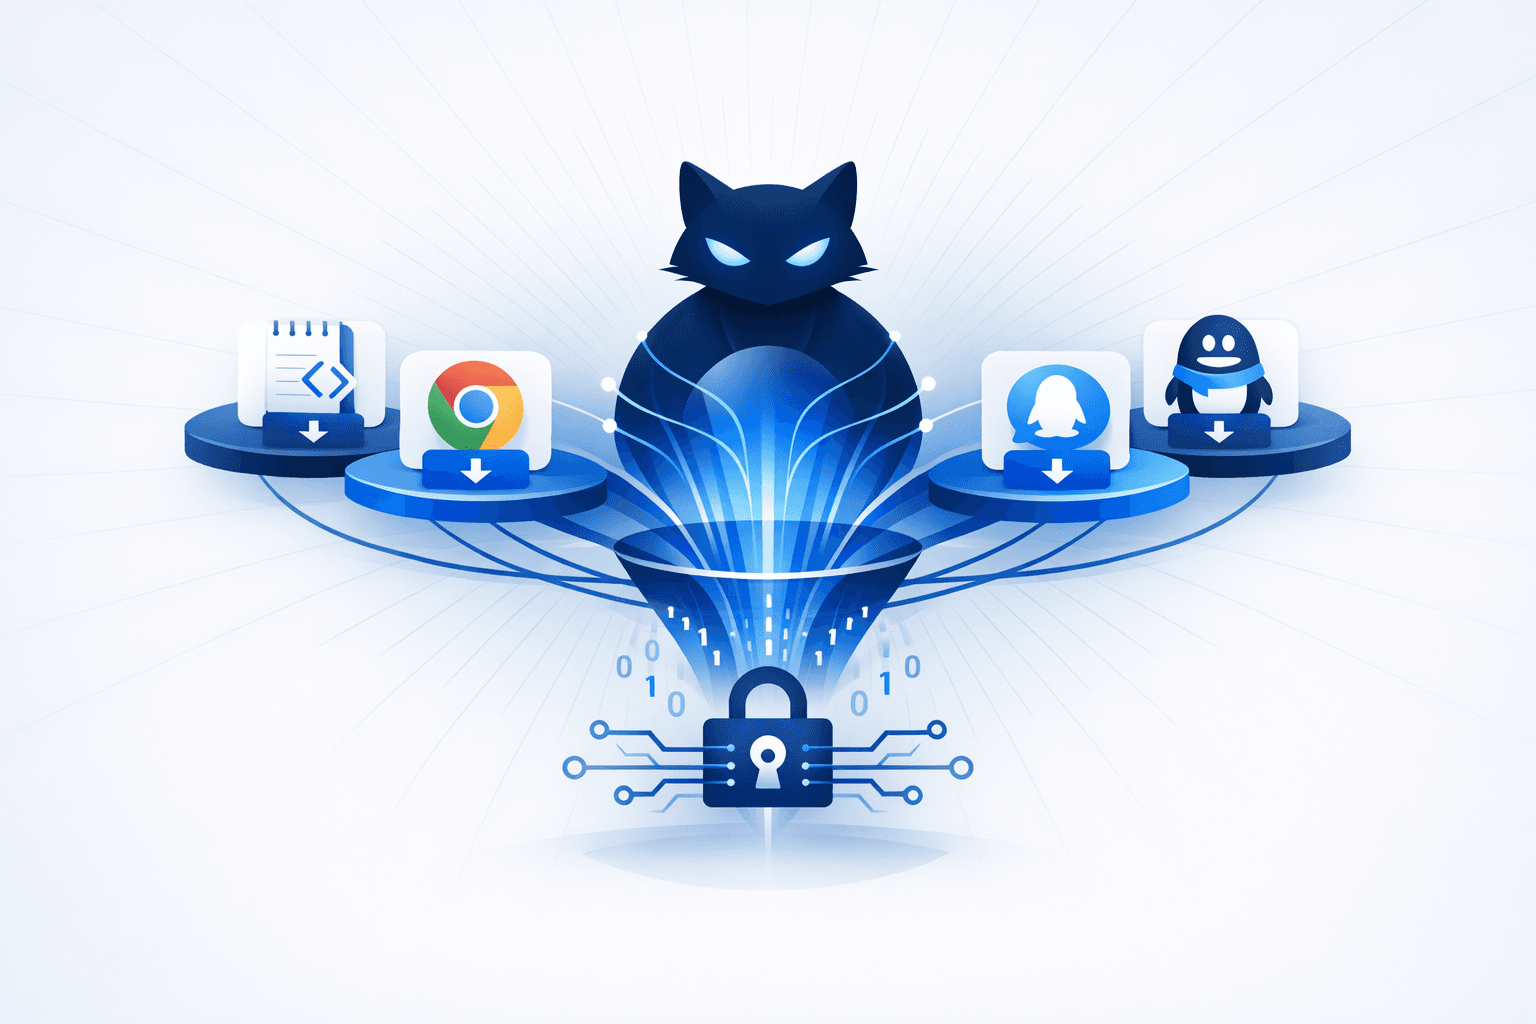
Get the infrastructure and lures behind it.
3 events from the most recent confirmed update back to the earliest known activity.
On January 7, 2026, reporting disclosed technical details of the campaign, including fake software sites, DLL side-loading, in-memory payload decryption, registry-based persistence, and data exfiltration to command-and-control infrastructure including sbido.com:2869.
Over a short period in 2025, the campaign's malicious installers deployed backdoor malware on roughly 277,800 hosts in China, with infections peaking at more than 62,000 in a single day. The malware enabled remote access and theft of browser data, keystrokes, and clipboard contents.
In December 2025, the Black Cat cybercrime group ran an SEO-poisoning campaign that pushed fake software download sites for programs such as Notepad++, Google Chrome, and QQ International to the top of search results, targeting Chinese users.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
A sophisticated SEO poisoning campaign is targeting Chinese-speaking Windows users by promoting fake software sites in search results. Victims are tricked into downloading trojanized installers that deliver Hiddengh0st and Winos malware, enabling remote access, data theft, and cryptocurrency wallet hijacking. The campaign uses advanced evasion, anti-analysis, and persistence techniques, making detection and removal challenging.
Jun 29, 2026
Affiliates of the **ALPHV/BlackCat** ransomware operation used malvertising campaigns on **Google** and **Bing** to impersonate popular business and IT software, including **Slack**, **Cisco AnyConnect**, **WinSCP**, **AnyDesk**, and **TreeSize Free**, in an effort to gain initial access to enterprise environments. Victims who clicked the ads were directed to download trojanized installers, often packaged as ISO files, that launched the **Nitrogen** malware family through **DLL sideloading** and **DLL preloading** techniques while displaying benign decoy installers to avoid suspicion. Researchers observed the activity targeting organizations in North America, including technology and non-profit sectors, and said the campaign appeared designed to prepare networks for later ransomware deployment. Analysis from Sophos and eSentire showed Nitrogen establishing persistence, attempting privilege escalation through a **CMSTPLUA UAC bypass**, and contacting command-and-control infrastructure over multiple protocols to retrieve follow-on payloads such as **Meterpreter** and in-memory **Cobalt Strike Beacons**. eSentire said it began tracking the campaign in June and stopped at least one intrusion before ransomware execution, while Sophos reported remediating infections before attackers could complete hands-on-keyboard activity. The activity was assessed as part of a broader access pipeline leading toward **BlackCat** ransomware attacks, underscoring how fake software ads are being used to convert routine IT searches into enterprise compromise.
Aug 15, 2026
Threat actors are using **compromised or spoofed websites** to trick victims into executing malware, with lures ranging from fake browser updates to counterfeit security-software download pages. Recorded Future’s Insikt Group reported that financially motivated **GrayCharlie** (overlapping with **SmartApeSG**) compromised multiple U.S. law-firm WordPress sites—potentially via a shared IT/marketing provider—and injected externally hosted JavaScript that redirected visitors to **bogus update pages** or **fake CAPTCHA** flows. Victims were prompted to run a PowerShell command via the Windows Run dialog, leading to **NetSupport RAT** installation and follow-on delivery of **Stealc** and **SectopRAT**; the operation’s infrastructure was noted as being supported by **MivoCloud** and **HZ Hosting Ltd.** Separately, Malwarebytes-linked reporting described a **typosquatting** campaign impersonating the Huorong antivirus site (`huoronga[.]com` vs. `huorong.cn`) to distribute **ValleyRAT** (built on the **Winos4.0** framework), attributed to the Chinese-speaking **Silver Fox APT**; the payload was routed through an intermediary domain and hosted on **Cloudflare R2**, with a ZIP masquerading as Huorong (`BR火绒445[.]zip`). In a different region and access vector, Group-IB reported Iran-linked **MuddyWater** running **Operation Olalampo** against MENA targets using **phishing emails** with malicious Office documents/macros to deploy new tooling including **GhostFetch** (dropping **GhostBackDoor**) and **CHAR** (a Rust backdoor controlled via a **Telegram bot**), plus variants using **HTTP_VIP** to deploy *AnyDesk*; the campaign also leveraged recently disclosed vulnerabilities on public-facing servers for initial access.
Jun 29, 2026