Malware Delivery via Deceptive Distribution and Evasion Techniques
Malware Intelligence · 3 sources · Updated 4mo ago · First seen Jan 14, 2026
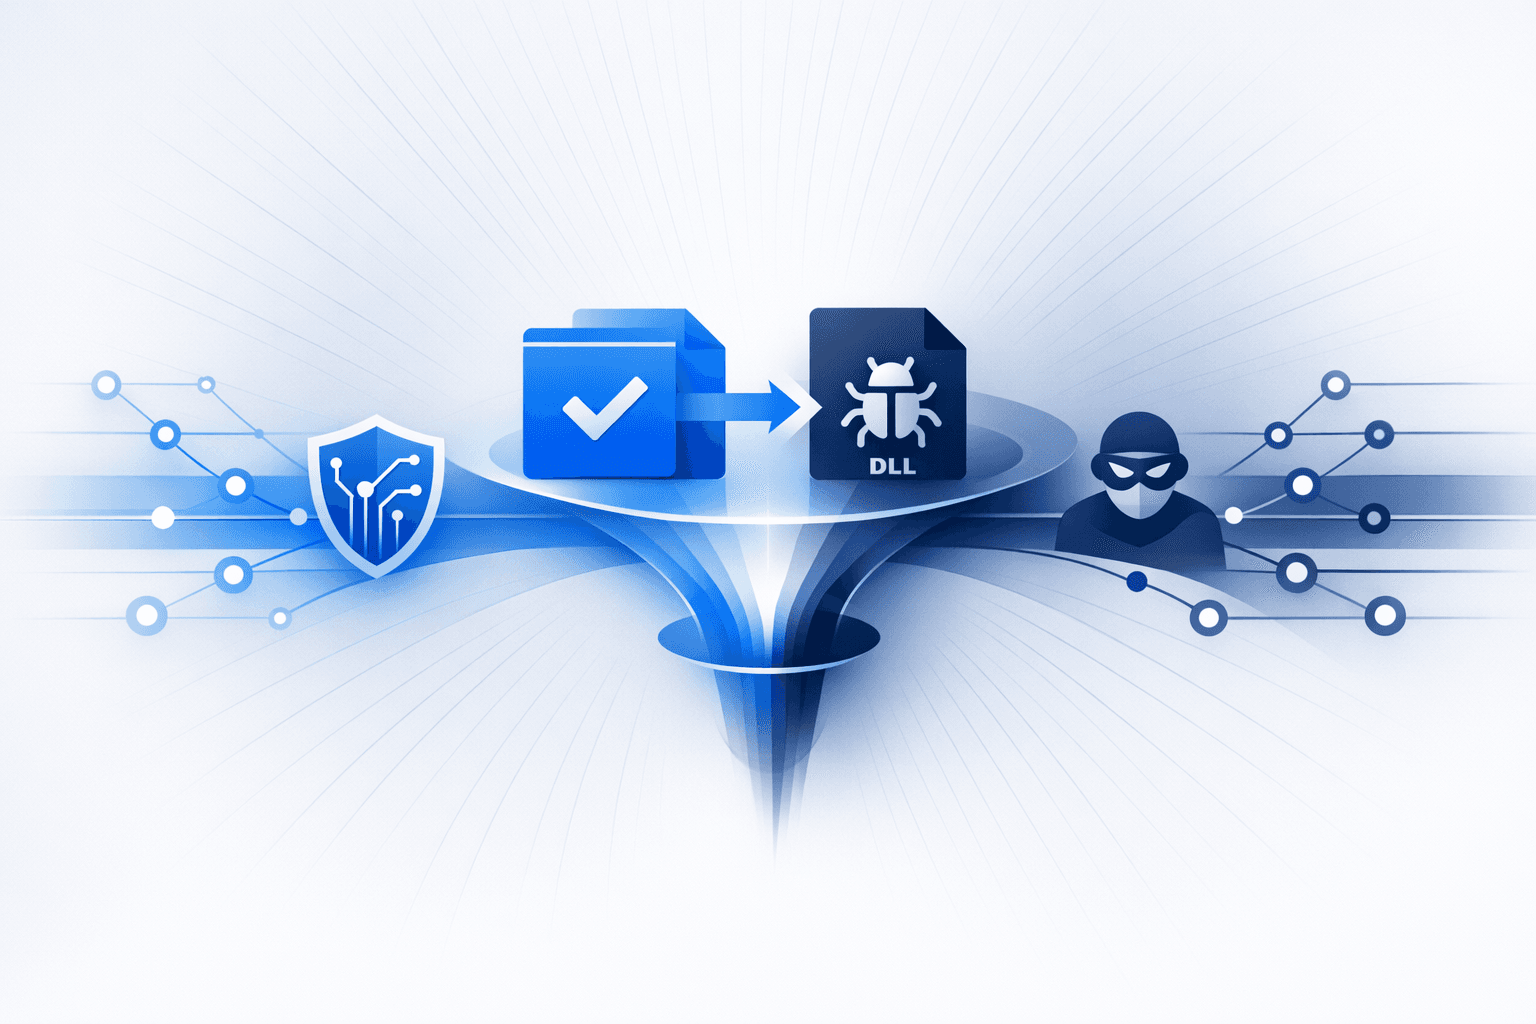
Threat researchers reported multiple active campaigns focused on stealthy malware delivery by abusing trusted execution paths and deceptive distribution. Trellix described attackers using DLL side-loading against a legitimate, signed ahost.exe binary associated with the c-ares ecosystem (commonly seen with GitKraken Desktop) by placing a malicious libcares-2.dll alongside the executable to trigger search-order hijacking and execute attacker code. The activity was linked to delivery of commodity malware families including Agent Tesla, Formbook, Remcos RAT, Quasar RAT, DCRat, XWorm, Vidar Stealer, Lumma Stealer, CryptBot, and others, with targeting observed across business functions (finance, procurement, supply chain, administration) and lures in multiple languages, suggesting regionally focused operations.
Separately, Malwarebytes documented a fake RustDesk download site (rustdesk[.]work) that installs legitimate RustDesk while silently deploying a persistent backdoor framework (Winos4.0) via a trojanized installer (e.g., rustdesk-1.4.4-x86_64.exe), relying on user deception rather than exploiting a software vulnerability. Sucuri detailed a WordPress compromise where attackers modified index.php to perform selective content injection/SEO cloaking, using IP-verified logic with hardcoded Google ASN CIDR ranges to serve malicious content to Googlebot while showing normal content to human visitors and site owners—an evasion technique that can facilitate downstream malware distribution while reducing the chance of detection.