ScarCruft (APT37) Ruby Jumper Campaign Targets Air-Gapped Systems via Zoho WorkDrive C2 and USB Malware
Threat Actor Intelligence · 3 sources · Updated 4mo ago · First seen Feb 27, 2026
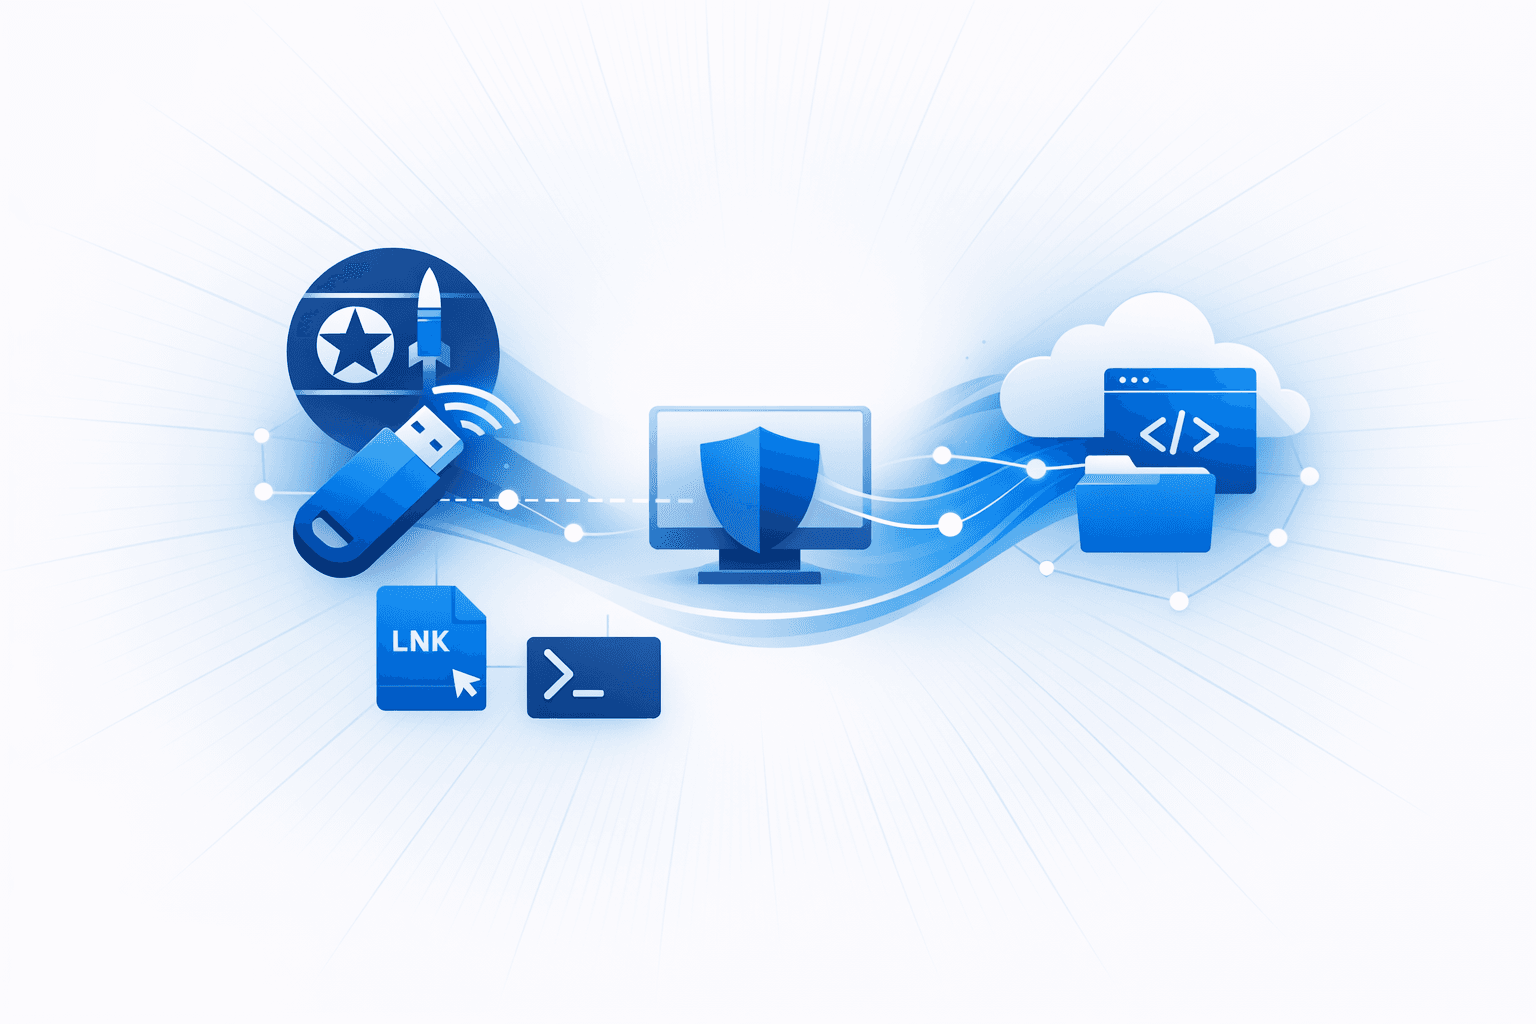
North Korea-linked ScarCruft (APT37) has been attributed to a new espionage campaign dubbed Ruby Jumper that is designed to compromise air-gapped environments using a multi-stage infection chain and removable media. Zscaler ThreatLabz reported the activity was identified in December 2025 and described an initial access method that relies on a malicious Windows shortcut (.LNK); when opened, it triggers PowerShell to extract multiple embedded payloads (including a decoy document and staged scripts/binaries) from fixed offsets within the LNK and then decrypts and executes follow-on code in memory.
The toolset includes multiple malware components—reported as RESTLEAF, SNAKEDROPPER, THUMBSBD, VIRUSTASK, FOOTWINE (and additionally BLUELIGHT in one account)—used to progress execution, establish persistence, and enable surveillance. RESTLEAF was described as using Zoho WorkDrive for command-and-control, authenticating with a valid access token and downloading additional shellcode for execution (including via process injection), representing a noted shift to abusing a cloud storage service for C2; the campaign also includes an implant/workflow that uses removable media (USB) to relay commands and bridge isolated networks, enabling compromise of systems without direct internet connectivity.