Phishing Campaigns Abuse Trusted Branding and Cloud Hosting to Steal Credentials
Social Engineering & Fraud · 2 sources · Updated 5mo ago · First seen Mar 4, 2026
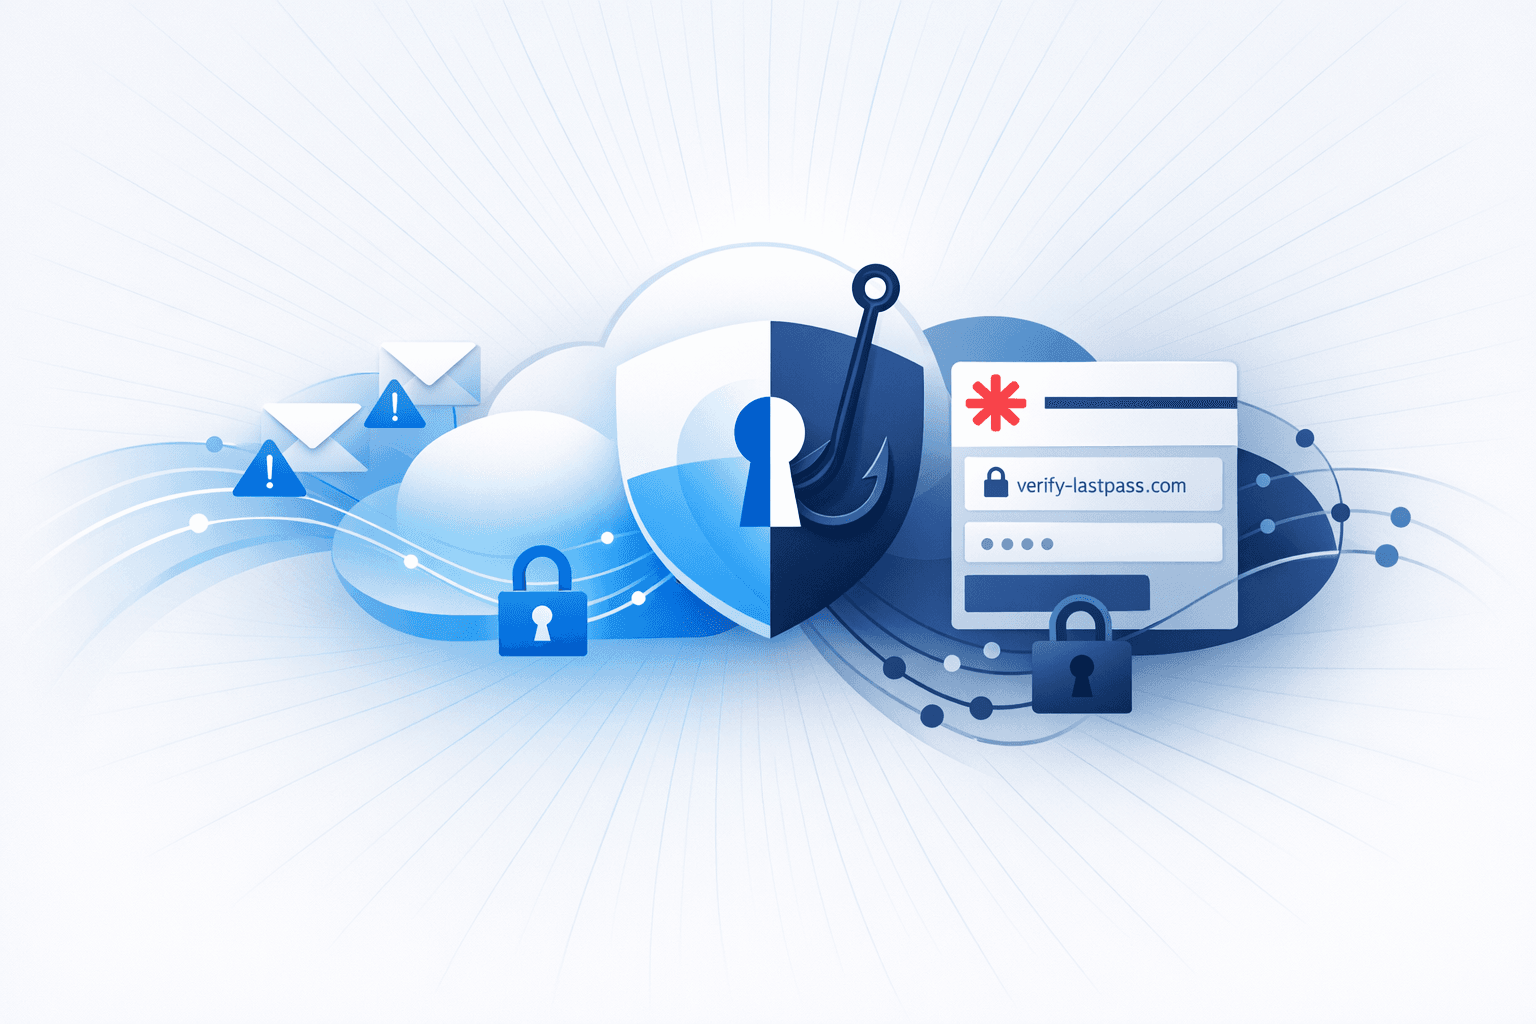
LastPass warned customers about an active phishing campaign using spoofed “security alert” emails that claim unauthorized access, vault export attempts, account recovery, or new device registration to pressure users into taking action. The messages spoof the LastPass display name (relying on many clients—especially mobile—showing only the display name) and direct victims to a fake SSO login page at verify-lastpass[.]com to steal credentials; LastPass reiterated it will never ask for a user’s master password and said it is working with partners to take down the phishing infrastructure.
Separately, researchers reported a coordinated phishing operation that abuses Google Cloud Storage (GCS) to host redirector content on a legitimate Google domain (storage.googleapis.com) to help links evade email security controls. Analysis tied 25+ distinct lure emails (e.g., “storage full,” “antivirus expired,” and brand-themed reward scams) to a single GCS bucket (whilewait) hosting comessuccess.html, which functions as a gatekeeper/redirector that forwards victims to third-party malicious sites associated with credential and/or payment-card harvesting and potential malware delivery; the consistent destination across varied themes indicates centralized attacker-controlled cloud infrastructure.