BeatBanker Android Malware Campaign Impersonating Starlink and Government Apps
Social Engineering & Fraud · 7 sources · Updated 5mo ago · First seen Mar 11, 2026
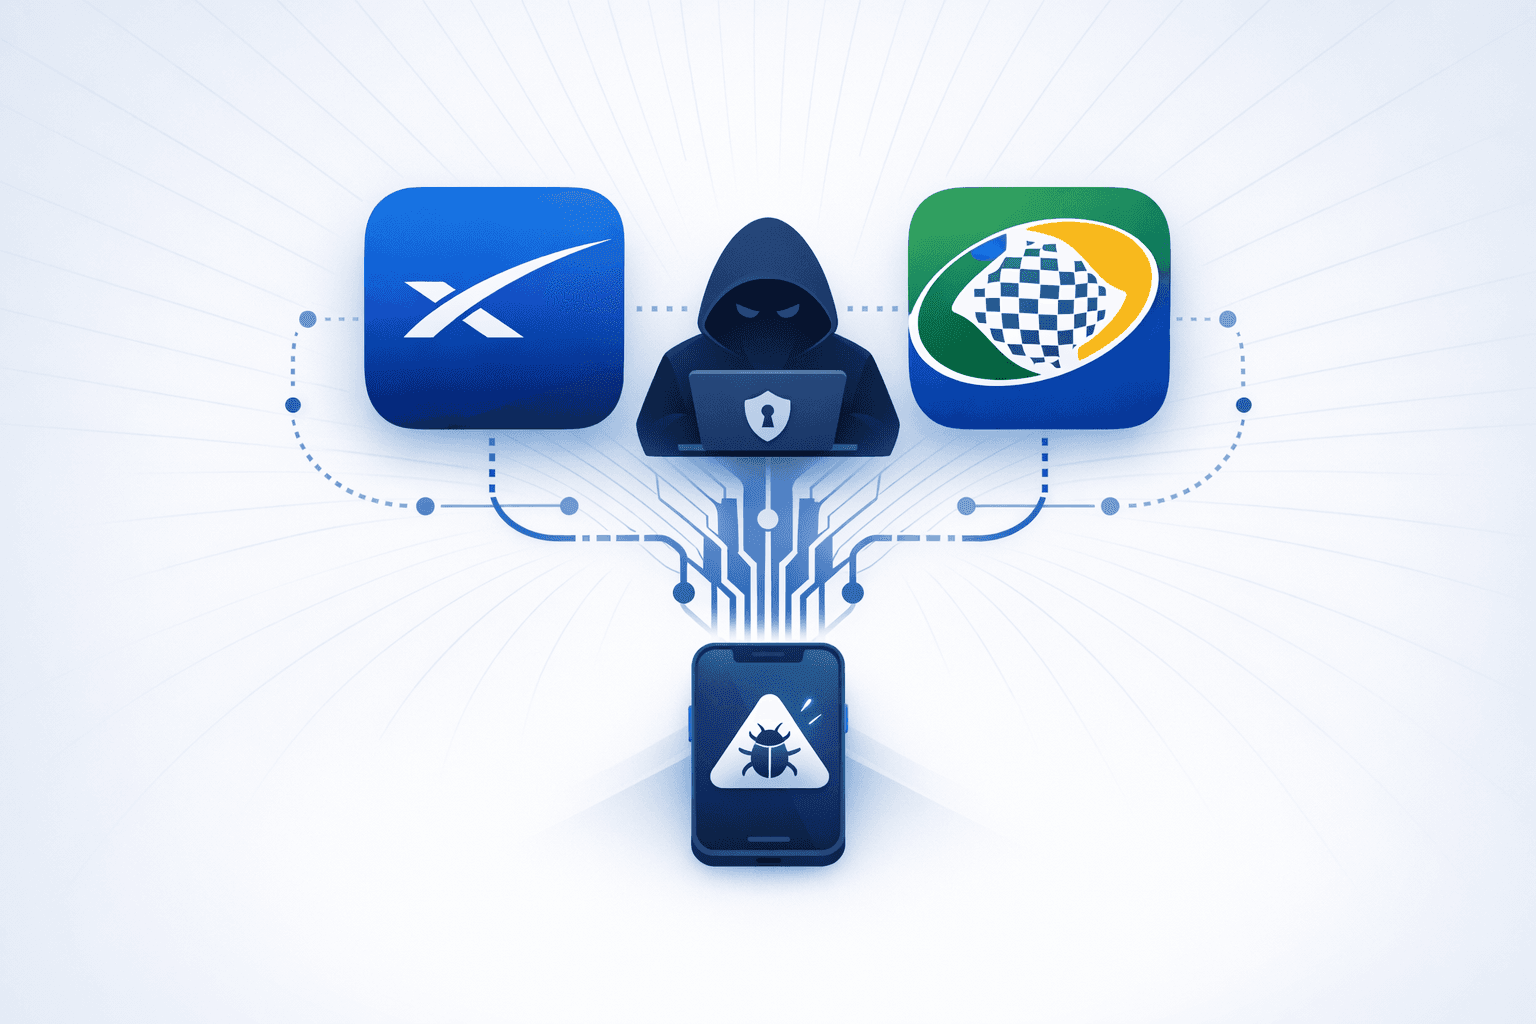
Kaspersky reported a new Android malware campaign dubbed BeatBanker targeting users in Brazil, distributed via phishing sites that closely mimic the Google Play Store and lure victims into installing trojanized APKs posing as legitimate apps such as Starlink and the Brazilian government services app INSS Reembolso. The infection chain is staged to reduce suspicion: an initial decoy app presents a fake in-app “update” flow that prompts users to grant permission to install additional apps/modules, after which the malware pulls down further payloads and requests expanded privileges.
Technical reporting indicates BeatBanker blends banking trojan capabilities with cryptomining (including a modified XMRig), and newer variants may deploy the commodity Android RAT BTMOB in place of the banking module, enabling broad device takeover (e.g., keylogging, screen recording, camera access, GPS tracking, and credential capture). The malware uses evasion techniques such as decrypting and loading hidden DEX code in-memory, performing anti-analysis environment checks, delaying malicious actions post-install, and maintaining persistence by continuously playing a near-inaudible MP3 (output8.mp3) to keep a foreground service alive and reduce the likelihood of the process being suspended by Android power management.