
Loading story…
Infoblox reported that the VexTrio cybercriminal network operated a large traffic distribution and scam-enablement ecosystem that relied on DNS manipulation, compromised routers, and hosting infrastructure to steer victims to malicious content. The reporting links VexTrio to Savvy Seahorse, a campaign that used Facebook ads and fake investment brands to lure users onto fraudulent trading platforms, with DNS services helping conceal the underlying infrastructure and redirect traffic through intermediary domains and systems.
A later Infoblox investigation said the operation also leveraged compromised SOHO routers, a traffic distribution system (TDS), and infrastructure associated with Aeza Networks to mask backend services and route victims based on geography, device, or campaign logic. Together, the findings describe a resilient criminal ecosystem that blended ad-driven social engineering with covert DNS and network-layer redirection to support investment fraud and other malicious web operations at scale.
TTPs, infrastructure, and targeting history in one profile.
5 events from the most recent confirmed update back to the earliest known activity.
Infoblox reported on a traffic distribution system hidden in Aeza Networks infrastructure and tied it to compromised routers and DNS abuse. The publication revealed additional technical details about the infrastructure supporting malicious traffic routing.
Infoblox published a threat-intelligence profile describing VexTrio as a large cybercriminal network. The report consolidated public technical details about the group's infrastructure and role in malicious online activity.
Infoblox published research examining how malicious traffic distribution systems route victims from initial clicks to harmful destinations. The report publicly documented TDS techniques and infrastructure used to steer users into cybercriminal activity.
The Five Eyes governments released a joint cybersecurity advisory on the Chinese state-sponsored threat actor Volt Typhoon, detailing its activity and tradecraft. The advisory marked a coordinated public warning and attribution effort by allied authorities.
Infoblox published research on the Savvy Seahorse operation, describing how the threat actor used Facebook ads and DNS infrastructure to lure victims to fraudulent investment platforms. The report publicly exposed the campaign's social engineering and infrastructure tactics.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
5 references tracked. Mallory keeps watching after this page renders.
blogs.infoblox.com
Open sourceinfoblox.com
Open sourceinfoblox.com
Open sourceinfoblox.com
Open sourceinfoblox.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Researchers from Confiant, Infoblox, and Netskope reported sustained criminal abuse of traffic distribution systems (TDSs) to filter, cloak, and route victims into scams and malware. Confiant and Infoblox found that attackers have extensively weaponized **Keitaro**, a self-hosted ad-tracking platform, across an ecosystem of roughly **15,500 malicious domains**, including about **9,000** registered specifically for abuse. Their four-month analysis found traffic arriving from programmatic ads, spam, social media, and compromised websites, then being selectively redirected based on device, geography, IP address, and referrer. Investment fraud was the dominant use case, with clusters such as **FaiKast** using deepfake news-style cryptocurrency ads, **WickedWally** targeting U.S. seniors with fake benefits and debt-relief offers, and **FishSteaks** running giveaway scams impersonating consumer brands. Netskope separately documented a parallel TDS-for-hire operation built around more than **12,700** fake CAPTCHA PDF files hosted on Webflow’s CDN and indexed by Google as benign upgrade guides. Those PDFs fed users into a custom **Elixir/Phoenix** routing platform that screened visitors through IP reputation, bot detection, geography, and device checks before sending qualified victims to malware or scam pages and diverting others to ad-arbitrage content. The downstream payloads included **Legion Loader**, a reseller TDS gate linked to `yfdpco` domains, and a Spanish-language premium-SMS fraud scheme. Researchers said the infrastructure has persisted for more than 14 months despite rotating lure domains, underscoring how commercial-style tracking and routing software is being repurposed at scale to industrialize online fraud and malware delivery.
Aug 6, 2026
Infoblox researchers reported a widespread **DNS hijacking** campaign targeting **outdated consumer/home routers** across **more than three dozen countries**, where attackers compromise devices and change router-level DNS settings to silently redirect all connected users’ traffic. The manipulated DNS queries are sent to malicious resolvers hosted by **Aeza International**, a **Russian bulletproof hosting provider** that the US sanctioned in **July 2025**, allowing threat actors to control where victims are routed while keeping common destinations working to reduce suspicion. The infrastructure reportedly uses a **two-stage redirection chain**: DNS traffic is forwarded into an **HTTP-based Traffic Distribution System (TDS)** that first verifies the request originates from a compromised router and then fingerprints/filters victims before sending them onward—often into **advertising/affiliate networks** that can lead to **scams or malicious sites**. Analysts also described an evasion behavior where the rogue resolvers may only respond under specific query conditions (e.g., when **EDNS0** is disabled), complicating reproduction and detection; user-visible symptoms included selective site failures and persistent redirects that victims often misattributed to endpoints rather than the router.
Jun 29, 2026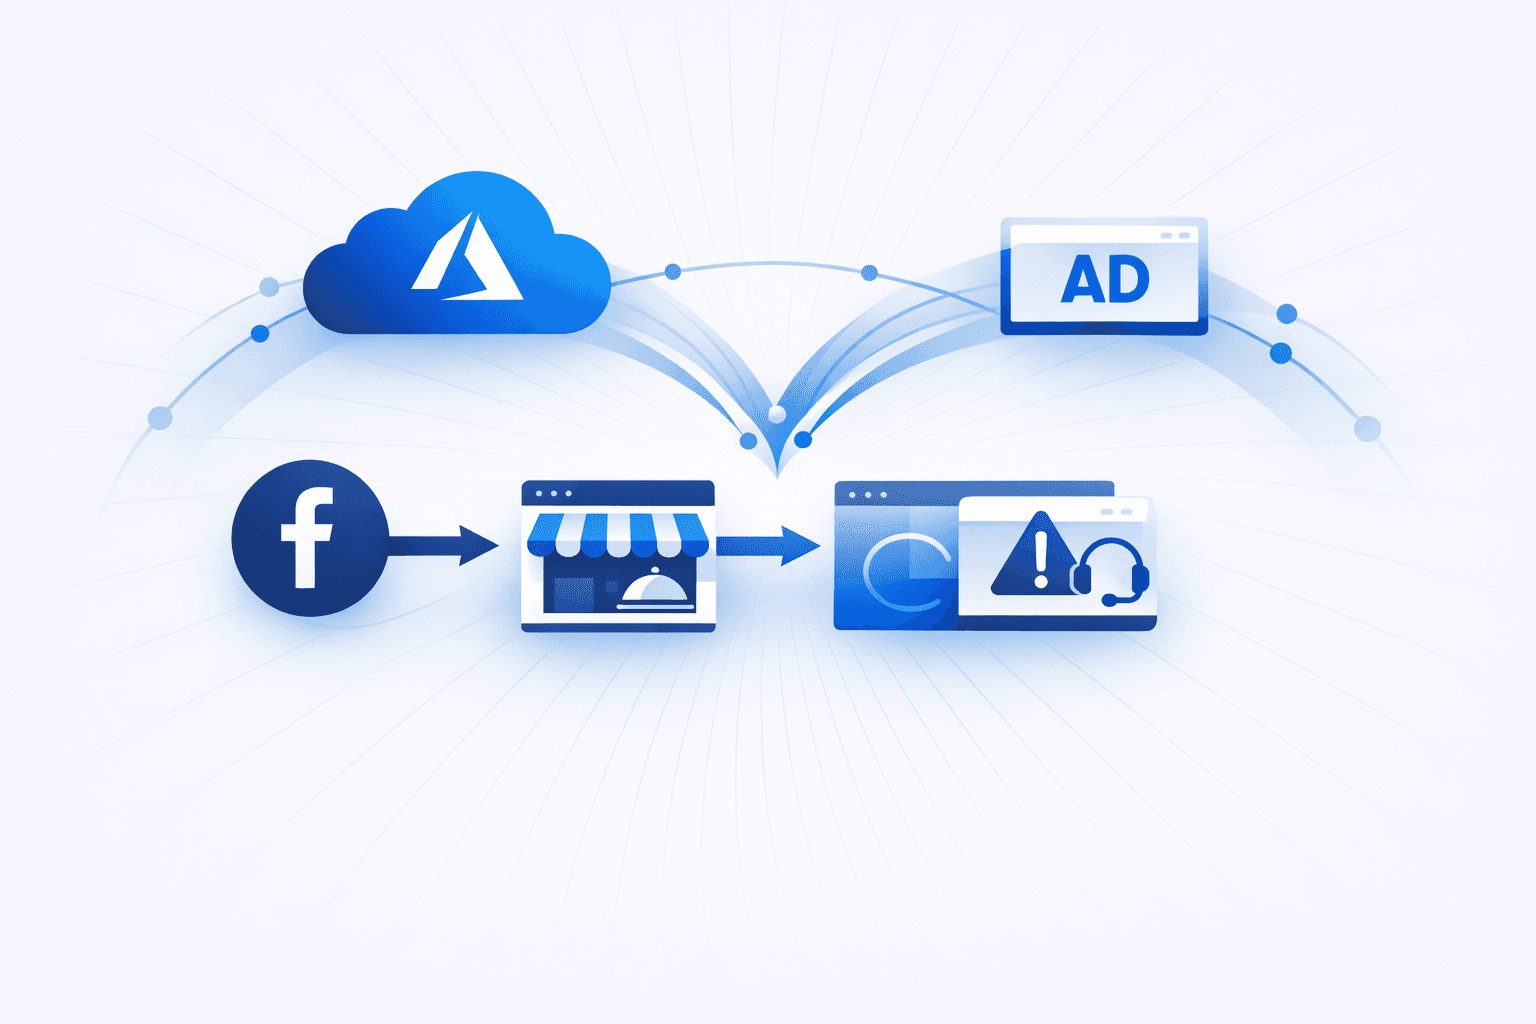
Threat actors are increasingly using **trusted platforms**—including cloud hosting and major ad networks—to deliver multi-stage phishing and scam campaigns that evade traditional URL and domain reputation controls. Recent activity includes a **three-step malvertising chain** delivered via **Facebook paid ads** that redirects victims through a decoy site (e.g., a fake Italian restaurant page) before landing on a **tech support scam (TSS) kit** hosted on **Microsoft Azure** infrastructure (including `web.core.windows.net`). Researchers reported rapid infrastructure churn, with **100+ domains rotated in seven days**, and targeting focused on **U.S. users** with activity concentrated on weekdays. Parallel enterprise-focused campaigns are hosting phishing infrastructure on **Microsoft Azure Blob Storage**, **Google Firebase**, and **AWS CloudFront**, using **redirect chains, CAPTCHA gates, and QR codes** to bypass automated analysis and email defenses. Analysis highlighted the use of **Adversary-in-the-Middle (AiTM)** phishing-as-a-service kits—**Tycoon2FA**, **Sneaky2FA**, and **EvilProxy**—to steal credentials and **session tokens** even when MFA is enabled. Separately, researchers documented a “clean email” approach to steal **Dropbox** credentials: benign-looking procurement-themed emails deliver **PDF attachments** that hide clickable elements (e.g., via *AcroForms* and `FlateDecode`), which then route victims to a second-stage file hosted on **Vercel Blob** and ultimately to a fake Dropbox login page that captures credentials and collects victim telemetry (IP address, location, and device details).
Jun 29, 2026