
Loading story…
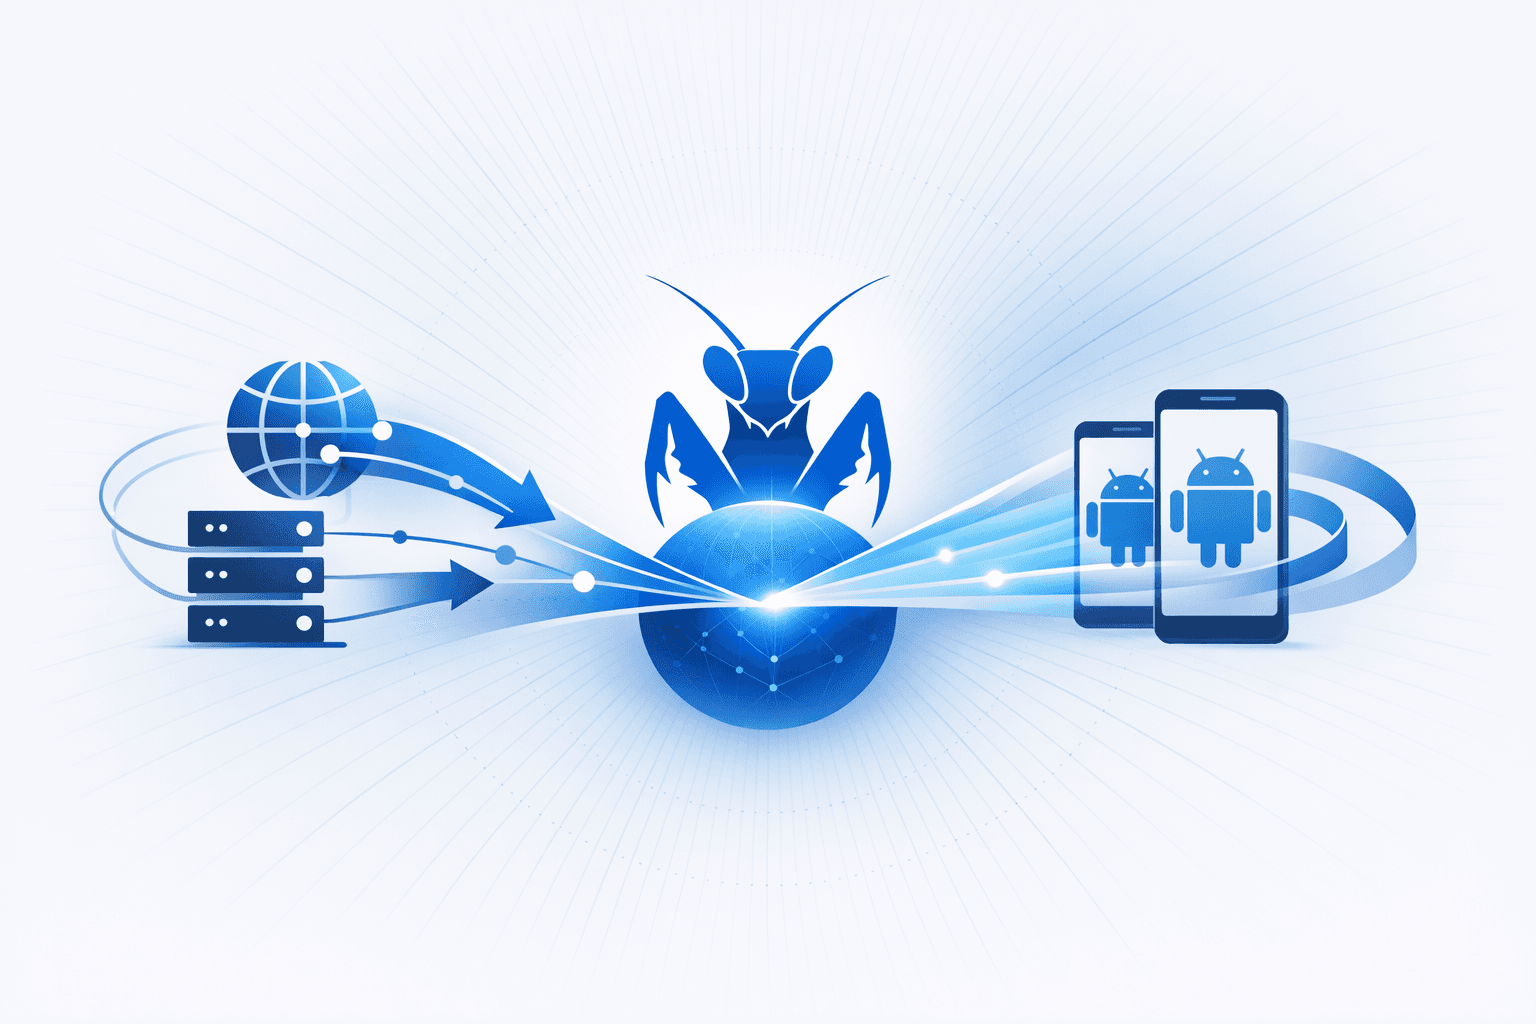
Researchers reported that the Roaming Mantis campaign hijacked DNS settings on compromised routers and redirected users to malicious landing pages that pushed Android malware. Victims who attempted to browse the web while connected to affected networks were instead shown fake update prompts, allowing the attackers to install malware on Android devices and potentially harvest credentials and other sensitive data.
The operation stood out because it abused home and small-office networking infrastructure rather than relying solely on phishing or malicious apps. By tampering with router DNS configurations, the attackers were able to intercept traffic at the network level and selectively deliver malicious content to mobile users, expanding the reach of the campaign and demonstrating how router compromise can be used to spread malware across connected devices.
See affected versions and whether adversaries are exploiting it.
1 event from the most recent confirmed update back to the earliest known activity.
Securelist published research describing the Roaming Mantis campaign using DNS hijacking to redirect users and infect Android smartphones. The report identified the campaign as an active mobile threat affecting users through compromised network infrastructure.
See whether adversaries are exploiting this yet, and where the affected versions run in your environment.
1 reference tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.

Roaming Mantis continued to expand its **MoqHao** Android malware operation—also tracked as **Wroba** and **XLoader**—using smishing messages, fake courier-themed apps, and region-specific landing pages to steal device data, credentials, and support financially motivated fraud. Researchers reported that the campaign evolved its delivery and evasion methods with allowlist-based download pages in South Korea, Multidex obfuscation, SMS-spamming automation, and phishing redirects aimed at Japanese online banking and carrier-billing accounts. The operation also added a **DNS changer** capability that targeted Wi-Fi routers commonly used in South Korea, allowing attackers to alter DNS settings and redirect users on affected networks to malicious pages. Infrastructure analysis identified **14 command-and-control servers**, while telemetry showed nearly **1.5 million** victim communications from **67 countries** since late 2022, with the heaviest activity still concentrated in East Asia—especially Japan—even as infections and APK downloads were observed across Europe, Africa, the Middle East, Oceania, and the Americas.
Aug 15, 2026
Researchers reported that **Trojan.AndroidOS.Switcher** infected Android devices and then pivoted to nearby Wi-Fi routers, brute-forcing the router web administration interface instead of directly targeting the phone owner. The malware primarily targeted **TP-LINK** devices and was distributed through fake Android apps, including a counterfeit **Baidu** client and a bogus Wi-Fi sharing application, while an associated website also functioned as command-and-control infrastructure. After gaining router access, the malware changed DNS settings to attacker-controlled servers, enabling **DNS hijacking** for all devices using the compromised network. The trojan selected one of three rogue DNS servers based on the victim’s ISP, reported activation and successful compromise to its C2, and set `8.8.8.8` as a secondary resolver for resilience; exposed attacker statistics claimed **1,280 Wi-Fi networks** had been infiltrated. Researchers warned that the malicious DNS settings could survive router reboots and advised users to check for rogue DNS entries and replace default router administrator credentials.
Aug 14, 2026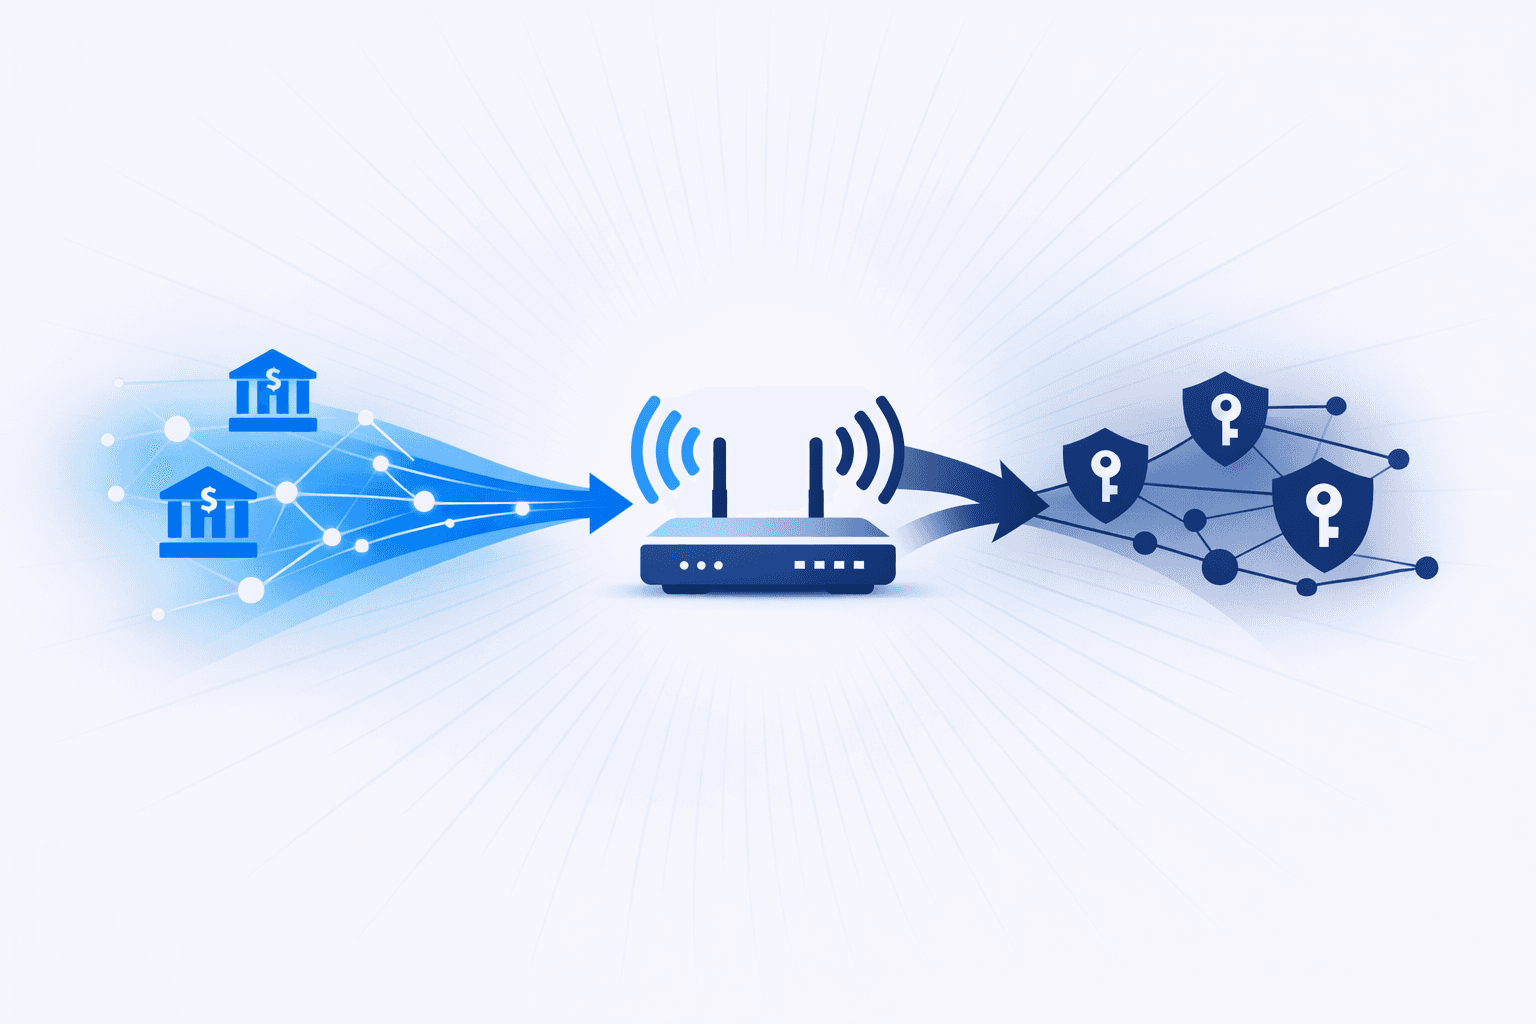
Researchers detailed the **GhostDNS** operation, a DNS-hijacking toolkit that compromised poorly secured SOHO and home routers in Brazil to redirect victims to phishing pages for banks and other services. The leaked source code showed a mature kit with versions dating back to 2017, including phishing templates, rogue DNS configurations, and tooling to alter router settings through **CSRF** requests and brute-forced default credentials. In some cases, the malware reset router passwords to attacker-controlled values such as `deadcorp2017` and `Snowden`, giving operators persistent access to infected devices. Separate analysis tied the campaign to malvertising that redirected Brazilian users from legitimate sites through attacker infrastructure, including domains such as `googleads.store`, to scripts that probed common private gateway addresses and attempted DNS changes across multiple router models. Once a router's DNS settings were changed, victims were sent to counterfeit banking portals, including fake **Banco do Brasil** pages, where attackers harvested login credentials and payment card data. The reporting indicates the campaign was heavily concentrated in Brazil, where weak default router passwords remained common, and that the operation extended into a broader criminal market selling both the toolkit and stolen financial data.
Aug 15, 2026