PetitPotam and AD CS Misconfigurations Enable Full Windows Domain Compromise
Vulnerability Disclosure · 4 sources · Updated 5mo ago · First seen May 25, 2026
Researchers and defenders warned that Active Directory Certificate Services (AD CS) can be abused to take over Windows domains through a combination of certificate misconfigurations and NTLM relay paths. SpecterOps documented multiple escalation techniques in its Certified Pre-Owned research, including vulnerable certificate templates, arbitrary Subject Alternative Name abuse, weak access controls, and relay attacks against AD CS web enrollment endpoints. The findings showed that attackers can obtain certificates usable for PKINIT or Schannel authentication, enabling privilege escalation, persistence that survives password resets, and in some cases creation of forged "golden certificates" if a CA private key is stolen.
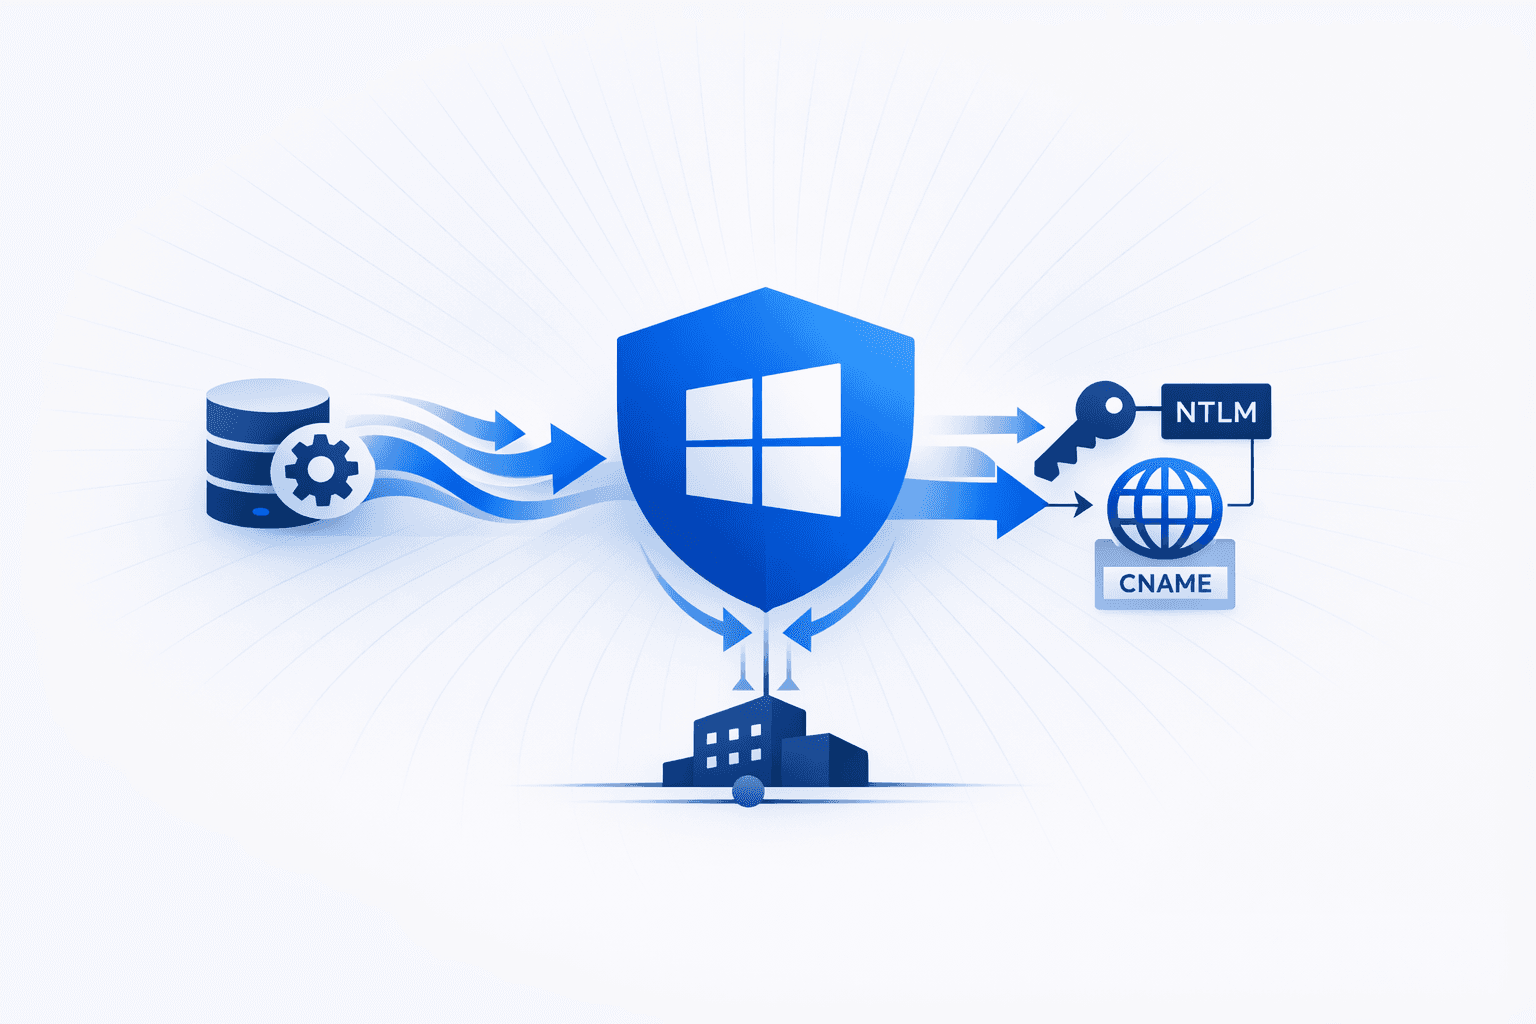
The risk became more urgent as the PetitPotam attack chain demonstrated how coercing NTLM authentication from a domain controller and relaying it to AD CS could lead to complete domain compromise. SANS highlighted the issue as a path to domain admin, while Microsoft published advisory ADV210003 with mitigations rather than a security patch, recommending steps such as enabling Extended Protection for Authentication, requiring HTTPS on certificate enrollment endpoints, and reducing or disabling NTLM where possible. The combined disclosures showed that widely deployed AD CS environments could become a direct route to full Active Directory takeover if left misconfigured.