Microsoft Details AD CS Hardening Against PetitPotam NTLM Relay Attacks
Vulnerability Disclosure · 6 sources · Updated 7d ago · First seen Dec 8, 2009
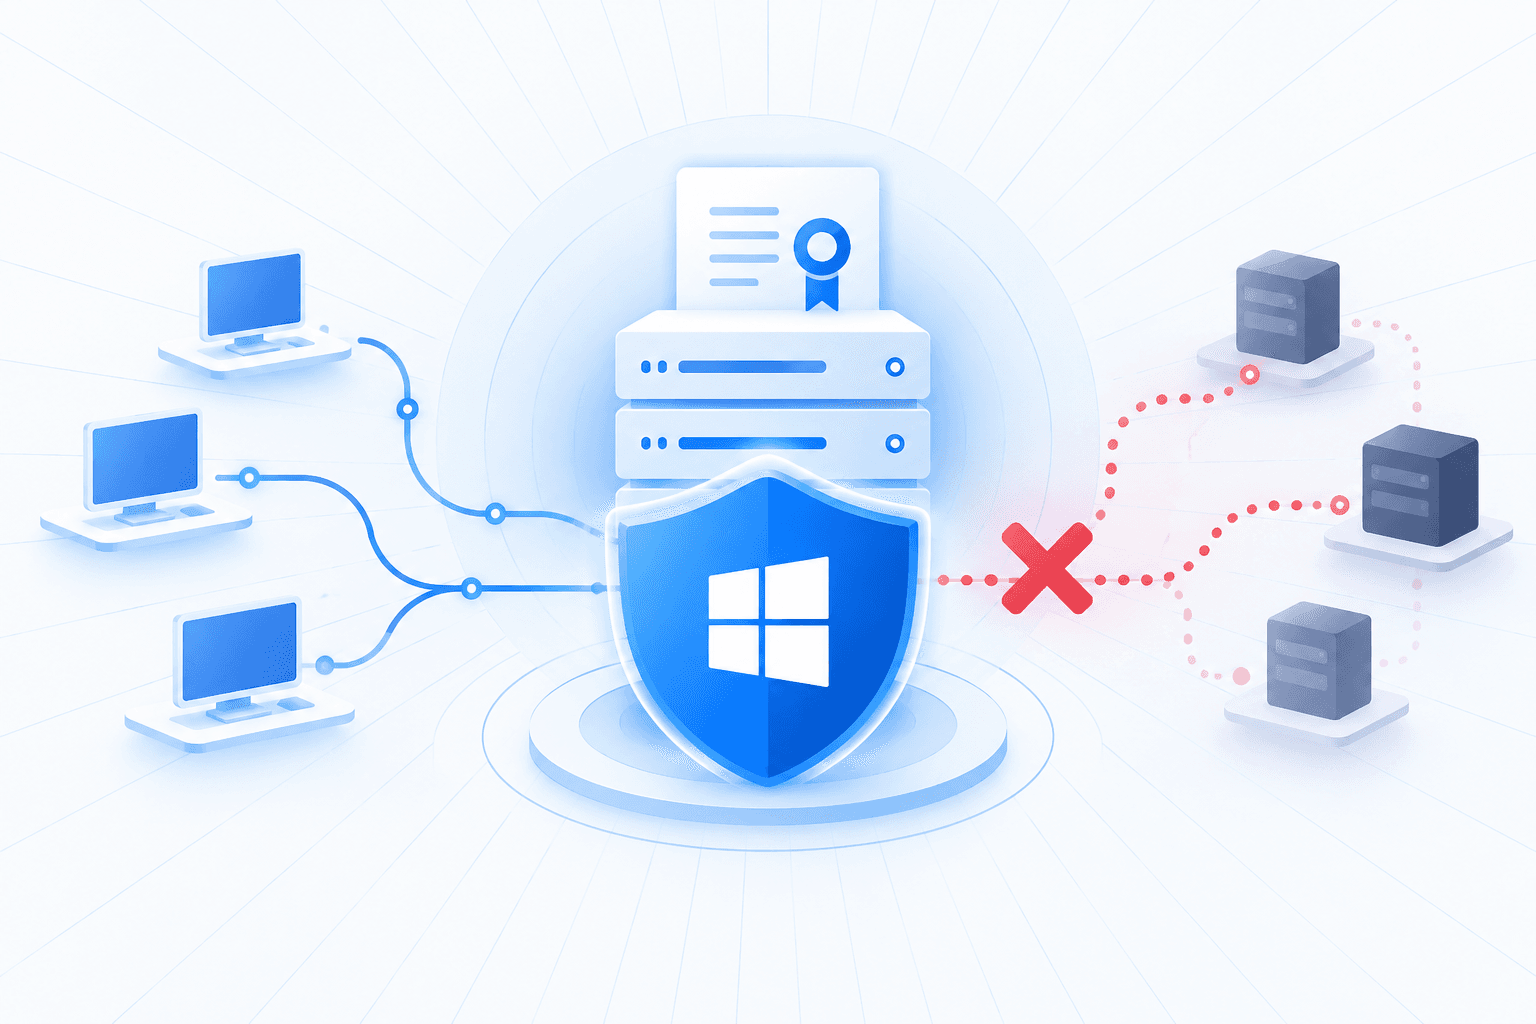
Microsoft’s KB5005413 guidance identifies Active Directory Certificate Services (AD CS) deployments as potentially vulnerable to PetitPotam NTLM relay attacks when Certificate Authority Web Enrollment or Certificate Enrollment Web Service lacks relay protections. Such attacks can target Windows domain controllers and other servers by forwarding authentication exchanges to another service and impersonating the authenticating client, without recovering the plaintext password. Microsoft recommends enabling Extended Protection for Authentication (EPA), requiring HTTPS, and disabling HTTP on affected AD CS servers. EPA validates the intended authentication destination and, when TLS is present, binds authentication to the TLS channel to reject relayed exchanges.
Administrators should verify EPA enforcement across IIS and applicable enrollment-service configurations rather than relying on HTTPS alone; Microsoft’s .NET documentation exposes explicit enforcement settings, including a setting that disables protection. Additional defenses include restricting or disabling NTLM at the domain, AD CS server, or IIS service level. Microsoft recommends auditing incoming NTLM usage before enforcing restrictions, reviewing operational logs to identify dependent applications and planning any necessary exceptions. Unconfigured incoming-NTLM policy permits authentication, while restrictive settings can block domain accounts or all accounts, making compatibility assessment important before rollout.