Microsoft OAuth Device Code Phishing Hijacks Microsoft 365 Sessions
Social Engineering & Fraud · 1 source · Updated 4mo ago · First seen Jun 2, 2026
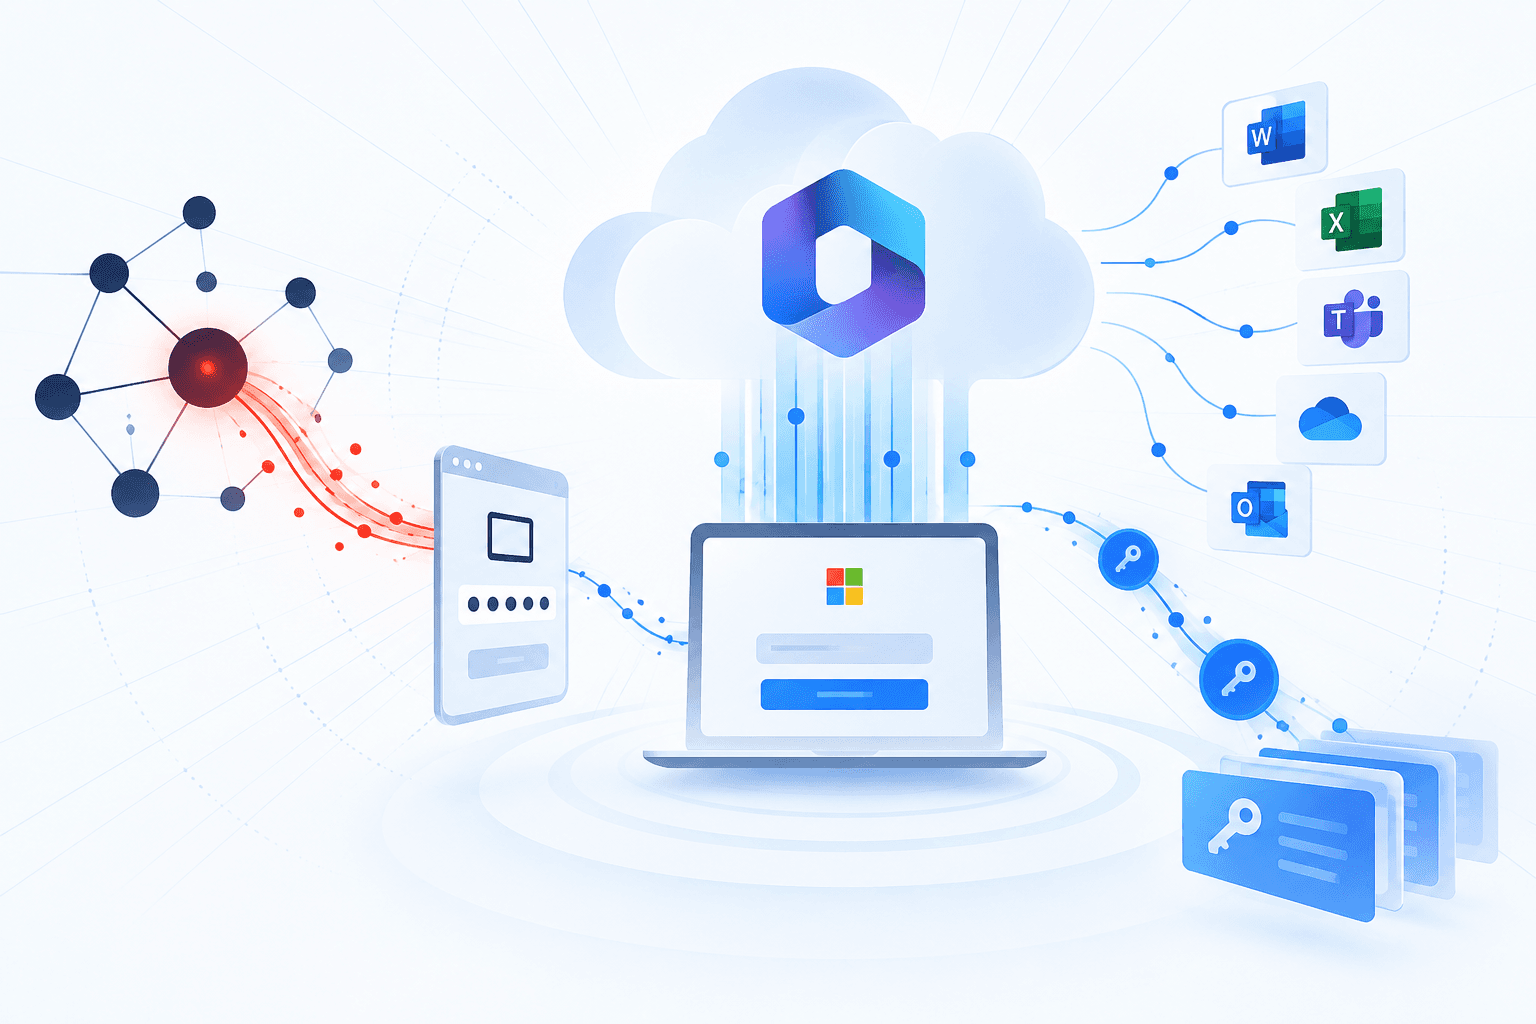
Attackers abused Microsoft’s OAuth 2.0 Device Authorization Grant flow to phish users into authorizing attacker-controlled sessions on legitimate Microsoft login pages, allowing them to capture access tokens, refresh tokens, and ID tokens without stealing passwords directly. In the observed campaign, victims received phishing emails, were routed through phishing landing pages and open redirects, and were told to enter attacker-supplied one-time device codes on Microsoft’s official device verification page before completing MFA.
The stolen tokens enabled access to Microsoft 365 services including email, OneDrive, and Teams. Researchers also observed a Brazil-focused variant that used cacoo.com, a legitimate Nulab-owned service, as an open redirect to phishing infrastructure. Recommended mitigations include training users to reject unsolicited device-code requests, reviewing redirect parameters and final destinations, monitoring DeviceCodeSignIn events, enforcing device-compliance controls, and disabling Device Code Flow in Microsoft Entra ID where it is not required.