Microsoft Device Code Phishing Abused Legitimate Login to Steal OAuth Tokens
Social Engineering & Fraud · 6 sources · Updated 4mo ago · First seen Jul 6, 2026
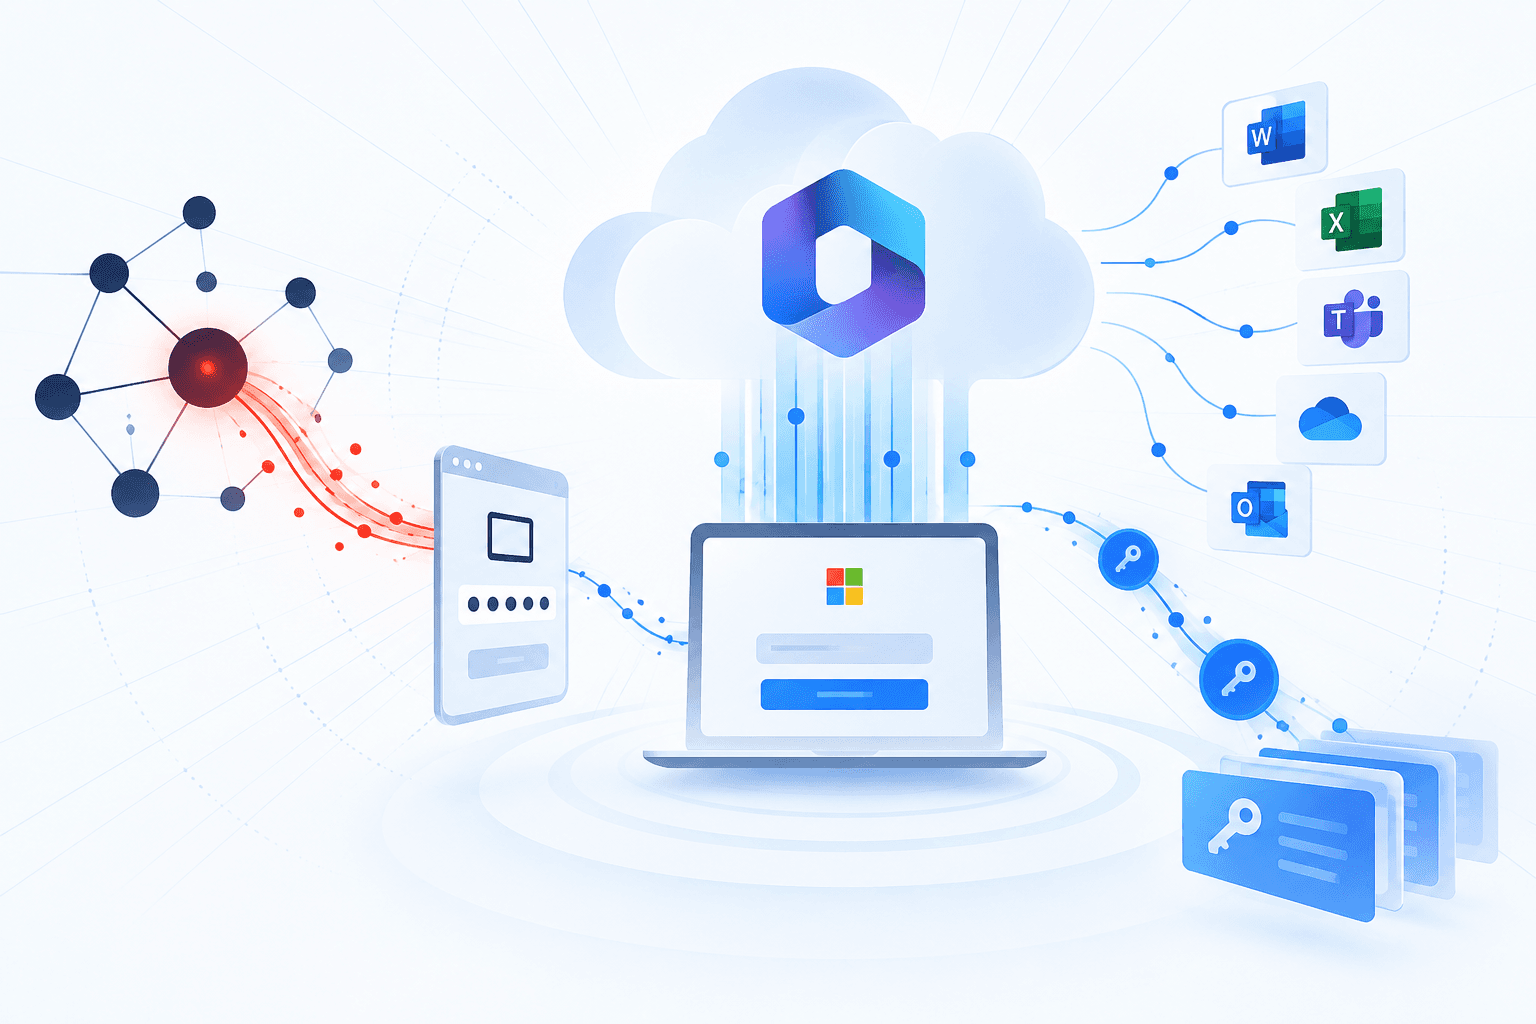
A phishing campaign abused Microsoft's OAuth 2.0 Device Authorization Grant (Device Code Flow) to capture valid Microsoft account tokens without sending victims to a counterfeit login page. Victims received emails posing as legal notifications, including password-protected PDF attachments, and were funneled through phishing pages that displayed a one-time device code before directing them to the legitimate microsoft.com/devicelogin page. After victims entered the code and completed normal MFA on Microsoft's real site, the attackers obtained access_token, refresh_token, and id_token values tied to attacker-controlled applications.
The stolen tokens enabled persistent access to Microsoft services including email, OneDrive, and Teams, allowing attackers to read messages, access files, and monitor conversations. Researchers said the activity was observed from early April to mid-May 2026 and included a Brazil-focused variant that used legitimate redirect links, including on cacoo.com, to add credibility to the lure chain. Defenders were urged to reject unexpected device authorization prompts, inspect redirect parameters in otherwise legitimate URLs, disable Device Code Flow in Microsoft Entra ID where it is not needed, and monitor DeviceCodeSignIn and anomalous sign-in activity for signs of compromise.