Mallory
← Back to News
phishing-campaign-intelligenceidentity-authentication-vulnerabilitycredential-access-methodpersistence-method

Device-Code Phishing Abuses Legitimate OAuth Sign-In to Steal Microsoft 365 Tokens

Social Engineering & Fraud · 4 sources · Updated 2mo ago · First seen Sep 22, 2026
Device-Code Phishing Abuses Legitimate OAuth Sign-In to Steal Microsoft 365 Tokens

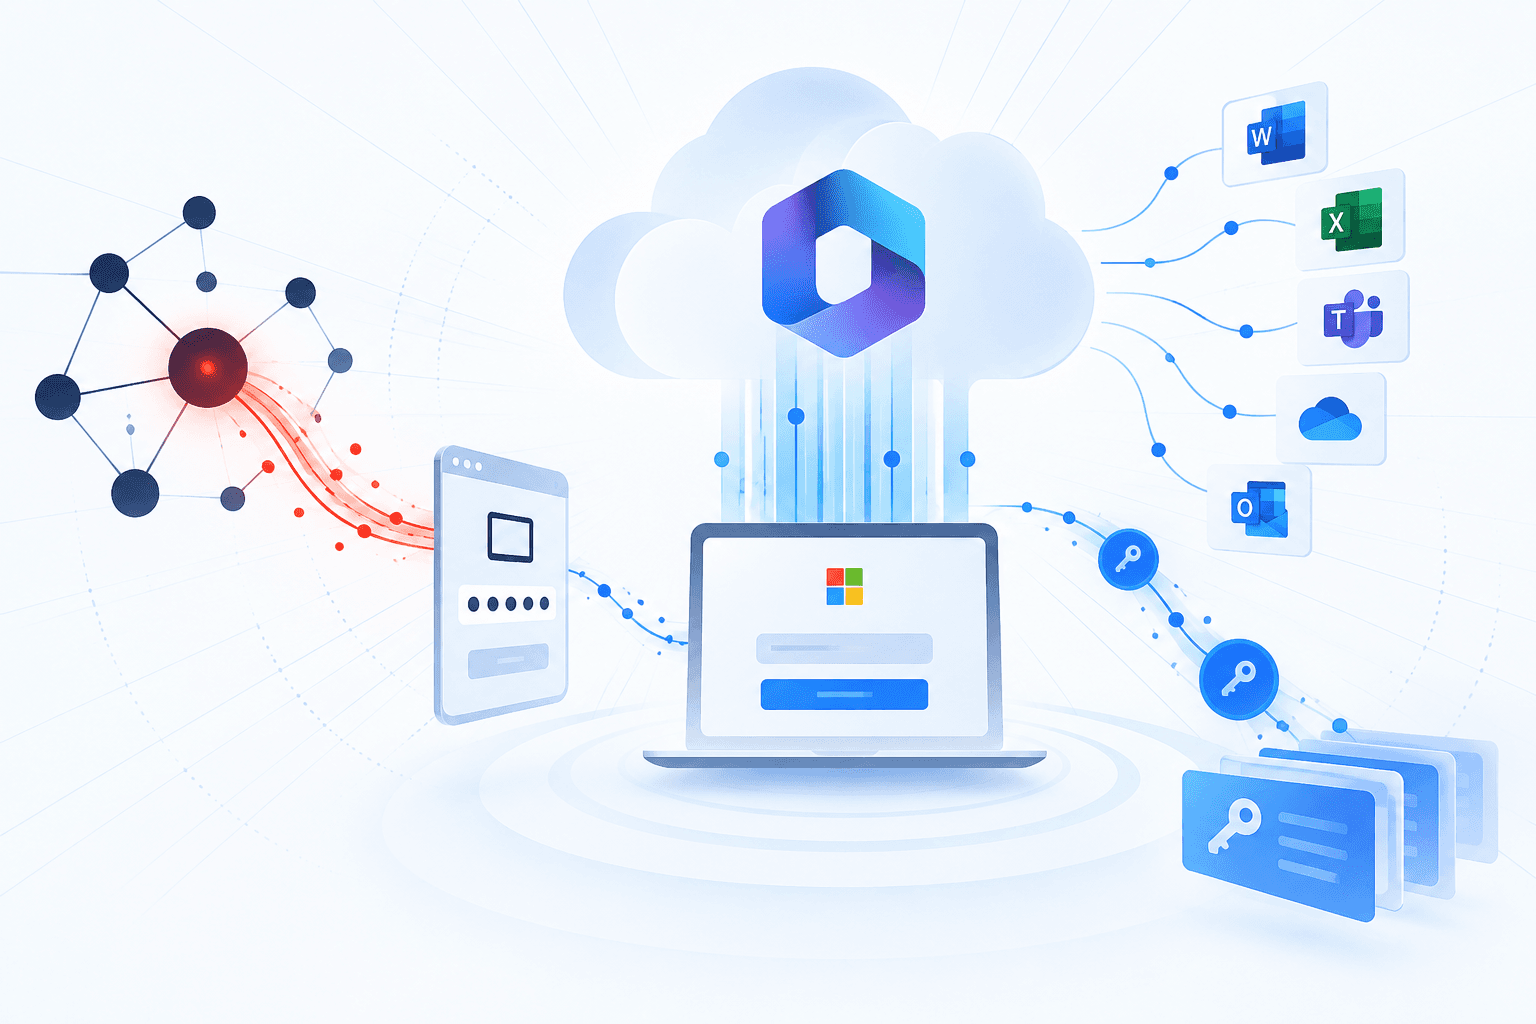
Attackers are abusing the OAuth 2.0 Device Authorization Grant to obtain Microsoft 365 account tokens without stealing passwords. They initiate a legitimate device-code sign-in on an attacker-controlled application or device, then persuade targets through meeting, document-sharing, chat, or security-themed lures to enter the supplied temporary code on a genuine Microsoft sign-in page. Because victims complete the authentication and consent themselves, URL checks and MFA may not stop the attack; the resulting tokens can expose email, files, contacts, and other authorized services.

Post-authentication activity can include device registration or Primary Refresh Token issuance, Microsoft Graph queries, mailbox access, and Exchange inbox rules that hide alerts or forward data externally. Defenders should correlate phishing delivery and click telemetry with device-code sign-ins, new-device events, Graph activity, and mailbox-rule changes; contain confirmed incidents by revoking sessions and refresh tokens, disabling unrecognized devices, removing malicious rules, and assessing accessed data. Microsoft recommends blocking device-code flow by default with Entra Conditional Access, first in report-only mode, while maintaining tightly scoped persistent exceptions for legitimate Teams resource accounts and excluding the Device Registration Service where required for enrollment.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

3 events
  1. Reported Sep 23, 20262mo ago

    Device-code phishing technique and EvilTokens support documented

    Reports describe attackers initiating legitimate OAuth 2.0 Device Authorization Grant sessions and socially engineering victims to enter attacker-supplied codes on genuine sign-in pages, thereby issuing account tokens to attacker-controlled devices. The reports identify EvilTokens as a phishing kit supporting this technique and note that victim-completed MFA may not prevent it.

    How device code phishing gives scammers access to your account - Malware News - Malware Analysis, News and Indicators
  2. Reported Sep 23, 20262mo ago

    Post-compromise Microsoft 365 activity pattern documented

    A Microsoft 365 device-code phishing sequence was described in which stolen tokens can be used to register devices, query Microsoft Graph, access email, and create mailbox rules to conceal activity or forward data. The post recommends correlating phishing delivery with device-code authentication, subsequent device or PRT issuance, Graph activity, and mailbox-rule changes.

    Device Code no Microsoft 365: o que correlacionar depois do login legítimo : r/sysadmin
  3. Reported May 28, 20266mo ago

    Microsoft publishes Conditional Access guidance to block device code flow

    Microsoft recommends blocking device code flow by default with Microsoft Entra Conditional Access, using narrowly scoped persistent exceptions for legitimate Teams device resource accounts and excluding the Device Registration Service. It advises report-only deployment, sign-in-log review, and continuous auditing of exceptions and unexpected usage.

    Restrict device code flow for Microsoft Teams devices with Conditional Access - Microsoft Entra ID | Microsoft Learn
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →

Affected products

1 linked
Microsoft 365

Organizations

1 linked
Microsoft Corporation
Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.