
Mallory
← Back to News
state-sponsored-espionageperimeter-device-exposuredefault-credential-exposuregovernment-diplomatic-threat

Allies Attribute Turla Espionage and Router Intrusions to Russia’s FSB Centre 16

Threat Actor Intelligence · 25 sources · Updated 4mo ago · First seen Jul 13, 2026

Allies Attribute Turla Espionage and Router Intrusions to Russia’s FSB Centre 16

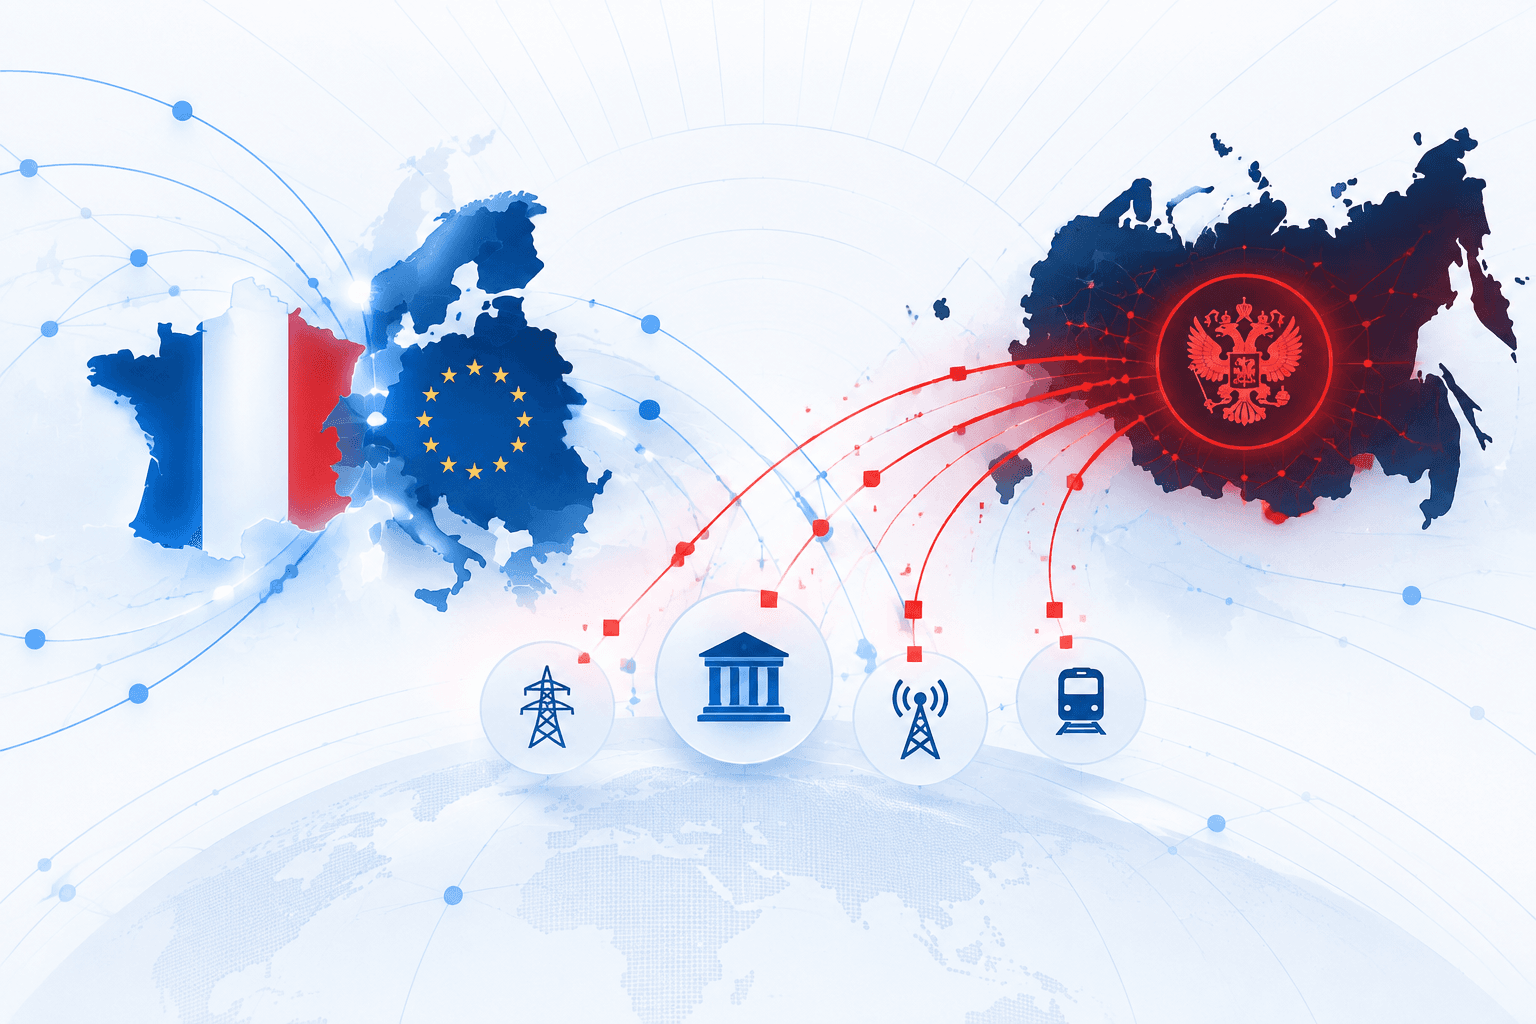
The UK, France, the EU, and partner cyber agencies publicly attributed a broad cyber-espionage campaign to FSB Centre 16, linking the Russian intelligence unit to both the long-running Turla intrusion set and active exploitation of internet-facing routers and network devices. UK and allied authorities warned that the actor is scanning globally for poorly configured infrastructure, abusing default or weak SNMP credentials and known Cisco-related weaknesses such as Smart Install and web-management flaws to seize control of devices, with critical sectors including communications, defence, energy, financial services, government, and healthcare identified as high-risk targets.

French authorities said entities in France, including ministries and organizations in the diplomatic, defence, justice, and technology sectors, were targeted and compromised using Turla tradecraft that has been active since at least 2004. The coordinated disclosures were accompanied by formal attribution statements from France and the EU, while the UK said EU member states and London also attributed the December 2025 attack on Poland’s energy grid to FSB Centre 16 and announced sanctions against 24 individuals and entities tied to Russian destructive cyber and hybrid operations. Defenders were urged to harden network devices by adopting SNMPv3, disabling legacy SNMP versions, enforcing strong unique passwords, and restricting access to management interfaces.
Know this adversaryTTPs, infrastructure, and targeting history in one profile.
Get the profile
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

16 events · Nov 1, 2021 – Jul 13, 2026
  1. Jul 13, 20264mo ago

    Turla compromises French justice-sector SharePoint server

    In 2019, French investigators said Turla compromised a justice-sector server hosting a continuing-education service by exploiting a Microsoft SharePoint-related vulnerability and installing malware. The intrusion potentially exposed information associated with several thousand user accounts.

    Turla Hackers Exploit SharePoint Flaw to Access Thousands of French User Accounts
  2. Jul 13, 20264mo ago

    CISA adds CVE-2008-4128 to KEV catalog

    On 2026-07-13, CISA added CVE-2008-4128, a Cisco IOS flaw affecting Cisco 871 Integrated Services Routers, to its Known Exploited Vulnerabilities catalog after confirming real-world exploitation. The reference ties the exploitation to actors associated with Russia's FSB Center 16 and notes the affected IOS release has been unsupported since 2016.

    CISA Adds Cisco IOS Flaw Exploited by Russian FSB Actors to KEV Catalog
  3. Jul 13, 20264mo ago

    EU sanctions Russian officers, hackers, and firms over cyber campaign

    On 2026-07-13, the European Union imposed sanctions on Russian military intelligence officers, hackers, and private companies over what it described as a yearslong cyber espionage and sabotage campaign targeting governments and critical infrastructure in at least nine countries. The EU said the network contributed to efforts to destabilize the bloc and highlighted the FSB's 16th Centre as controlling multiple threat groups.

    EU Targets Russian Intelligence Officers Accused of Running a Yearslong Cyber Spying Campaign - SecurityWeek
  4. Jul 13, 20264mo ago

    UK sanctions 24 people and entities tied to Russian cyber operations

    The NCSC notice states that the UK simultaneously sanctioned 24 individuals and entities linked to destructive cyber and hybrid operations associated with Russian intelligence services.

    UK and Allies urge critical sectors to improve defences against Russian intelligence targeting | National Cyber Security Centre
  5. Jul 13, 20264mo ago

    UK and EU member states attribute Poland grid attack to FSB Centre 16

    The NCSC said the UK and EU member states formally attributed the December 2025 attack on Poland's energy grid to FSB Centre 16 as part of coordinated public action on 13 July 2026.

    UK and Allies urge critical sectors to improve defences against Russian intelligence targeting | National Cyber Security Centre
  6. Jul 13, 20264mo ago

    UK and allies issue joint advisory on Russian targeting of network devices

    On 13 July 2026, the UK NCSC and 18 partner agencies from 12 countries issued a joint advisory warning that Russia's FSB Centre 16 is exploiting poorly configured and vulnerable routers and network devices globally, especially in critical sectors.

    UK and Allies urge critical sectors to improve defences against Russian intelligence targeting | National Cyber Security Centre
  7. Jul 13, 20264mo ago

    France and EU formally attribute Turla activity to FSB Centre 16

    On 13 July 2026, France and the European Union issued formal attribution statements regarding malicious cyber activities linked to the Turla intrusion set and attributed them to the 16th Centre of Russia's FSB.

    Rapport menaces et incidents - CERT-FR
  8. Jul 13, 20264mo ago

    France discloses Turla compromises of military email and Moscow diplomatic network

    France said the FSB-linked Turla campaign had targeted French entities for more than a decade, including French military ministry email accounts, the French diplomatic network in Moscow, technology-sector companies, an advanced-technologies entity, and a justice-sector organization. The attribution was based on investigations by ANSSI, DGSE, DGSI, the Direction générale de l’armement, and the French Cyber Defence Command.

    La veille du 14-Juillet, la diplomatie française pointe à nouveau ...
  9. Jul 13, 20264mo ago

    French entities observed targeted and compromised with Turla

    Members of France's Cyber Crisis Coordination Centre (C4) observed French entities being targeted and compromised using the Turla intrusion set, affecting ministries and organizations in the diplomatic, defence, justice, and technology sectors.

    Rapport menaces et incidents - CERT-FR
  10. Jul 13, 20264mo ago

    UK and EU attribute failed January Poland grid attack to FSB Center 16

    UK and EU officials said a failed January attack on Poland’s energy grid was carried out by actors linked to FSB Center 16. Officials warned the operation could have disrupted electricity service for 500,000 Polish citizens.

    Weak Security Continues to Fuel Russian Cyberattacks
  11. Jul 13, 20264mo ago

    December 2025 attack hits Poland's energy grid

    The NCSC notice states that an attack on Poland's energy grid occurred in December 2025 and was later formally attributed to FSB Centre 16 by the UK and EU member states.

    UK and Allies urge critical sectors to improve defences against Russian intelligence targeting | National Cyber Security Centre
  12. Jul 13, 20264mo ago

    Turla intrusion set has been used for espionage since at least 2004

    CERT-FR reported that the Turla intrusion set, attributed to the 16th Centre of Russia's FSB, has been used since at least 2004 for intelligence-gathering against strategic entities and individuals worldwide, including in France.

    Rapport menaces et incidents - CERT-FR
  13. Oct 30, 20251y ago

    FSB Center 16 router campaign has affected sectors since 2015

    The reference says the Russia-affiliated group identified as FSB Center 16 has targeted vulnerable routers and network infrastructure affecting telecommunications, higher education, and manufacturing since 2015, with activity especially impacting Ukraine and allied countries. The campaign used SNMP scanning and exploitation of older Cisco flaws, including CVE-2018-0171 and CVE-2008-4128.

    Nations warn of Russian router threat as DDoS forces get sanctioned - SDxCentral
  14. Aug 1, 20251y ago

    FBI IC3 warns FSB Center 16 compromised thousands of network devices

    In August 2025, an FBI IC3 warning said operators linked to Russia's FSB Center 16 had compromised thousands of network devices in critical infrastructure sectors. The warning described two main access vectors: exposed SNMP v1/v2 with weak or default community strings and exploitation of Cisco Smart Install flaw CVE-2018-0171.

    Атаки APT на сетевое оборудование: TTP FSB Center 16
  15. Feb 24, 20225y ago

    Russia launches full-scale war against Ukraine

    CERT-FR anchored ongoing Turla espionage campaigns against Ukraine, NATO countries, and EU member states to the context of Russia's war of aggression launched on 24 February 2022.

    Rapport menaces et incidents - CERT-FR
  16. Nov 1, 20215y ago

    Authorities link FSB Center 16 to CVE-2018-0171 exploitation

    The joint advisory said the Russian group tied to FSB Center 16 has exploited Cisco Smart Install vulnerability CVE-2018-0171 since November 2021. The activity was linked to the group's broader targeting of routers and network devices used to access critical infrastructure networks.

    US and allies warn of Russian critical infrastructure attacks
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.

Open in app →
Do you run this?See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
Get the Full Actor Profile
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.