Mallory
← Back to News
vendor-distribution-compromiseransomware-group-operationendpoint-security-bypassdetection-content-update

Kaseya VSA Supply-Chain Attack Disabled Defender and Deployed REvil Ransomware

Supply Chain Risk · 2 sources · Updated 4mo ago · First seen Jul 4, 2016
Kaseya VSA Supply-Chain Attack Disabled Defender and Deployed REvil Ransomware

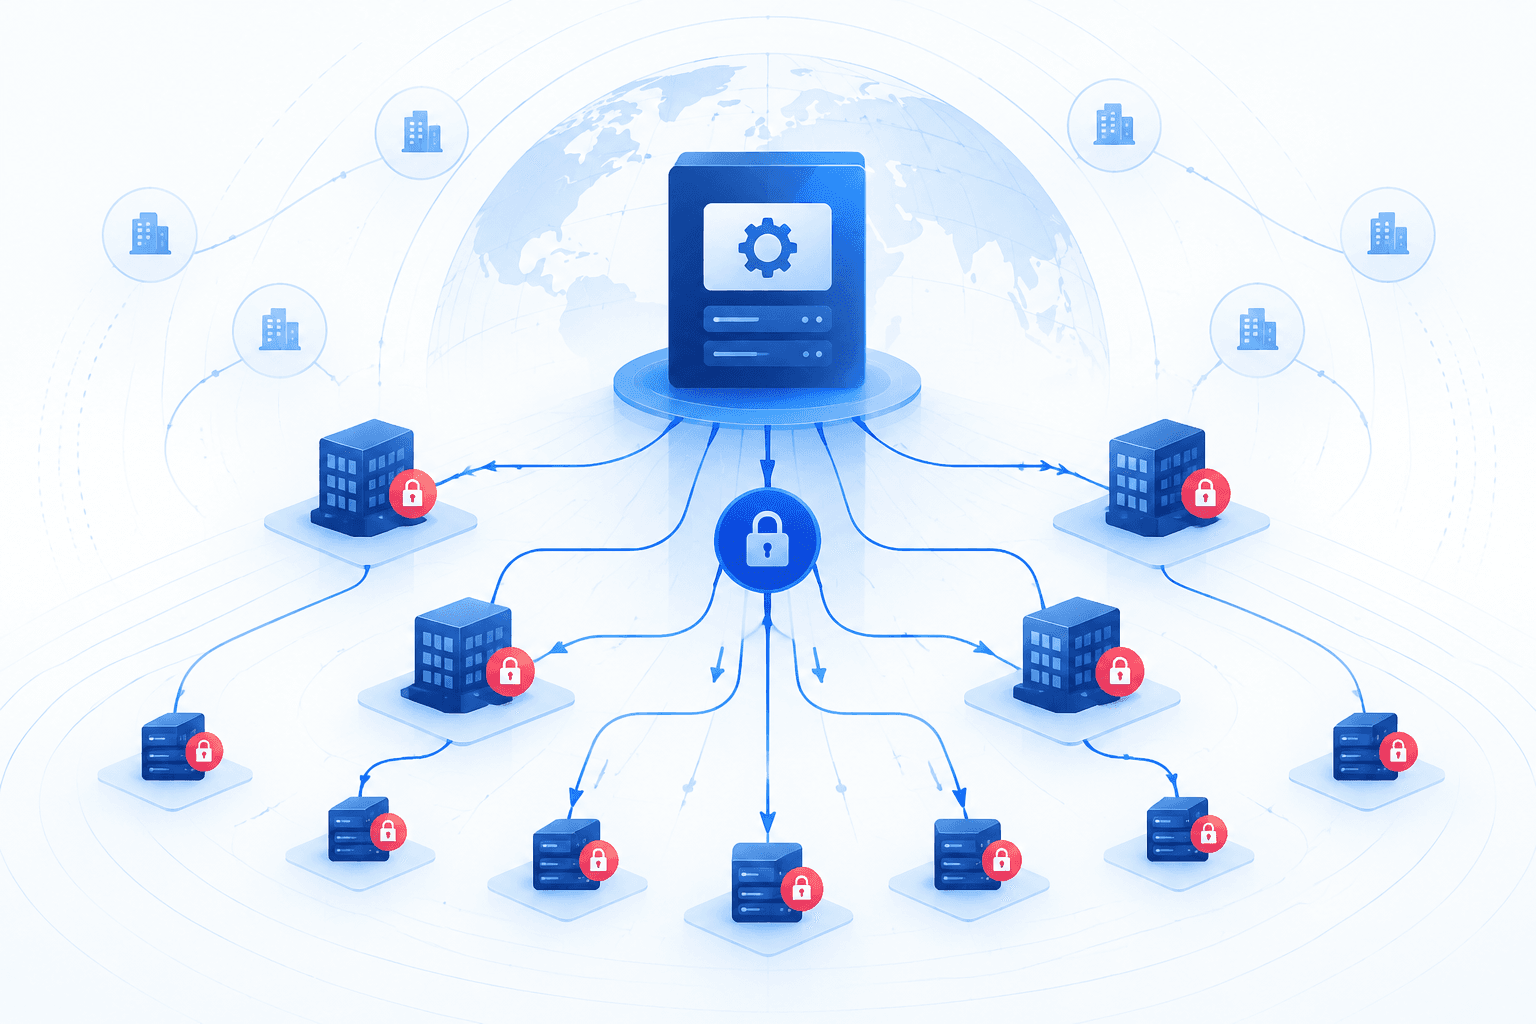
Attackers exploited a code injection flaw in on-premises Kaseya VSA servers to distribute a malicious update through managed service providers, turning the remote management platform into a supply-chain delivery mechanism for REvil/Sodinokibi ransomware. Kaseya said victims numbered in the low thousands, while tens of thousands of customers reportedly shut down VSA servers as a precaution; reporting cited especially heavy impact in the UK, South Africa, and Canada. The intrusion chain used an encrypted file named agent.crt, pushed as a "Kaseya VSA Agent Hot-fix", then decoded it to agent.exe and launched the ransomware payload mpsvc.dll via DLL sideloading.

The malware sequence also attempted to disable Microsoft Defender protections before encryption, underscoring the importance of controls such as Defender tamper protection to prevent unauthorized security-setting changes. Response guidance included shutting down on-premises VSA servers, disabling VSA agents, backing up sensitive data, rotating credentials including krbtgt, and investigating for persistence, data theft, and lateral movement. Published indicators included file hashes, registry artifacts, log locations, and source IP addresses associated with curl/7.69.1 activity to help defenders scope exposure and hunt for compromise.
Does this reach your builds?Trace attribution and downstream blast radius.
Trace the chain
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

3 events · Jul 4, 2016
  1. Jul 4, 201610y ago

    Customers take Kaseya VSA servers offline after the incident

    At least 36,000 customers reportedly took their servers offline in response to the ransomware incident. This reflected a broad defensive shutdown affecting organizations using Kaseya VSA.

    Customer Advisory Kaseya VSA Ransomware Incident
  2. Jul 4, 201610y ago

    Kaseya says victim count is in the low thousands

    Following the attack, Kaseya said the number of victims was in the low thousands. The incident was described as having especially significant impact in the UK, South Africa, and Canada.

    Customer Advisory Kaseya VSA Ransomware Incident
  3. Jul 4, 201610y ago

    REvil exploits Kaseya VSA in a supply-chain ransomware attack

    In July 2021, attackers exploited a code injection vulnerability in on-premises Kaseya VSA servers to push malicious updates through managed service providers to downstream customer endpoints. The attack chain included delivery of an encrypted file named agent.crt, decoding it to agent.exe, disabling Microsoft Defender protections, and executing the REvil/Sodinokibi payload via DLL sideloading.

    Customer Advisory Kaseya VSA Ransomware Incident
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

1 linked

Malware

1 linked

Affected products

1 linked
Virtual System Administrator

Organizations

1 linked
Kaseya

Breaches

1 linked
KASEYA-2021-07

Observables

7 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See attribution and downstream blast radius, and whether this package or vendor reaches your builds.
Trace the Supply Chain
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.