Critical RCE in sentence-transformers Bypasses `trust_remote_code=False`
Emerging Technology Risk · 2 sources · Updated 4mo ago · First seen Jul 31, 2026
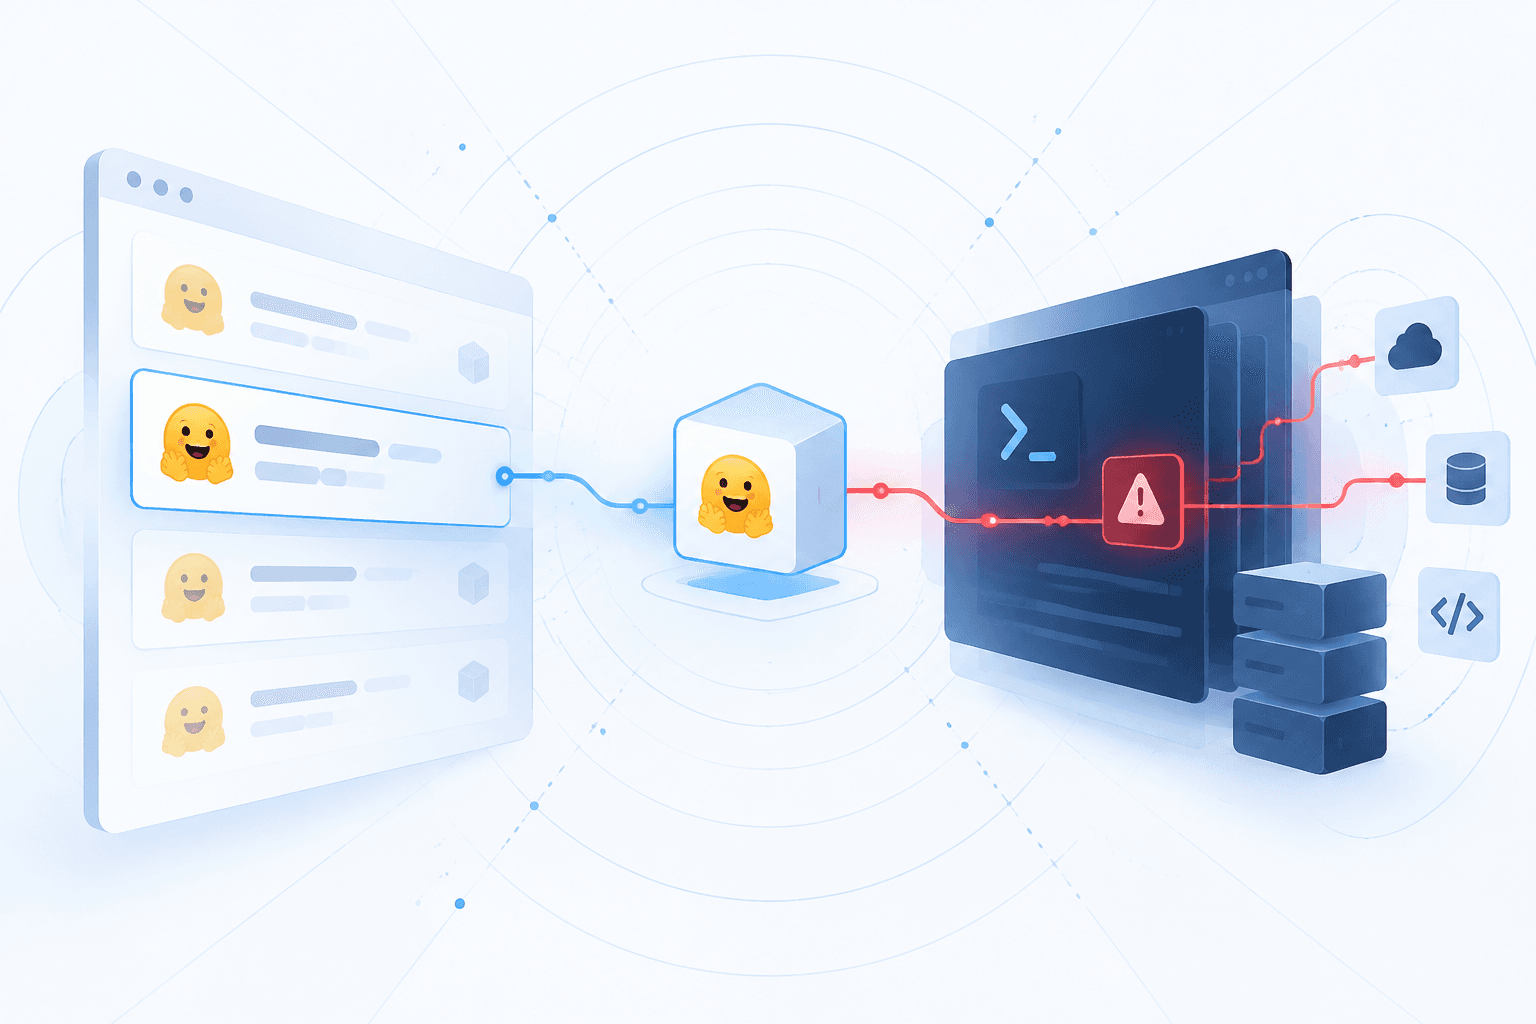
A critical vulnerability tracked as CVE-2026-68770 affects Hugging Face's sentence-transformers package and allows arbitrary code execution when a model is loaded from a local path, even if applications explicitly set trust_remote_code=False. The flaw stems from a logic error in the import_module_class helper in sentence_transformers/util/misc.py, where an or os.path.exists(model_name_or_path) condition accepts existing local filesystem paths and can cause malicious Python code referenced through modules.json to run during import. The issue is classified as CWE-94 and carries a CVSS 3.1 score of 9.8, with high impact to confidentiality, integrity, and availability.
The bug affects sentence-transformers through version 5.5.1 and creates a significant AI/ML supply-chain risk for organizations that load models from disk or from directories an attacker can influence. Reporting indicates no active exploitation had been confirmed at publication, but maintainers have released a fix, with coverage pointing to version 5.6.1 as the remediated release. Organizations using local model-loading workflows are being urged to upgrade immediately and tighten controls around model directories, stored artifacts, and any process that imports untrusted model content.