Hugging Face Transformers Flaw Let Malicious Models Bypass `trust_remote_code`
Emerging Technology Risk · 4 sources · Updated 5mo ago · First seen Jun 3, 2026
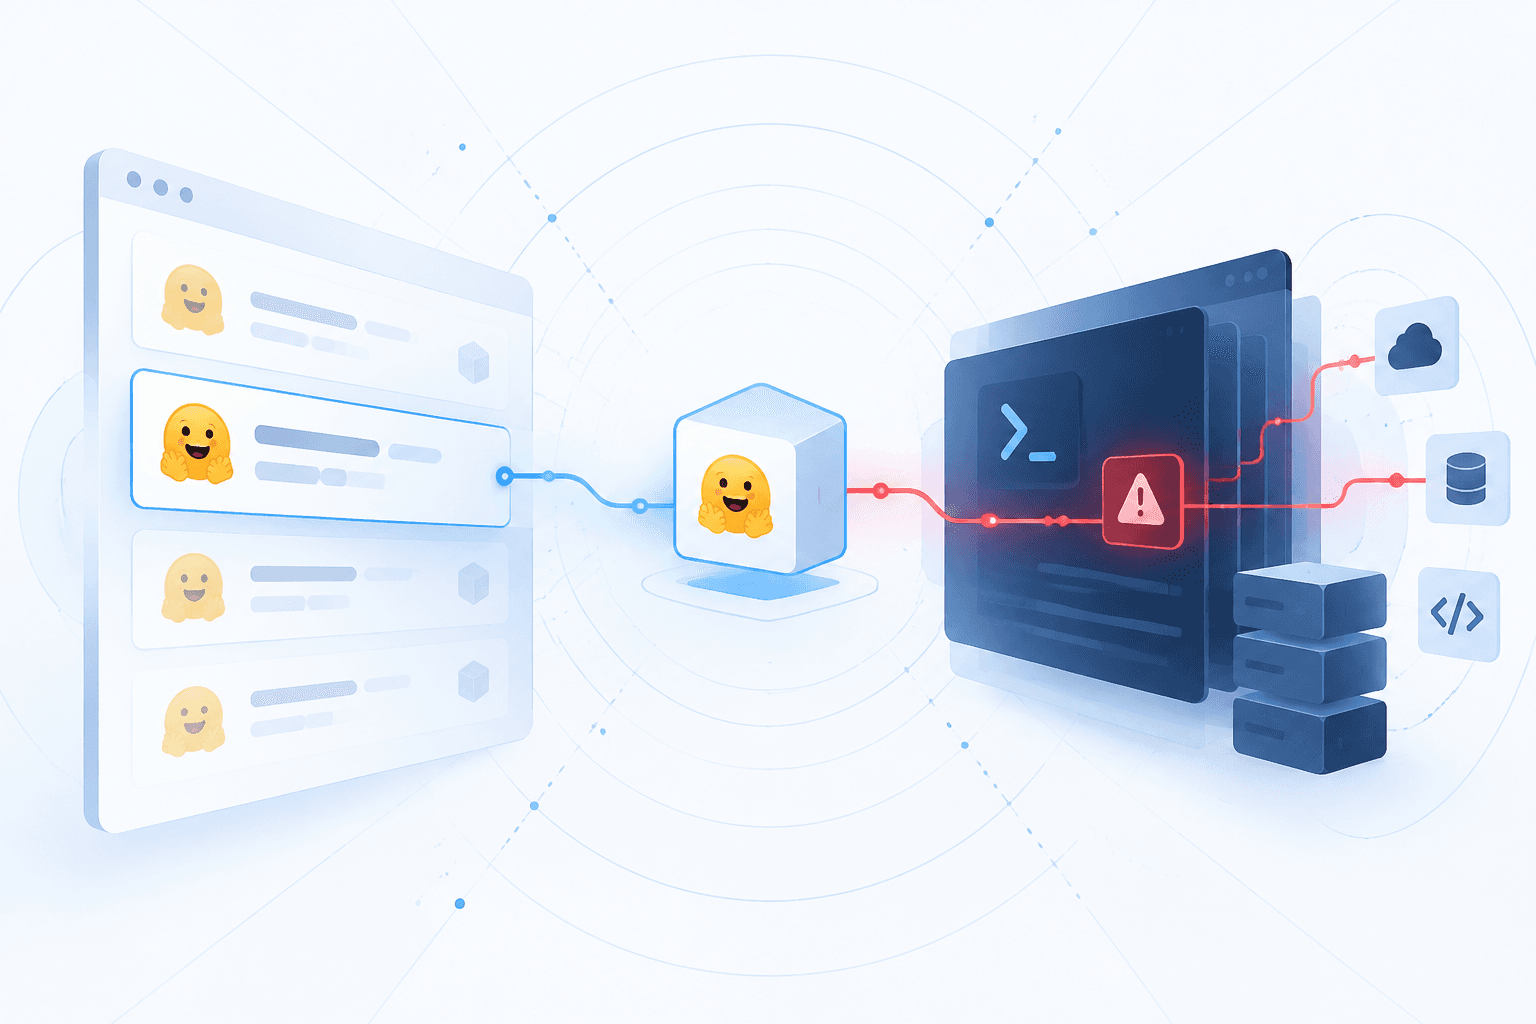
A critical remote code execution flaw in Hugging Face's transformers library allowed attacker-controlled model repositories to run arbitrary code during the standard from_pretrained() loading process, even when trust_remote_code=False was set. The issue was tied to unsafe handling of untrusted model configuration data, including nested configuration resolution in the LightGlue loading path, where values from config.json could override the intended safety setting and trigger execution of attacker-supplied Python modules during model initialization.
Reports said the vulnerability affected transformers versions 4.56.0 through 5.2.x in environments where the kernels package was installed, with version 5.2.0 specifically cited in LightGlue-related exploitation scenarios. Exposed targets included inference servers, research notebooks, CI/CD pipelines, and automated model evaluation systems, where successful compromise could enable theft of cloud credentials, API keys, SSH keys, proprietary datasets, lateral movement, persistence, and backdoor deployment. Hugging Face released a fix in transformers 5.3.0 and urged organizations to upgrade and treat model loading as a code execution surface.