CopyEscape Flaw in `docker cp` Enables Container-to-Host File Overwrite
Patch & Detection Intelligence · 4 sources · Updated 3mo ago · First seen Aug 11, 2026

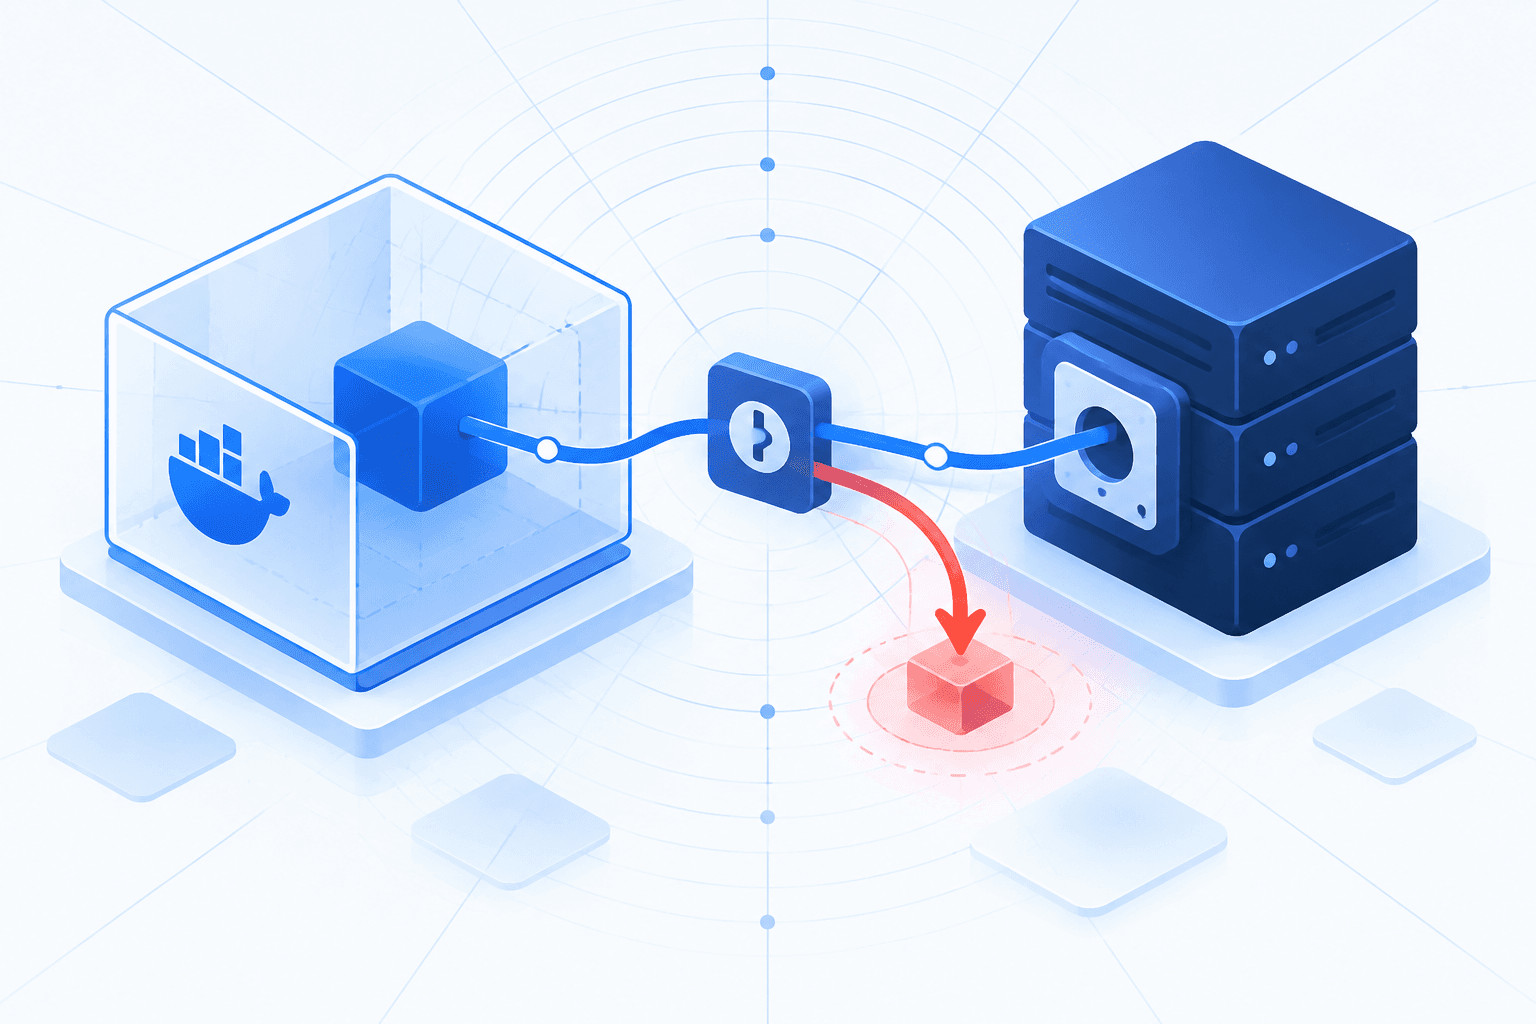
Imperva disclosed CopyEscape, tracked as CVE-2026-17106, a container-to-host arbitrary file-write vulnerability in Docker’s docker cp functionality that allows a malicious container to create or overwrite files outside the destination chosen by the user on the machine running the Docker CLI. The issue stems from a filesystem race in Docker’s archive creation path combined with unsafe symlink handling during extraction, turning a routine file copy from a container into a host write primitive.
Docker confirmed the same CVE also affects sbx cp in Docker Sandboxes when copying files out of sandboxes. Imperva said exploitation was validated against Docker Engine 29.6.1 on Linux and Docker Desktop 4.81.0 on macOS, with impact ranging from compromise of the developer account using the CLI to root code execution when docker cp is run with elevated privileges. Fixes are available in Docker Engine and CLI 29.7.2 or later, Docker Desktop 4.86.0 or later, and Docker Sandboxes 0.38.0 or later.