Docker Sandboxes TOCTOU Flaw Lets Guests Redirect Host Unix-Socket Connections
Patch & Detection Intelligence · 12 sources · Updated 2mo ago · First seen Sep 17, 2026
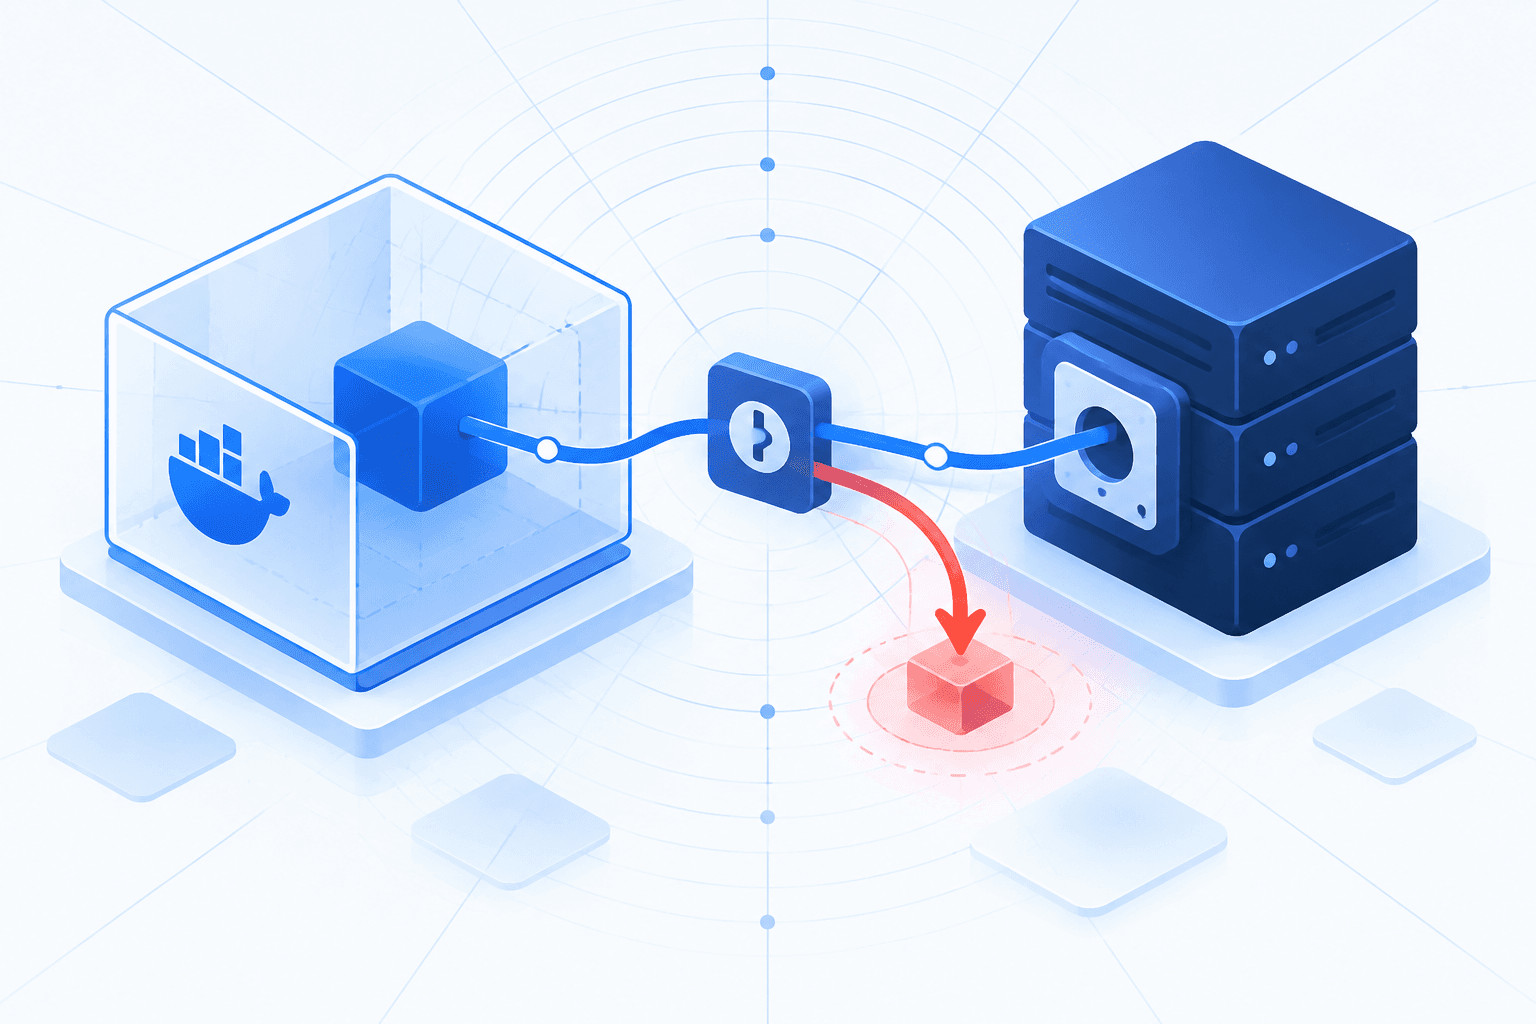
Docker disclosed and fixed CVE-2026-79994, a high-severity time-of-check to time-of-use (TOCTOU) vulnerability in the host-side relay used by Docker Sandboxes. A malicious sandbox guest could alter an intermediate workspace directory after validation of a Unix-socket path, replacing it with a symbolic link and causing the trusted relay to connect to an AF_UNIX socket outside the approved workspace.
The flaw affects Docker Sandboxes versions 0.37.0 through versions before 0.41.0; version 0.41.0 includes the specific fix. Docker's broader security advisory recommends upgrading deployments to 0.43.0 or later. Although the issue does not directly grant unrestricted host filesystem access, it can enable a guest to influence connections to reachable host socket services, potentially affecting confidentiality and integrity; no active exploitation has been confirmed.