
Loading story…
Attackers compromised a prominent Georgian news website and used its Georgian-language pages as a watering hole to selectively infect macOS visitors. Malicious JavaScript profiled users by operating system, browser, and prior visits, then redirected qualifying Safari users to an attacker-controlled fake Adobe Flash update that delivered a signed macOS application, GetFlashPlayer.app. The malware established persistence with a LaunchAgent, opened the legitimate Adobe Flash website as a decoy, and communicated with command-and-control infrastructure over TCP port 7777.
Volexity identified the payload as a newer variant of OSX/Leverage.A, a macOS backdoor that expanded beyond earlier versions by providing unrestricted shell access. Reporting on the malware family and related analysis highlighted code-signing details, file hashes, network indicators, and host- and network-based detection opportunities, giving defenders concrete artifacts to hunt for on potentially exposed Apple systems.

Pull IOCs and campaign context straight into your stack.
3 events from the most recent confirmed update back to the earliest known activity.
Volexity reported that attackers had breached a respected Georgian media outlet and used the Georgian-language section to selectively target Safari users on Mac OS X with a fake Adobe Flash update flow. The report detailed the infection chain, persistence via a LaunchAgent, command-and-control traffic to downloadarchives.servehttp[.]com on TCP port 7777, and assessed the payload as a newer OSX/Leverage.A variant with unrestricted shell access.
ESET published reporting on the Stantinko adware campaign, describing it as operating covertly since 2012. Volexity later noted one IP overlap with an ESET Stantinko report but said it was unaware of any tie between the macOS activity and Stantinko.
The macOS malware sample used in the campaign was digitally signed with an Apple Developer certificate for "aleks papandopulo." The code-signing metadata carried a timestamp of February 5, 2016, 06:25:25.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 14 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
3 references tracked. Mallory keeps watching after this page renders.
volexity.com
Open sourcewelivesecurity.com
Open sourcealienvault.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.

The **Flashback** malware infected more than 500,000 Mac systems—and by some estimates more than 600,000—after evolving from fake Adobe Flash Player installers to **drive-by compromise via malicious Java applets**. Researchers tied the largest wave to exploitation of Java flaws including `CVE-2012-0507` and `CVE-2011-3544`, which allowed compromised websites to silently drop malware on vulnerable OS X hosts. Doctor Web said its telemetry showed about **817,879** bots had connected at some point, with roughly **550,000** systems still checking in during a 24-hour period and around **650,000** remaining infected overall, disputing lower public estimates. Technical analysis showed Flashback used a hidden Mach-O installer, persistence via a plist, and a second-stage library that intercepted **HTTP and HTTPS** traffic by abusing `DYLD_INSERT_LIBRARIES` and CoreFoundation stream interposition. The malware encrypted components with **RC4** keys derived from each victim Mac’s Platform or Hardware UUID, generated large numbers of domains for command-and-control, validated updates with hard-coded **RSA** signatures, and even used a **Twitter hashtag** fallback for C2 discovery. Its operators appeared focused on **ad fraud and traffic manipulation**, including harvesting Google search-related data and altering responses to simulate ad clicks, while Apple later issued Java patches and a dedicated removal tool to contain the outbreak.
Aug 15, 2026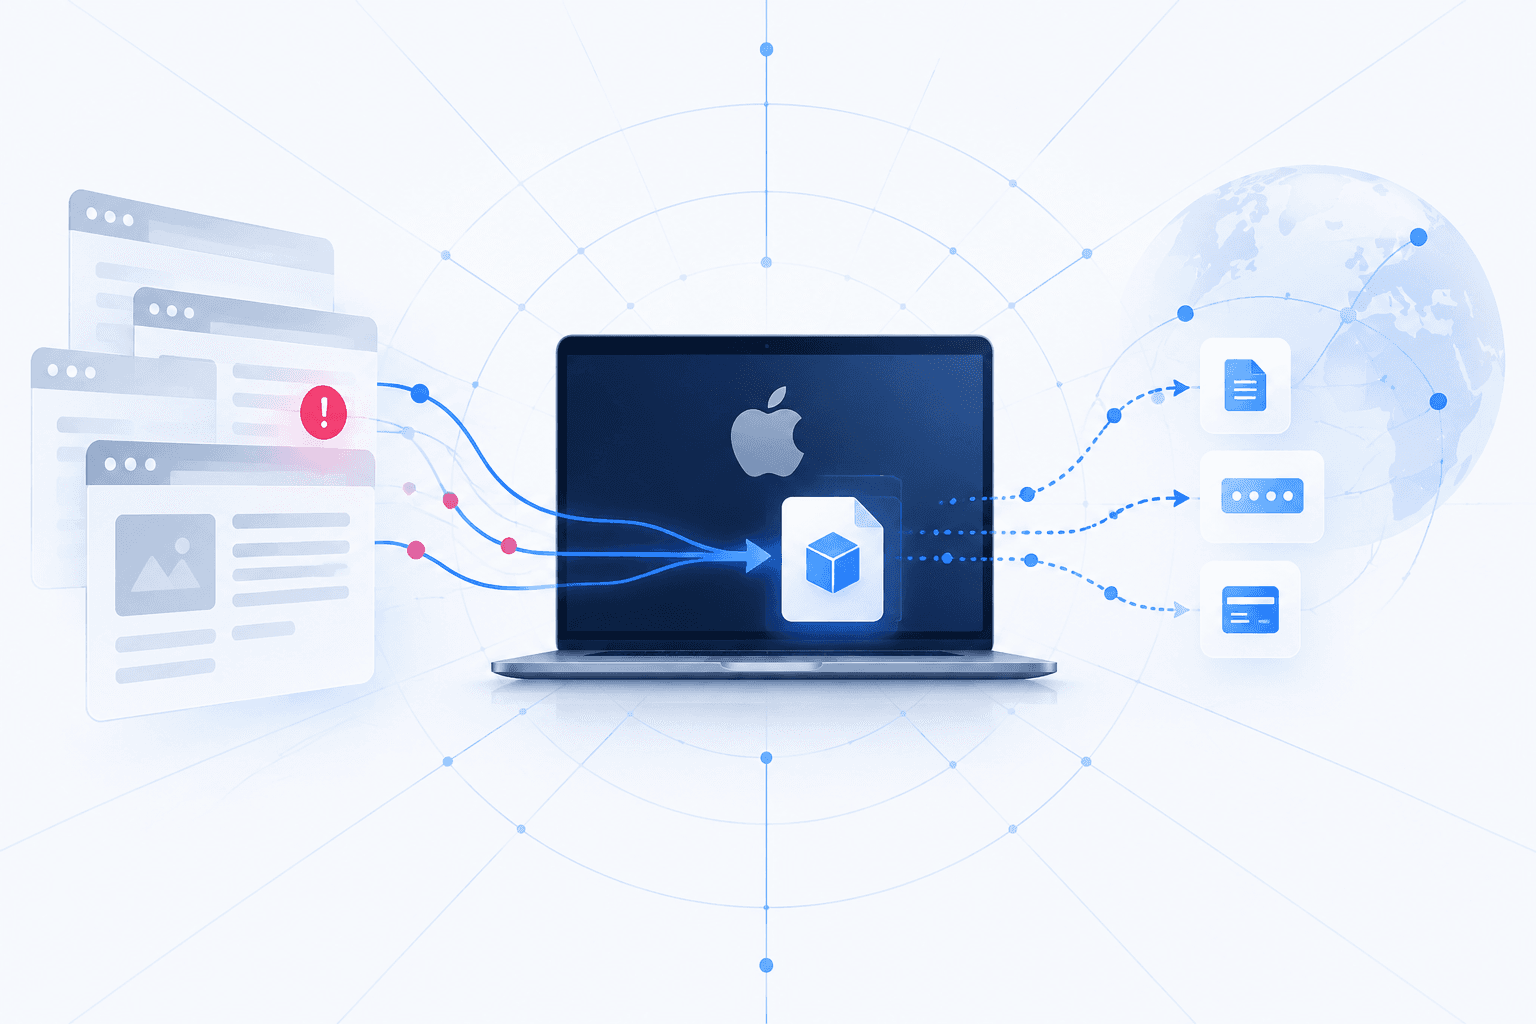
The **Macfinger ClickFix** campaign compromises legitimate websites by injecting JavaScript that fingerprints visitors and selectively presents macOS users with a fake bot-protection page. The page uses ClickFix-style instructions to trick victims into executing a malicious shell script, which retrieves architecture-specific Mach-O payloads for Apple Silicon or Intel-based Macs. Post-compromise activity includes repeated telemetry and credential-submission requests to command-and-control infrastructure. Ransom-ISAC assessed the final payload as a variant of **Atomic macOS Stealer (AMOS)**, though observed indicators differ from previously tracked AMOS activity; investigators have released IOC, packet-capture, and collected-file archives to support detection and analysis.
Sep 28, 2026
A sophisticated cybercriminal campaign has been identified targeting macOS users, particularly developers, by leveraging fake download portals that impersonate trusted platforms such as Homebrew, LogMeIn, and TradingView. The attackers have registered over 85 domains that closely mimic the legitimate sites of these popular tools, using convincing branding and user interfaces to deceive visitors. These malicious domains are promoted through Google Ads, ensuring that they appear prominently in search results and increasing the likelihood that unsuspecting users will visit them. Once on the fake sites, users are instructed to copy and execute a curl command in their Terminal, which initiates the download and installation of infostealing malware. The primary payloads delivered in this campaign are AMOS (Atomic macOS Stealer) and Odyssey Stealer, both of which are capable of harvesting sensitive information such as system details, browser data, and cryptocurrency credentials from infected machines. The campaign employs advanced social engineering tactics, including clipboard manipulation and command obfuscation, to increase the success rate of infections. Researchers from Hunt.io have mapped the infrastructure supporting this operation, noting that the attackers reuse IP addresses and SSL certificates across multiple domains, indicating a persistent and well-organized effort. The infrastructure has been active for several years, with some IP addresses registered under personal names, suggesting a degree of operational continuity and experience. The campaign does not rely on exploiting software vulnerabilities but instead exploits user trust in widely used open-source and financial tools. The use of Google Ads as a distribution vector highlights the attackers' willingness to invest in paid advertising to reach their targets. The campaign's focus on the developer community is particularly concerning, as compromised developer systems could lead to broader supply chain risks. Security researchers have emphasized the importance of verifying download sources and being wary of unsolicited installation instructions, especially those involving Terminal commands. The ongoing nature of the campaign, with continuous adaptation of infrastructure and tactics, underscores the need for vigilance among macOS users. The discovery of this campaign began with public reports from independent researchers, which were then corroborated and expanded upon by threat intelligence teams. The scale and persistence of the operation suggest that it is likely to continue evolving, posing a significant threat to the macOS ecosystem. Organizations are advised to educate users about the risks of malvertising and to implement technical controls to block access to known malicious domains. The campaign demonstrates the increasing sophistication of social engineering attacks targeting macOS, a platform often perceived as less vulnerable than Windows.
Jun 29, 2026