Lazarus Spearphishing Campaign Used Word Templates, Rundll32, and Startup Persistence
Threat Actor Intelligence · 6 sources · Updated 3mo ago · First seen Jan 27, 2020
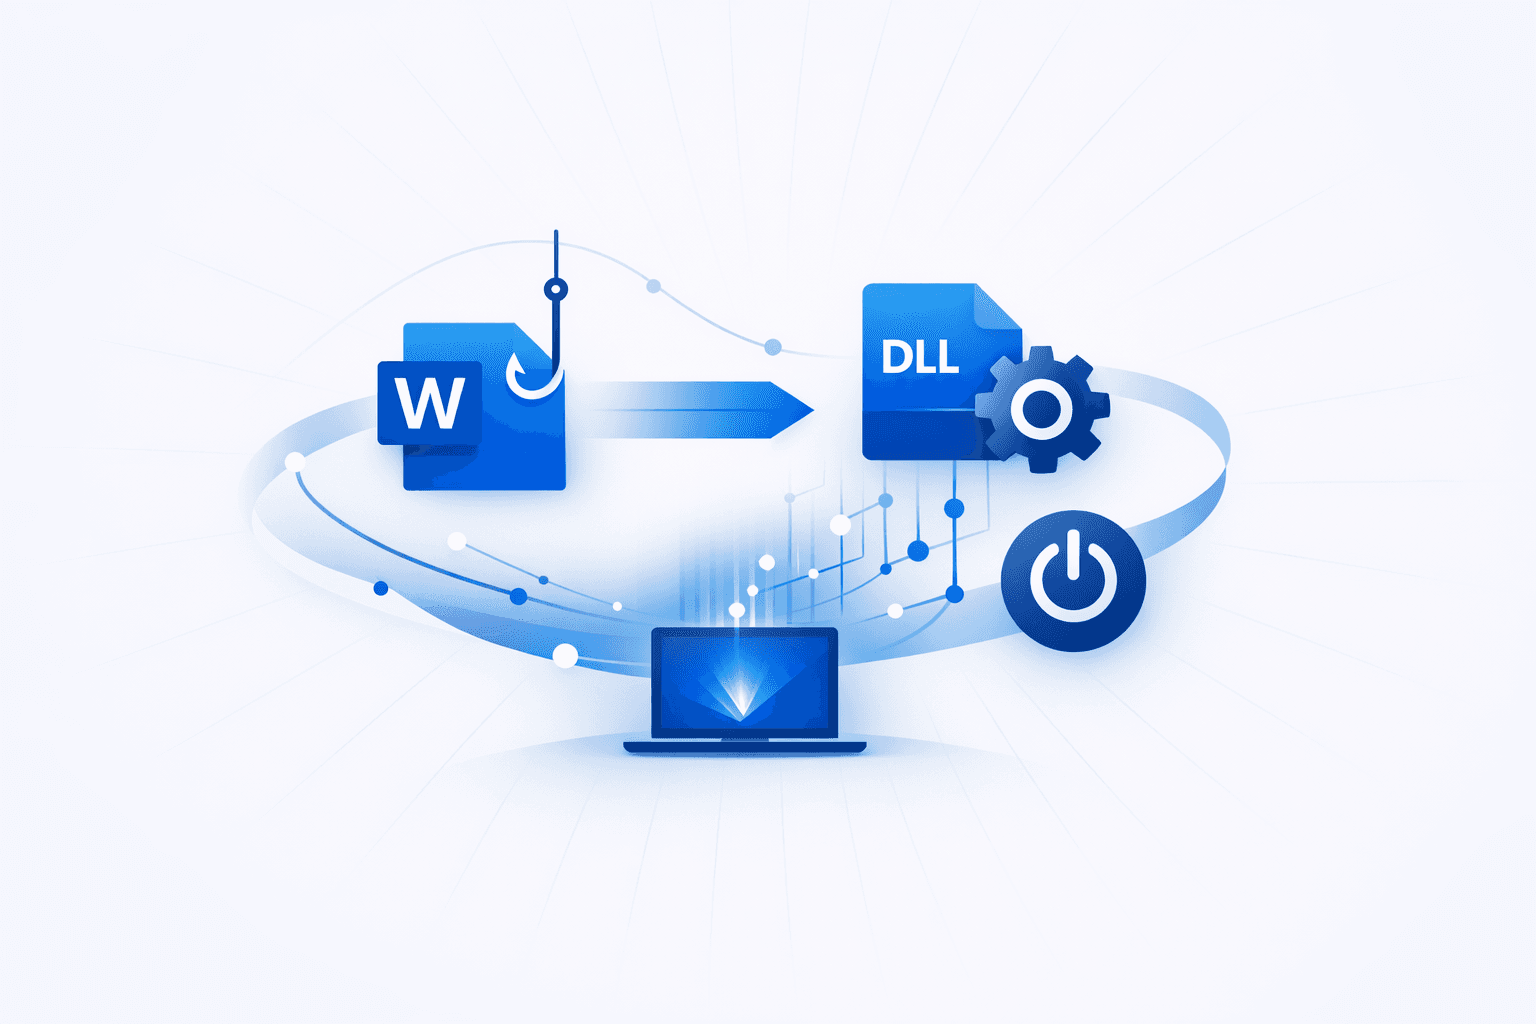
The Lazarus Group ran a spearphishing campaign that delivered malicious Microsoft Word documents to targets in aerospace, defense, research, and financial sectors, including organizations linked to Boeing, BAE Systems, Lockheed Martin, and the Republic of Korea Army. The infection chain used remote template injection to fetch an external DOTM file, whose macro dropped a lure document and a malicious DLL such as onenote.db into the victim’s AppData path, then executed the implant while showing a decoy file to reduce suspicion. Related reporting describes similar Lazarus lures sent in spoofed emails, with separate payloads for 32-bit and 64-bit systems and reconnaissance-focused first-stage malware.
The implant executed through rundll32.exe and established persistence via the Windows Startup folder, techniques widely tracked in MITRE ATT&CK as T1218.011 and T1547.001. Once active, it collected host, process, and disk information, compressed or encrypted the data, and exfiltrated it over HTTP POST using compromised or attacker-controlled infrastructure, including IIS/Plesk-hosted domains such as elite4print.com and astedams.it. Analysts linked the activity to Lazarus based on recurring tradecraft, lure themes, victim profiling, and overlap with operations such as Operation Dream Job, where the group similarly abused rundll32.exe and autostart mechanisms for stealthy execution and persistence.