PikaBot Malvertising Campaign Uses Fake AnyDesk Ads to Deliver Loader Malware
Malware Intelligence · 16 sources · Updated 3mo ago · First seen Dec 14, 2022
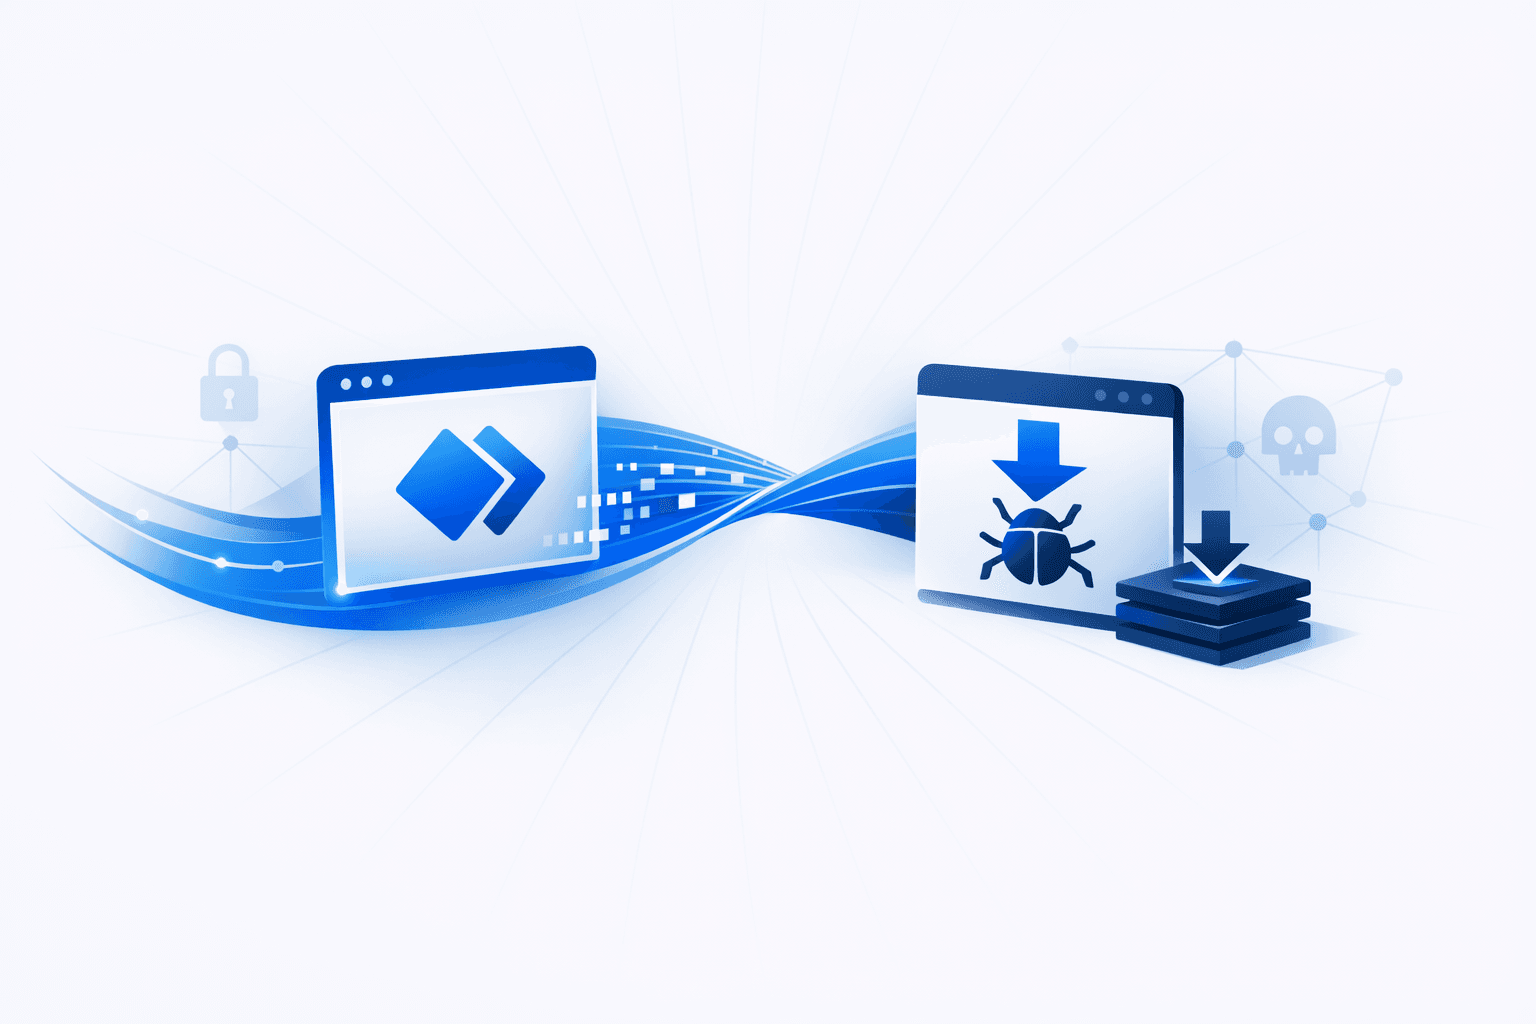
Attackers used malicious Google search ads impersonating AnyDesk to deliver PikaBot, redirecting victims through traffic-filtering and fingerprinting infrastructure before serving a digitally signed MSI installer from Dropbox. Researchers said the chain included JavaScript-based anti-analysis checks and likely virtualization detection, echoing earlier fake software ad campaigns that used spoofed AnyDesk pages, MSI installers, and staged payload delivery to infect Windows systems.
PikaBot is a loader designed to fetch and execute additional malware, with commands for shell execution, payload retrieval, shellcode launch, and system profiling over encrypted HTTPS communications. Its emergence in malvertising expands a malware family already linked to initial-access activity and ransomware delivery ecosystems, reinforcing a broader criminal model in which loaders such as PikaBot, IcedID, and TrickBot establish footholds that are later used for tools like Cobalt Strike and, in some cases, hands-on ransomware deployment.