
Loading story…
Researchers reported that GhostSocks, a Golang-based SOCKS5 backconnect proxy sold as a malware-as-a-service, is tightly integrated with the LummaC2 infostealer ecosystem and can be automatically deployed on Lumma-infected hosts through a partnership promoted on Telegram. GhostSocks supports both Windows and Linux, stores an obfuscated JSON configuration in %APPDATA%\config, communicates with relay-based C2 infrastructure over HTTP, and assigns infected systems as Tier 1 backconnect nodes to create SOCKS5 tunnels for criminal customers. Analysts said the malware also enables arbitrary command execution, SOCKS5 credential changes, and download-and-execute activity, extending Lumma-compromised machines beyond credential theft into proxy infrastructure for follow-on abuse.
Separate analysis of LummaC2 v4.0 showed the stealer continuing to evolve with stronger evasion and anti-analysis features, including control-flow-flattening obfuscation, XOR-encrypted strings, dynamic C2-delivered configuration, and a two-layer packer designed to frustrate reverse engineering. KrakenLabs found Lumma delays execution until it detects human-like mouse movement, calculating cursor angles and restarting its checks if movement appears unnatural, a technique that can block detonation in sandboxes. The combined findings indicate that Lumma operators and affiliates are pairing a mature infostealer with a dedicated proxy service, while using anti-sandbox protections and hardened packing to reduce detection and sustain access.
Pull IOCs and campaign context straight into your stack.
5 events from the most recent confirmed update back to the earliest known activity.
Infrawatch says the GhostSocks sample they analyzed was observed on this date; the sample was heavily obfuscated and linked to relay-based C2 infrastructure.
GhostSocks expanded promotion to an English-speaking criminal forum under the moniker "GhostSocks," broadening its visibility beyond Russian-language venues.
A Telegram announcement introduced automatic provisioning of GhostSocks within the Lumma administration panel and discounted pricing for existing Lumma customers, indicating close integration between the two services.
Infrawatch reports GhostSocks was first identified in October 2023 when it was advertised on a Russian-language criminal forum as a SOCKS5 backconnect proxy malware service.
Outpost24 states that LummaC2, an information-stealing malware sold as a MaaS offering, has been sold in underground forums since December 2022.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Pull the IOCs, campaigns, and victimology behind this family, ready to push into your SIEM and EDR.
2 references tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Darktrace reported rising activity tied to **GhostSocks**, a Go-based malware-as-a-service offering advertised on the Russian-language forum `xss[.]is`, which turns infected systems into residential **SOCKS5** proxy nodes. The malware is designed to help threat actors evade IP-based detection and geographic restrictions by routing traffic through victim devices, using a relay-based command-and-control architecture and **TLS**-wrapped proxy traffic for stealth. Later variants added persistence through Windows registry run keys and expanded functionality beyond proxying to include backdoor features for arbitrary command execution and payload delivery. The company said GhostSocks saw broader adoption after a 2024 partnership with **Lumma Stealer** and has also been linked to use by the **Black Basta** ransomware group for maintaining long-term access. In a December 2025 incident at an education-sector organization, a device contacted Lumma-linked infrastructure, downloaded a GhostSocks-associated executable called `Renewable.exe`, retrieved additional payloads from suspicious endpoints, and began likely early-stage beaconing to rare external destinations. Darktrace said blocking actions were recommended multiple times, but because the customer was operating in Human Confirmation Mode, mitigations were not automatically enforced, allowing the activity to continue.
Jun 29, 2026
**Lumma Stealer** continued to expand as a prolific malware-as-a-service infostealer, with researchers reporting sharp growth in detections and increasingly diverse delivery chains. Microsoft attributed the malware and its command-and-control ecosystem to **Storm-2477**, which operates Lumma for affiliates that build payloads and run campaigns through a management panel. ESET reported Lumma detections surged **369%** in late 2024, while additional reporting from Netskope and other researchers highlighted ongoing **fake CAPTCHA/ClickFix** lures and fresh payload variants designed to evade detection. Observed campaigns used multiple infection paths, including phishing, malvertising, compromised websites, trojanized software, abuse of trusted platforms such as GitHub, and delivery by other malware including **DanaBot**. Microsoft described an early-April campaign that combined **EtherHiding** hosted through Binance Smart Chain smart contracts with ClickFix social engineering, and an April 7 campaign targeting Canadian organizations that used **Prometheus TDS** redirection plus `mshta` and PowerShell stages to deploy Lumma alongside **Xworm**. The malware was reported stealing credentials and cryptocurrency wallets, using process injection and hollowing, and relying on layered infrastructure with hardcoded domains and fallback channels through **Steam** and **Telegram** behind Cloudflare; Microsoft said its disruption effort led to the takedown, suspension, or blocking of about **2,300 malicious domains** tied to Lumma operations.
Aug 15, 2026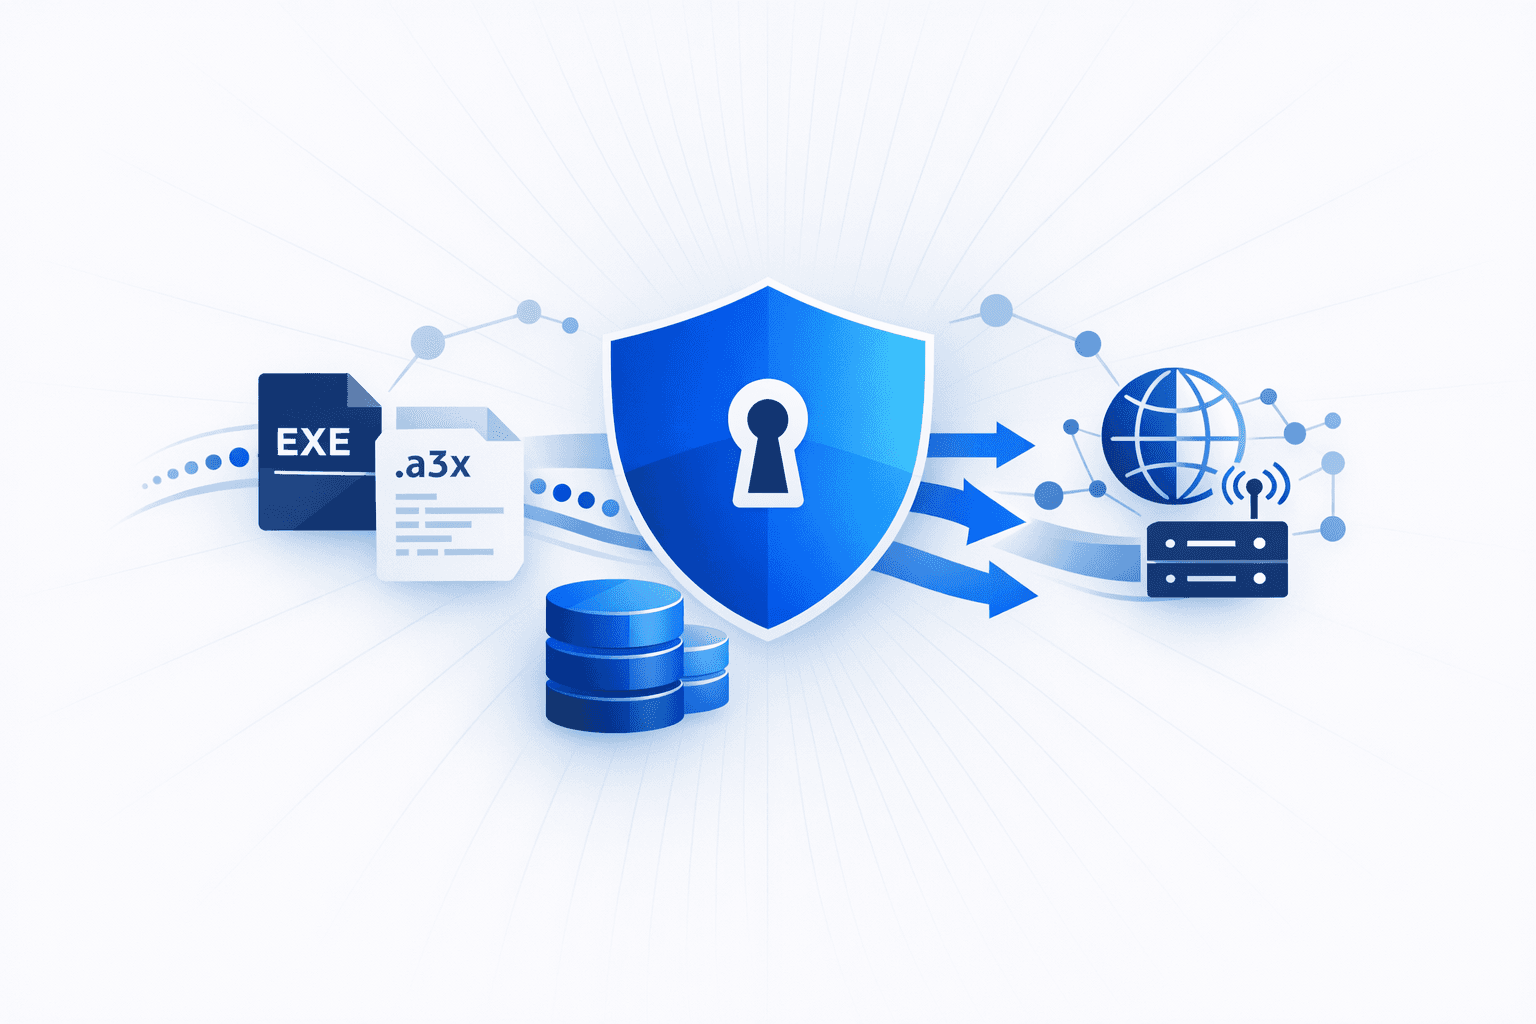
Multiple incidents have been documented involving the deployment of the Lumma Stealer malware on Windows systems, followed by the installation of additional malicious payloads. Technical analysis reveals that the Lumma Stealer installer, a large PE32 executable, temporarily saves several files to the infected host, including AutoIt3 scripts and various data files. The infection process also generates a custom `.a3x` AutoIt3 script and establishes command-and-control (C2) communications with domains such as `offenms[.]cyou`. Network traffic captures and file samples from these incidents have been made available for further analysis, providing insight into the infection chain and the nature of the follow-up malware. Indicators of compromise (IOCs), packet capture files, and extracted malware samples have been published to assist defenders in identifying and mitigating these threats. The technical details include SHA256 hashes of the malware, file paths used during infection, and specifics about the C2 infrastructure. These resources enable security teams to detect similar infections and understand the tactics used by threat actors leveraging Lumma Stealer in multi-stage attacks.
Jun 29, 2026