
Loading story…
Palo Alto Networks Unit 42 detailed two advanced Kerberos forged-ticket techniques—Diamond Ticket and Sapphire Ticket—that build on the classic Golden Ticket attack to compromise Active Directory domains. Instead of creating a fake ticket from scratch, both methods alter a legitimately issued ticket-granting ticket (TGT), making them harder to detect because the ticket originates from a domain controller. The attacks require theft of the KRBTGT account password hash and can give an intruder broad or effectively unconstrained access by modifying the Privileged Attribute Certificate (PAC) or changing identity data inside the TGT.
The report said Sapphire Ticket abuses U2U and S4U2Self to obtain a legitimate high-privilege PAC and transplant it into another user’s TGT, while Diamond Ticket directly edits a valid TGT’s PAC to add privileges or impersonate another user. Unit 42 linked forged-ticket tradecraft to activity associated with Playful Taurus / APT15 / NICKEL, which has previously used Mimikatz and credential-dumping techniques for Golden Ticket persistence. Recommended detection opportunities include monitoring for KRBTGT hash theft and DCSync behavior, suspicious combined use of U2U and S4U2Self, mismatches between TGT and TGS activity, and Windows events such as 4627, 4728, and 4732.
Get the actors, campaigns, and ATT&CK mapping behind it.
4 events from the most recent confirmed update back to the earliest known activity.
On its December 2022 publication, Unit 42 described Diamond Ticket and Sapphire Ticket as newer Kerberos forged-ticket techniques that modify legitimate TGTs and outlined detection opportunities for Active Directory defenders.
Microsoft Threat Intelligence Center reported that around December 2021 the same threat actor used Mimikatz, WDigest, NTDSDump, and other password-dumping tools to gather credentials.
An NCC Group incident response investigation from May 2017 reported that Playful Taurus used Mimikatz to dump credentials and generate Kerberos Golden Tickets for persistence.
Unit 42 said Playful Taurus, also known as APT15, Ke3chang, and NICKEL, has targeted oil, government, diplomatic, military, and non-governmental organizations since 2010.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
Get the adversaries, campaigns, and ATT&CK mapping behind this technique, with detections ready to deploy.
1 reference tracked. Mallory keeps watching after this page renders.
Map indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Semperis disclosed two Active Directory privilege-escalation vulnerabilities involving hidden and unfilterable Unicode characters that can undermine Microsoft’s identity protections. The first flaw, **KerberLoss** (`CVE-2026-25177`), lets a low-privileged user with service principal name (SPN) write permissions bypass SPN and SPN-alias uniqueness checks, enabling denial of service against `HOST`-mapped services, SPN-jacking in constrained delegation scenarios, and forced Kerberos-to-NTLM downgrade. The second flaw, **ResetNightmare** (`CVE-2026-27912`), is more severe and allows an attacker who can write a user principal name (UPN) on a user or computer object to abuse NT-ENTERPRISE name handling and the Kerberos password-change protocol to reset a privileged account’s password and gain Domain Admin access. The findings build on Microsoft’s earlier hardening work for `CVE-2021-42282`, which introduced uniqueness verification for UPNs, SPNs, and SPN aliases, but the new research shows those checks could still be bypassed under certain conditions. Microsoft patched **KerberLoss** in March 2026 and **ResetNightmare** in April 2026. Defenders were urged to update domain controllers, restrict delegated rights that allow SPN or UPN modification, and monitor Active Directory changes—particularly suspicious SPN and UPN edits such as **Event ID 5136**—for signs of exploitation.
Aug 6, 2026
Incident response findings and large-scale Active Directory assessments show that attackers can often escalate from a low-privileged account to **full domain compromise** by chaining common identity weaknesses. Microsoft reported repeated cases of "total identity compromise" tied to excessive privilege, weak password policies, poor credential hygiene, insecure delegation, ACL abuse, Group Policy abuse, trust relationship weaknesses, and exposure of other Tier 0 assets. Separate analysis of 250 PingCastle reports found the same patterns at scale, including delegable administrator accounts, Kerberoast exposure, weak Kerberos encryption, dangerous Group Policy assignments, and exploitable Print Spooler configurations on domain controllers. The assessments also highlighted persistent weaknesses in **Active Directory Certificate Services (AD CS)** and service account management. Research on **Certified Pre-Owned** and AD CS hardening showed that certificate template and enrollment misconfigurations can let attackers impersonate privileged users and gain durable access, while DFIR reporting found widespread service accounts with non-expiring passwords, excessive privileges, and Kerberoastable administrator accounts. Microsoft guidance points defenders toward continuous AD auditing with tools such as Defender for Identity, BloodHound, and PingCastle, along with privilege reduction, stronger authentication, hardened delegation and trust settings, and tighter governance of managed and legacy service accounts to close common escalation paths.
Aug 1, 2026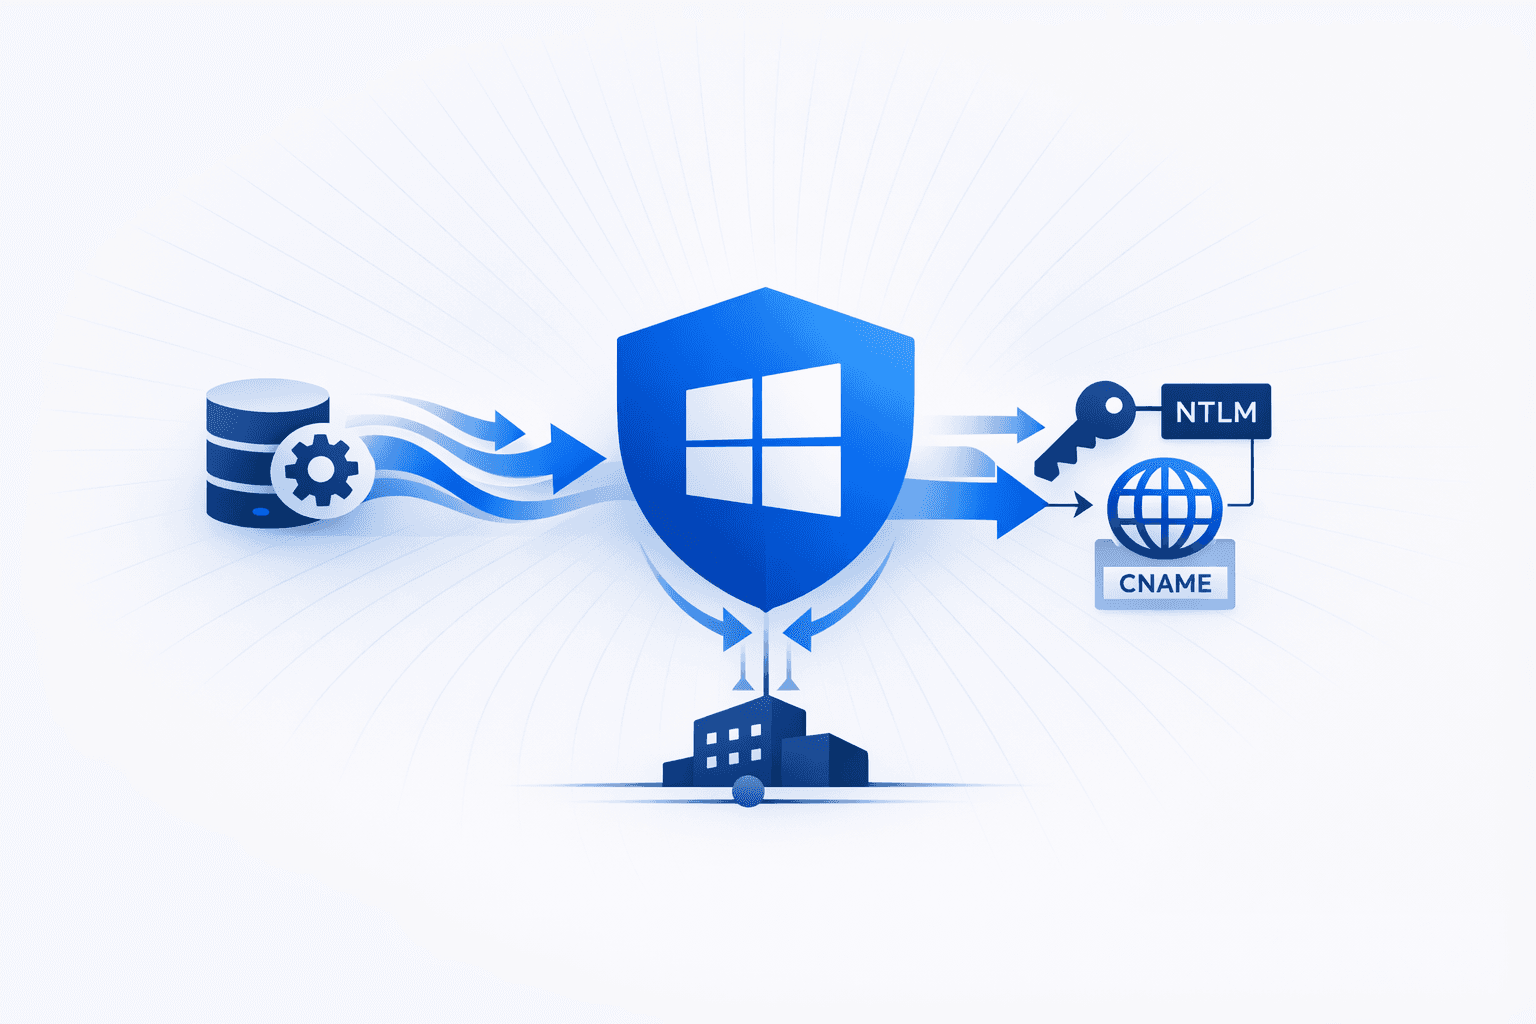
Two separate Windows authentication weaknesses were highlighted as enabling high-impact **Active Directory** compromise via relay-style attacks. One issue, **CVE-2025-33073**, affects Windows **SMB client** authentication and enables **NTLM reflection**: attackers can coerce `lsass.exe` (running as **SYSTEM**) to authenticate to attacker-controlled infrastructure using techniques such as *PetitPotam*, *DFSCoerce*, and *Printerbug*, then relay/reflect that authentication to gain SYSTEM-level access and potentially full domain compromise. Reporting emphasized that despite a June 2025 patch, the condition remains widely present in enterprise environments due to incomplete patch adoption, and exploitation can be enabled with relatively low prerequisites such as the ability to register a malicious AD DNS record (often permitted to Authenticated Users by default) or to perform local DNS poisoning. A second technique described a **Kerberos relay** vector that abuses how Windows clients process **DNS CNAME** responses when building the SPN for TGS requests, allowing an on-path attacker (e.g., via ARP poisoning or DHCPv6/mitm6) to redirect victims to attacker-controlled services and obtain service tickets usable for relays and lateral movement. The write-up claims default configurations across Windows 10/11 and Windows Server 2022/2025 are susceptible, with potential impact including cross-protocol relays (e.g., HTTP→SMB/LDAP) and paths to RCE in some environments (e.g., via ADCS web enrollment scenarios). A separate Metasploit weekly wrap-up noted new and updated offensive modules (including AD privilege-escalation content), but it did not specifically tie to either of the two relay issues above.
Jun 30, 2026