
Loading story…
Ukraine’s military intelligence agency, HUR, said it carried out a cyberattack against Wildberries, Russia’s largest online marketplace, in coordination with the hacker group Cyber Corps. According to the claim, the operation disrupted customer service, contact centers, and payment infrastructure, with customers reportedly encountering failed payments and service outages.
Ukrainian officials said the cyber operation was timed to amplify the effects of drone strikes on Wildberries’ logistics infrastructure, portraying the company as a strategic target because of its role in Russia’s logistics network and alleged support for the war effort, including sales of military-related goods. The reported impact and extent of damage had not been independently verified, and Wildberries had not publicly commented at the time of reporting.
TTPs, infrastructure, and targeting history in one profile.
3 events from the most recent confirmed update back to the earliest known activity.
In September 2025, HUR said it hacked Russian election systems and other government services in response to voting held in occupied Ukrainian territories.
In June 2025, Ukraine's military intelligence agency HUR said it breached the internal systems of Russian state-owned aircraft manufacturer Tupolev following Ukrainian drone attacks on Russian air bases.
Ukraine's Main Intelligence Directorate, working with the Cyber Corps hacker group, claimed it conducted a cyberattack against Russian e-commerce giant Wildberries. HUR said the operation disrupted customer service, contact centers, and payment infrastructure, with customers reportedly unable to complete payments.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
2 references tracked. Mallory keeps watching after this page renders.
cyberveille.ch
Open sourcetherecord.media
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Ukraine faced a series of disruptive cyberattacks targeting government ministries, the Defense Ministry, state portals, and major banks, culminating in what officials called the largest **DDoS** campaign in the country’s history. On 15 February, attacks knocked or degraded access to services at PrivatBank, Oschadbank, the Ministry of Defense, government websites, and the **Diia** platform, with Ukrainian officials saying roughly 15 banks were affected. Authorities said the operation had been prepared in advance, originated from multiple countries, and was intended to destabilize society and trigger panic; they also said no theft of funds or personal data had been confirmed, while U.S. partners helped provide technical support and additional protections. The February disruption followed an earlier January intrusion in which multiple Ukrainian ministry websites were hit and a defacement message in Russian, Polish, and Ukrainian falsely warned that citizens’ personal data had been leaked and destroyed. Ukrainian officials said no personal data leak was verified, while the **EU** and **NATO** publicly backed Kyiv and expanded cyber assistance, including closer cooperation and access to malware-sharing resources. The incidents fit a longer pattern of cyber operations against Ukraine, including the **NotPetya** attack that previously disrupted government bodies, banks, utilities, logistics firms, and airport operations and was later publicly attributed by the UK and US to Russia, an accusation Moscow has denied in more recent cases.
Jun 29, 2026
Russian-linked cyber operations hit Ukraine at the outset of the invasion with both destructive malware and a major satellite communications disruption. Security researchers identified the **HermeticWiper** data-wiping malware on hundreds of systems in Ukraine, with additional impacts reported at a Ukrainian financial institution and government contractors in Latvia and Lithuania. The activity coincided with **DDoS** attacks against Ukrainian government entities and PrivatBank, underscoring a coordinated effort to degrade communications and critical services as military operations began. A parallel attack on Viasat’s **KA-SAT** network knocked 40,000 to 45,000 satellite modems offline, many of them permanently, after attackers compromised a VPN-connected management center in Turin and pushed wiper malware through a software update server. Viasat later said the incident unfolded in two stages, with a second wave using compromised modems to flood company systems and complicate recovery; the disruption spilled into Europe, including outages affecting **5,800 Enercon wind turbines in Germany**. U.S. and EU officials attributed the operation to Russian hackers, and the investigation helped support sanctions announced in 2022.
Jun 29, 2026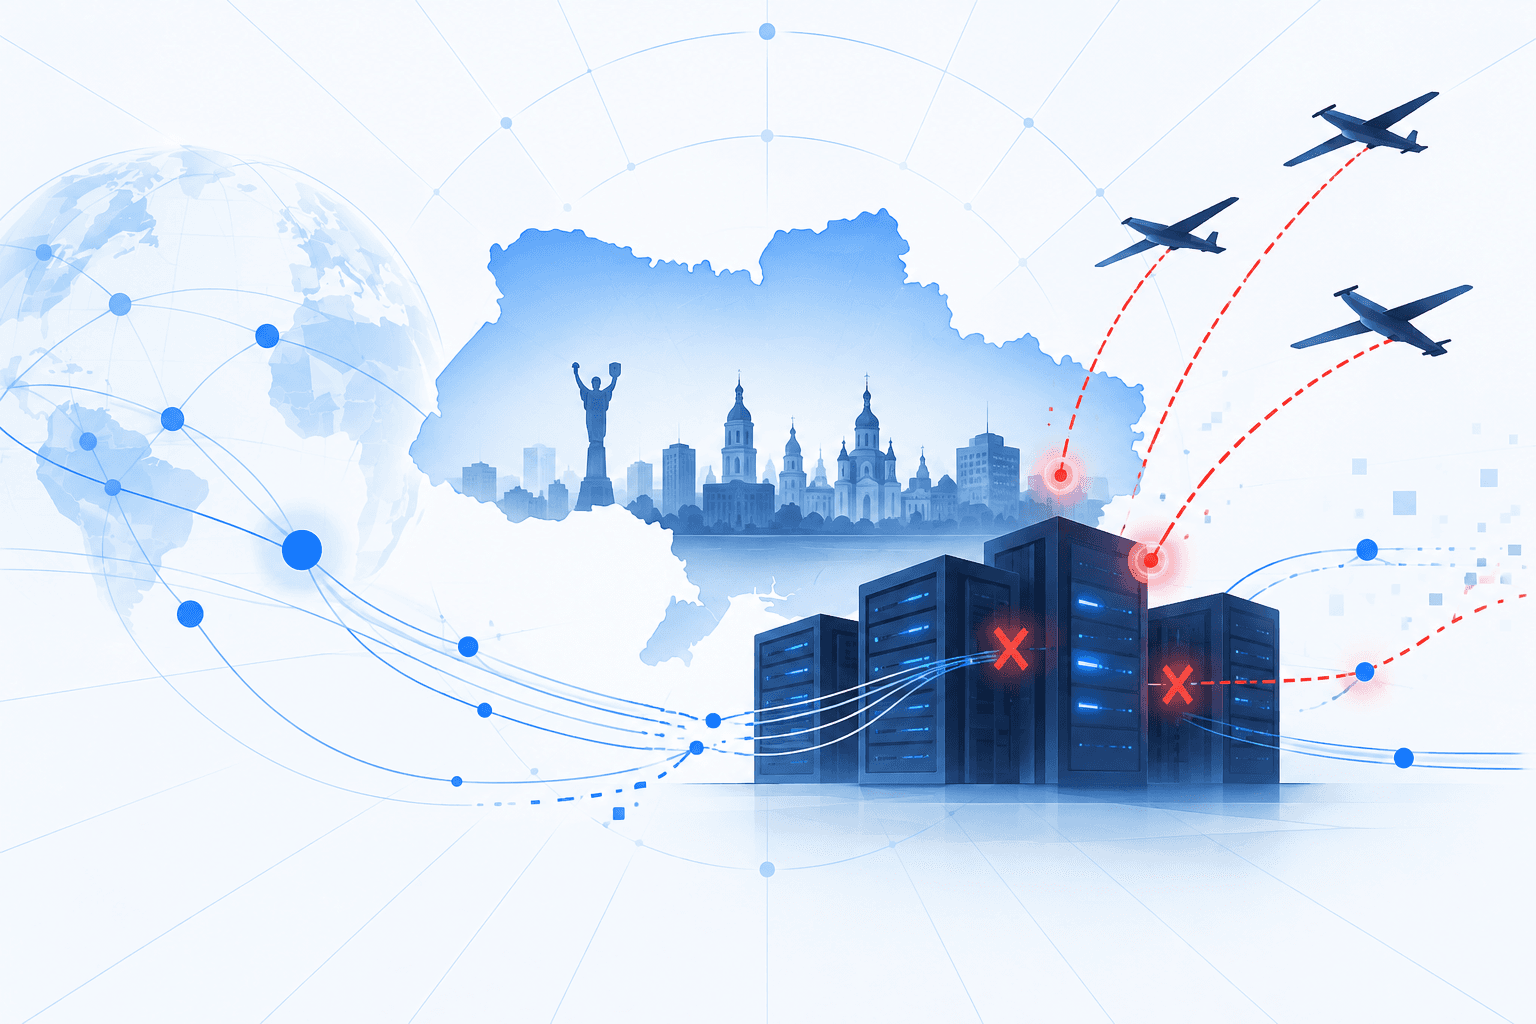
Russian drone strikes damaged commercial data-center and telecommunications infrastructure in Kyiv, disrupting connectivity for roughly **100,000 households**. At least four providers—Kyiv Link, Pautina, Utels, and Crazy Network—reported outages or degraded service caused by damage to facilities, critical equipment, communications lines, and a traffic-exchange site. A strike on a Datagroup data center in Kyiv’s central business district also killed four people in the surrounding area. Russia acknowledged targeting the Datagroup site and said it struck or sought facilities associated with New-Telco, United DC, Kyivstar, and Parkovyi, alleging links to Ukrainian military or security services; those claims were not independently verified. Ukrainian officials said the country’s decentralized network architecture should prevent nationwide failure, but warned that localized outages could impair air-raid alerts and other essential civilian services. Some companies have begun moving data abroad in response to the heightened risk.
Sep 26, 2026