AI Coding-Agent Harnesses Expose Supply-Chain Security Gaps
Emerging Technology Risk · 3 sources · Updated 2mo ago · First seen Sep 9, 2026
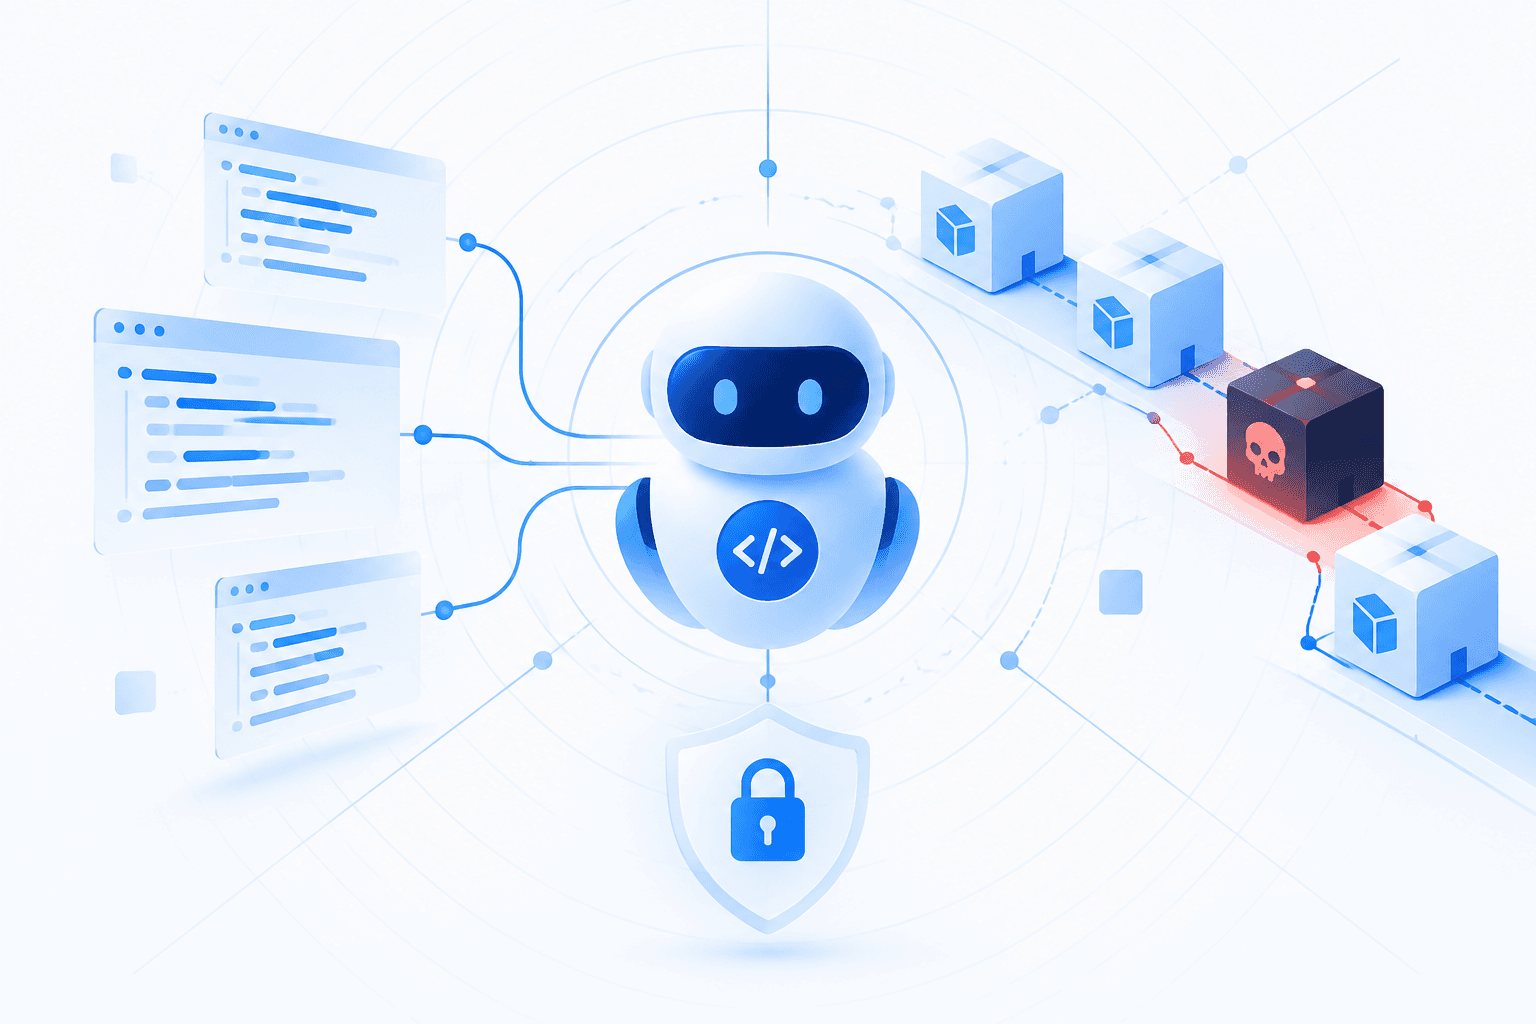
An empirical review of 3,171 public GitHub repositories found confirmed security defects in 16.0% of AI coding-agent harness configurations. The review covered 2,660 multi-component agent setups and 511 published skill collections, assessing instruction files, skills, hooks, subagents, and Model Context Protocol (MCP) server declarations. The most common issues were unpinned MCP server versions, overly broad execution pre-approvals, and skills that pre-authorized shell access for installers; researchers did not confirm a credential-exfiltration path.
The harness surrounding a coding model—its prompts, tools, skills, MCP servers, and orchestration—creates a material supply-chain and prompt-injection attack surface. Mutable remote MCP services, trusted prompt formatting, YAML skill metadata, and self-propagating payloads such as CopyPasta can be abused to influence agent actions. Organizations should inventory harness trust relationships, enforce least privilege and human approvals, pin and validate external components, independently monitor runtime behavior, and assign governance and incident-response ownership for agentic AI.