UNC3569 Exploits Sogou Input Method RCE to Deploy GRAYRABBIT
Active Exploitation · 6 sources · Updated 2mo ago · First seen Jul 10, 2026
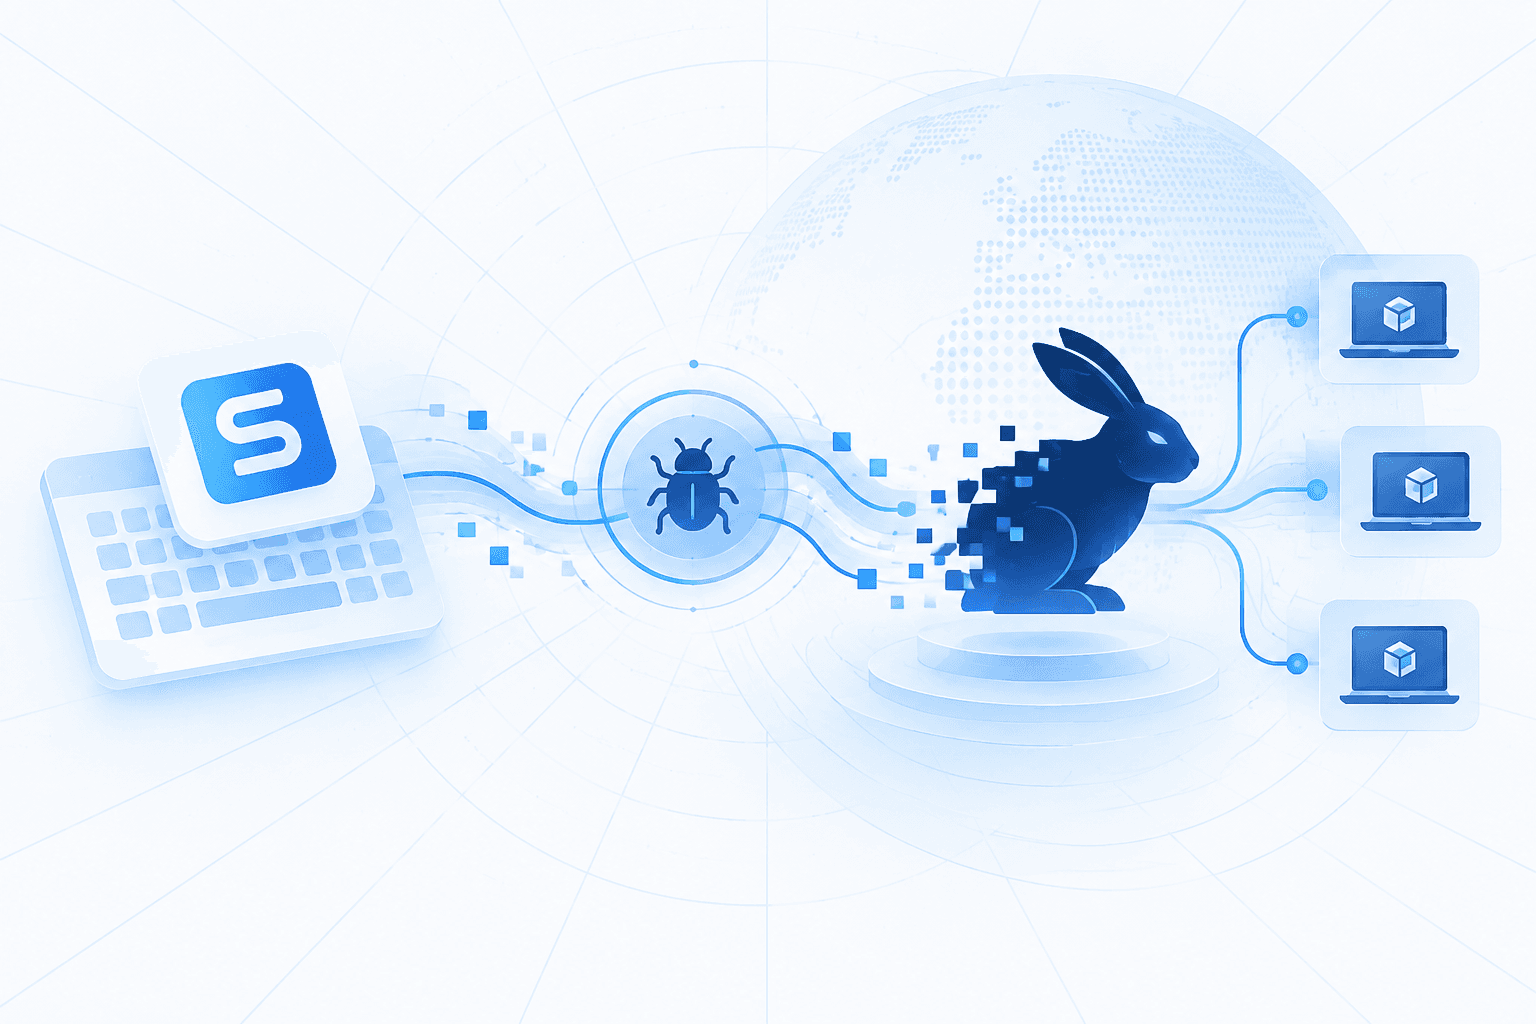
China-linked threat actor UNC3569 actively exploited critical remote-code-execution flaw CVE-2026-51990 in Tencent Sogou Input Method for Windows to install the GRAYRABBIT backdoor. Victims could be compromised through a crafted sgbiz: link that injected attacker-controlled arguments, opened Sogou's Skin Center CEF webview at a malicious site, and exploited the Chromium V8 vulnerability CVE-2021-38003 to execute code in the logged-in user's context.
Tencent released Sogou Input Method version 16.3.0.3498 through automatic updates, adding validation for URL-bearing protocol-handler arguments. However, researchers reported that the application continues to embed Chromium 80 with its sandbox and web-security/same-origin protections disabled. GRAYRABBIT used 7-Zip DLL sideloading, anti-analysis and self-deletion measures, and RC4-obfuscated non-TLS command-and-control traffic over TCP port 443.