Hacking Cat Linked to Gorilla RAT and Destructive Malware Against Russian Targets
Threat Actor Intelligence · 3 sources · Updated 1mo ago · First seen Sep 11, 2026
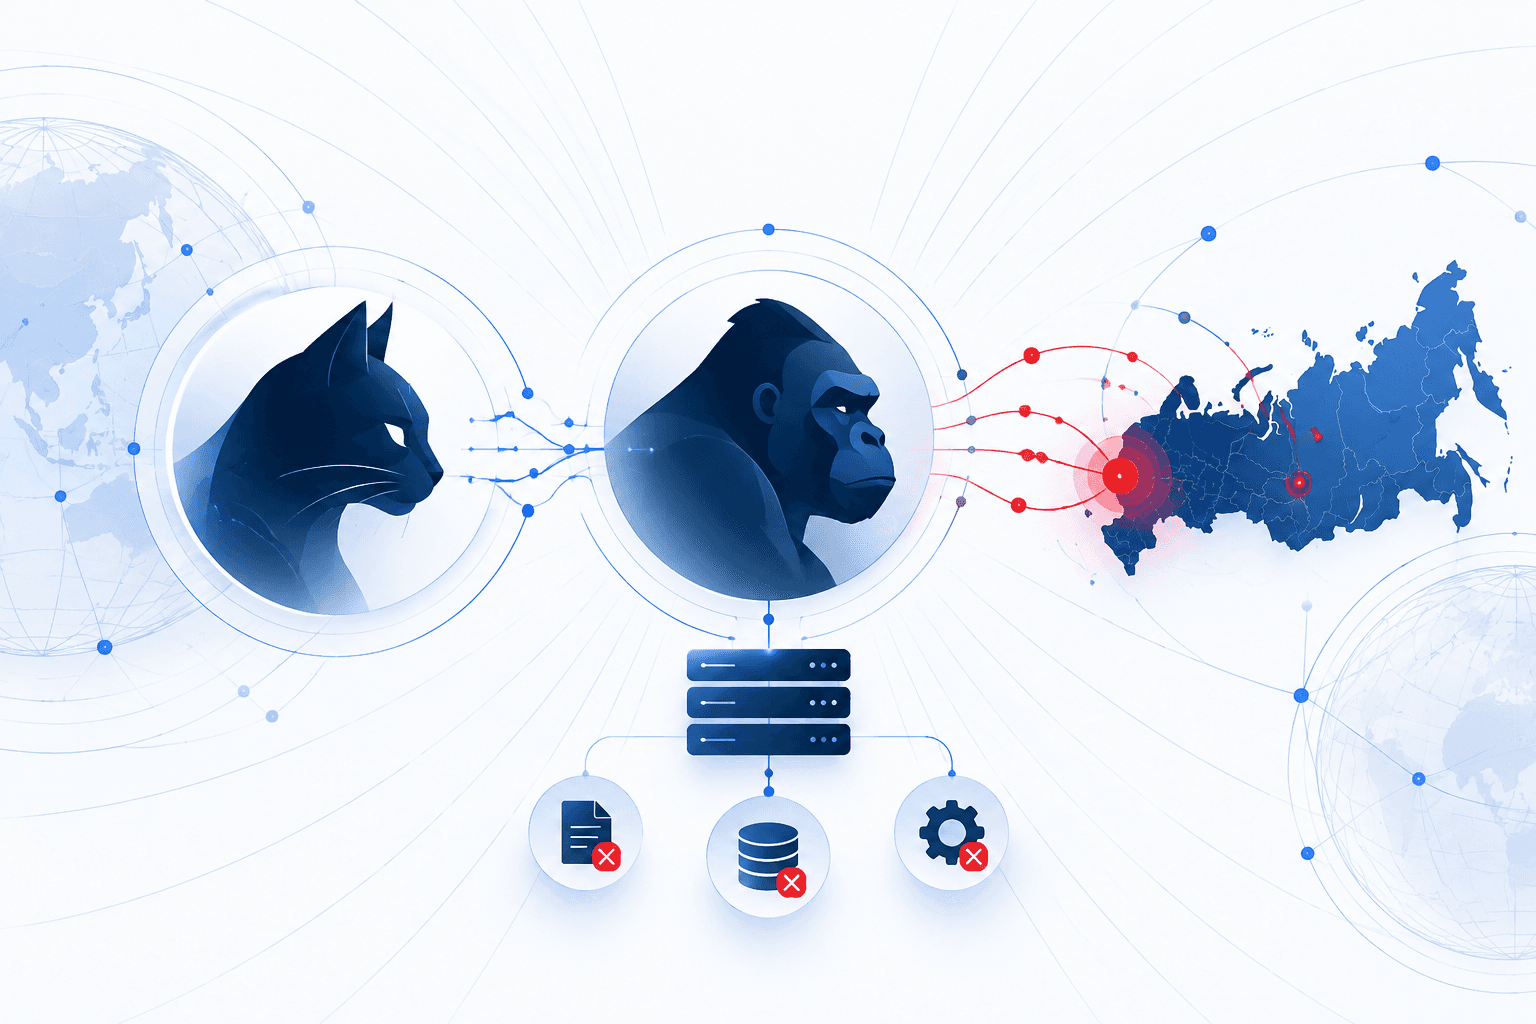
Pro-Ukraine hacktivist group Hacking Cat has escalated operations against Russian organizations from website defacements and data leaks to campaigns that encrypt or destroy victim data. Kaspersky assessed with high confidence that the group uses the previously undocumented Go- and WebSocket-based Gorilla RAT, which supports command execution, file transfers, TCP tunneling, and—in some variants—VNC control; reported intrusions have at times followed exploitation of Microsoft Exchange vulnerabilities.
The activity has also been linked to cross-platform Monkey Ransomware variants targeting Windows, Linux, and ESXi, including Rust-based samples that do not preserve decryption keys and therefore operate effectively as wipers despite presenting ransom demands. Researchers observed overlaps with Ukraine-linked groups including Cyber Anarchy Squad and Ukrainian Cyber Alliance, such as ClearWater ransomware and a delivery chain for Nemo Wiper, while noting only tentative infrastructure and operational ties to Thor. Hacking Cat disputed the attribution, saying it owns certain tools but denying responsibility for the ransomware lockers.