Compromised HBO Max Reddit Account Served PasteSwitch ClickFix Malware Ads
Malware Intelligence · 17 sources · Updated 1mo ago · First seen Sep 14, 2026
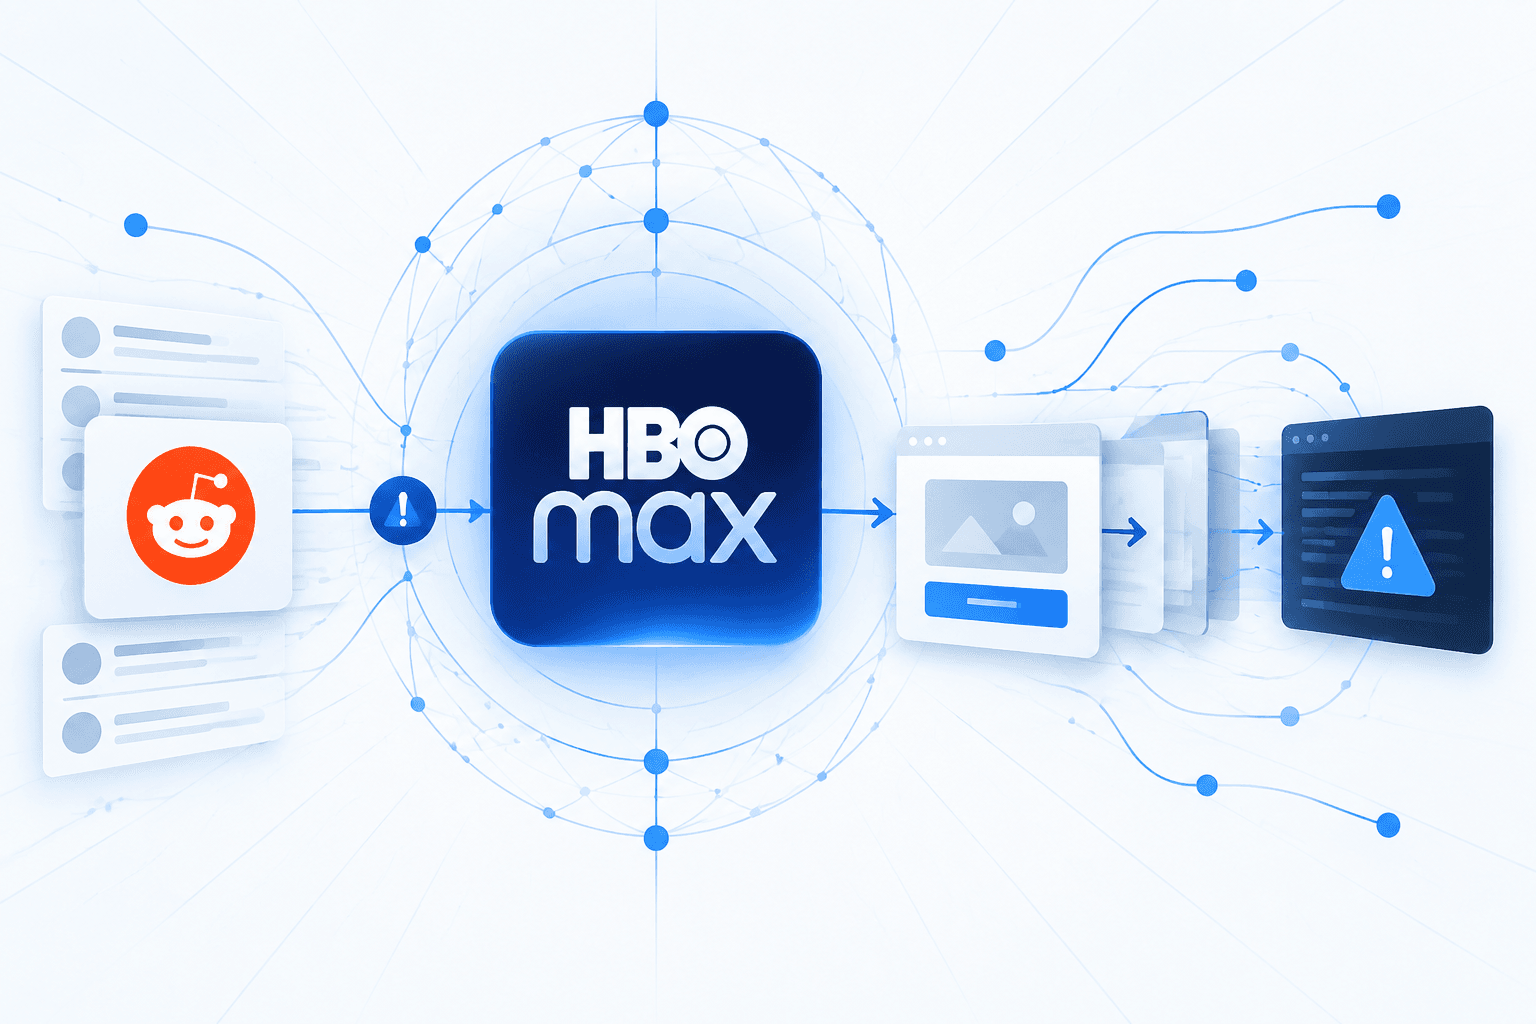
Attackers compromised the verified Reddit account u/hbomax and used it to run 108 malicious advertisements over roughly 48 hours. The ads impersonated HBO Max, AI-development tools, and macOS utilities, directing targets into a ClickFix campaign researchers call PasteSwitch that persuaded victims to copy and execute commands in a terminal or Windows Run dialog.
The copied commands selected payloads by operating system: macOS victims received MacSync and AMOS Helper stealers, while a Windows InstallFix chain loaded Amatera Stealer in memory. The campaign also deployed fake cryptocurrency wallets and crypto clippers, using direct-to-IP TLS communications and Binance Smart Chain smart contracts to rotate clipper command-and-control domains. Reddit paused the malicious ads and began an internal investigation to secure the compromised account.