Mallory
← Back to News
state-sponsored-espionageremote-access-implantcommand-and-control-methodcredential-stealer-activity

Iranian MOIS Actors Deploy HEAVYGRAM Malware Through Telegram C2

Threat Actor Intelligence · 7 sources · Updated 2mo ago · First seen Sep 15, 2026
Iranian MOIS Actors Deploy HEAVYGRAM Malware Through Telegram C2

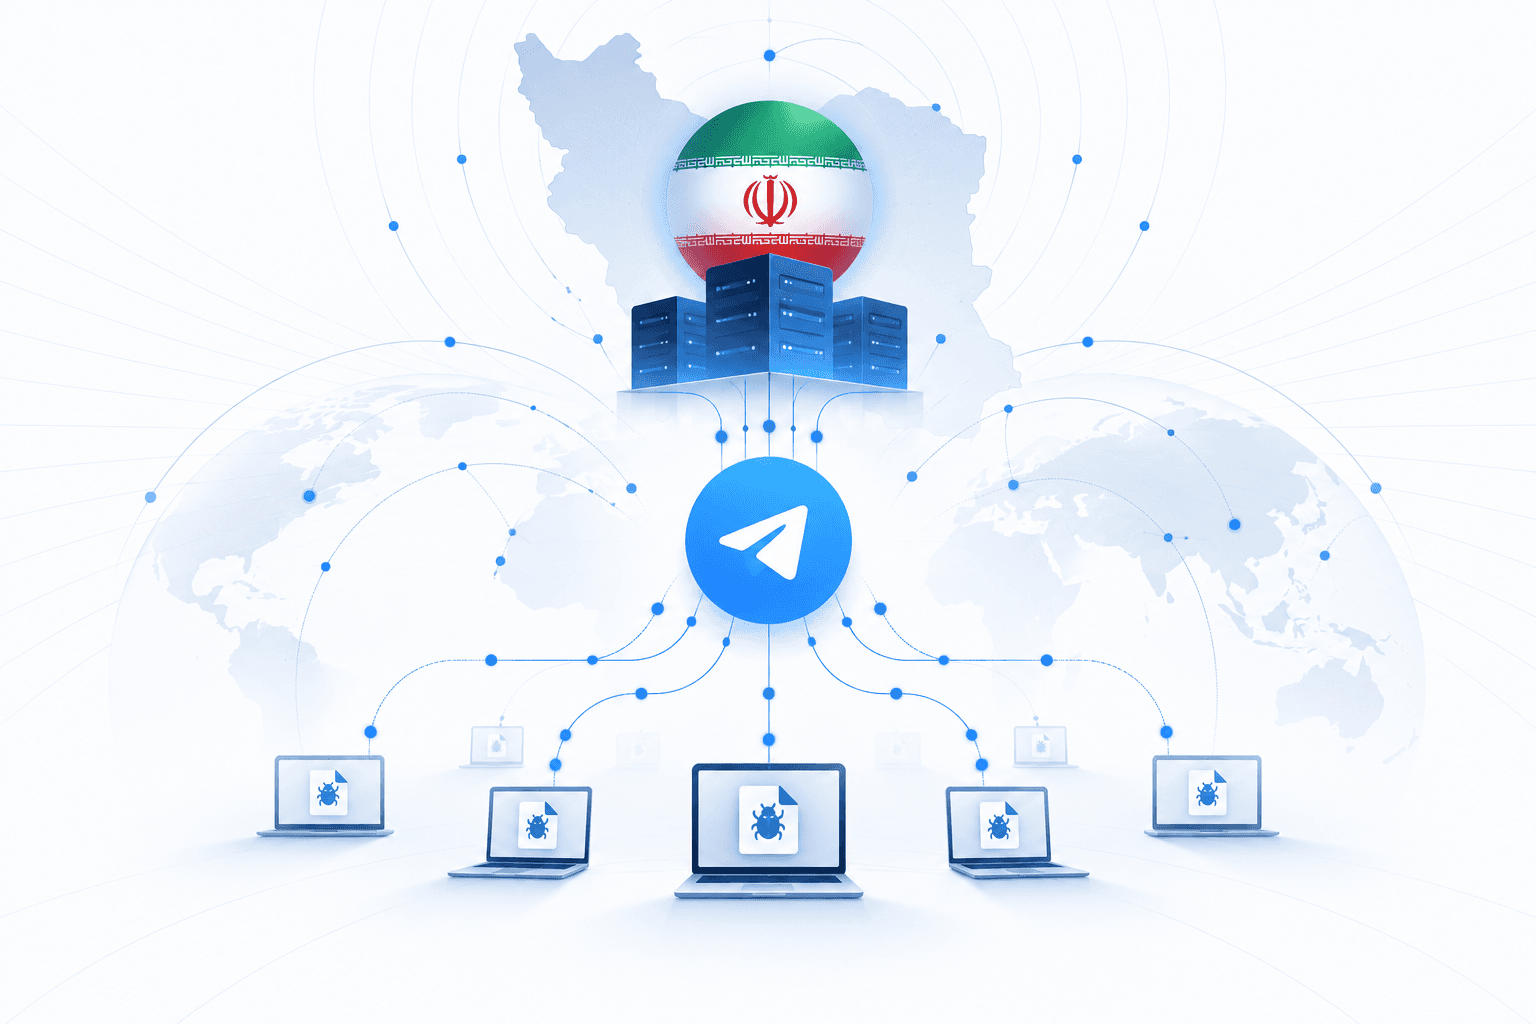
The FBI assesses that cyber actors linked to Iran’s Ministry of Intelligence and Security (MOIS) have used the modular Windows malware framework HEAVYGRAM since fall 2023 against Iranian dissidents, anti-government journalists, opposition groups, and other individuals Tehran considers threats worldwide. The operators use Telegram, WhatsApp, and Instagram social-engineering lures, impersonating IT-service providers to persuade targets to install AnyDesk or trojanized applications posing as Pictory Premium, Telegram Authenticator, and KeePass.

HEAVYGRAM uses Telegram Bot API infrastructure for command-and-control and data exfiltration, while Vultr S3 storage supports payload and data staging. Its implants can conduct host reconnaissance, execute commands, capture screenshots, steal browser credentials and sessions, collect Telegram and WhatsApp data and Outlook and Gmail content, and access removable media; optional modules enable screen and audio recording. Organizations supporting at-risk Iranian communities should scrutinize suspicious remote-access deployments and look for Telegram-based C2 activity, credential theft, and counterfeit software installers.
Know this adversaryTTPs, infrastructure, and targeting history in one profile.
Get the profile
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

6 events · 2023 – Mar 19, 2026
  1. Reported Sep 18, 20262mo ago

    Gurucul publishes HEAVYGRAM lures, hosting URLs, and file hashes

    Gurucul documented HEAVYGRAM lure filenames, Vultrobjects object-storage payload-hosting URLs, and associated MD5, SHA-1, and SHA-256 hashes. The report also detailed the backdoor's Telegram-based command-and-control and exfiltration, screenshot capture, remote command execution, persistence, and DLL sideloading capabilities.

    HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack | Community Portal | Gurucul
  2. Reported Sep 17, 20262mo ago

    Handala Hack assessed as a Void Manticore persona

    Handala Hack was assessed to be operated by Void Manticore, also known as Banished Kitten, Red Sandstorm, and Storm-0842, an actor affiliated with Iran's Ministry of Intelligence and Security. The assessment links this persona to the HEAVYGRAM backdoor and CRUDEEXCLUDE defense-evasion utility.

    Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
  3. Reported Sep 17, 20262mo ago

    Group-IB links HEAVYGRAM operation to Handala Hack

    Group-IB assessed with moderate confidence that the HEAVYGRAM surveillance operation is linked to Handala Hack and identified 29 additional HEAVYGRAM-related samples, loaders, and payloads. The investigation also associated CRUDEEXCLUDE with the campaign, noting that it may create security-exclusion paths before HEAVYGRAM deployment.

    Hackers Turn Telegram Into a Command Center for HEAVYGRAM Surveillance Malware | Cryptika Cybersecurity
  4. Mar 19, 20268mo ago

    DOJ seizes four MOIS-linked domains tied to HEAVYGRAM

    The U.S. Department of Justice announced the seizure of four MOIS-linked domains, including Justicehomeland[.]org, Karmabelow80[.]org, Handala-Redwanted[.]to, and Handala-Hack[.]to. Its affidavit also described HEAVYGRAM intrusions involving a UK-based Farsi-language journalist and a separate U.S.-based victim.

    HEAVYGRAM: A Telegram-based Surveillance Backdoor Linked to Handala Hack | Group-IB Blog
  5. 2023

    MOIS-linked actors begin HEAVYGRAM targeting campaign

    FBI assesses that Iranian Ministry of Intelligence and Security cyber actors began using HEAVYGRAM against Iranian dissidents, anti-government journalists, opposition organizations, and other perceived threats worldwide. The actors used social engineering on Telegram, WhatsApp, and Instagram to induce targets to install AnyDesk or trojanized software.

    Ic3 Alerts
  6. Date unknown

    FBI issues updated HEAVYGRAM malware analysis and indicators

    The FBI released an updated FLASH containing technical analysis and additional indicators for HEAVYGRAM, assessing that MOIS actors use the malware for intelligence collection, data leaks, and reputational harm on behalf of Iran.

    Ic3 Alerts
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

2 linked

Malware

1 linked

Organizations

3 linked
Government of IranMinistry of Intelligence and SecurityMinistry of Intelligence and Security of Iran

Observables

135 linked

Indicator values are masked on this page. View all 135 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
Get the Full Actor Profile
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.