x47.c Windows Botnet Drains AI API Credits Using Stolen Keys
Malware Intelligence · 5 sources · Updated 1mo ago · First seen Sep 23, 2026
The previously undocumented x47.c Windows botnet is being marketed by WraithTools with 18 attack capabilities, including credential theft, SOCKS5 proxying, fast-flux infrastructure, DDoS attacks, and AI-assisted persistence and host concealment. Its persistence module reportedly uses xAI's Grok to select from predefined persistence and evasion actions on compromised hosts.
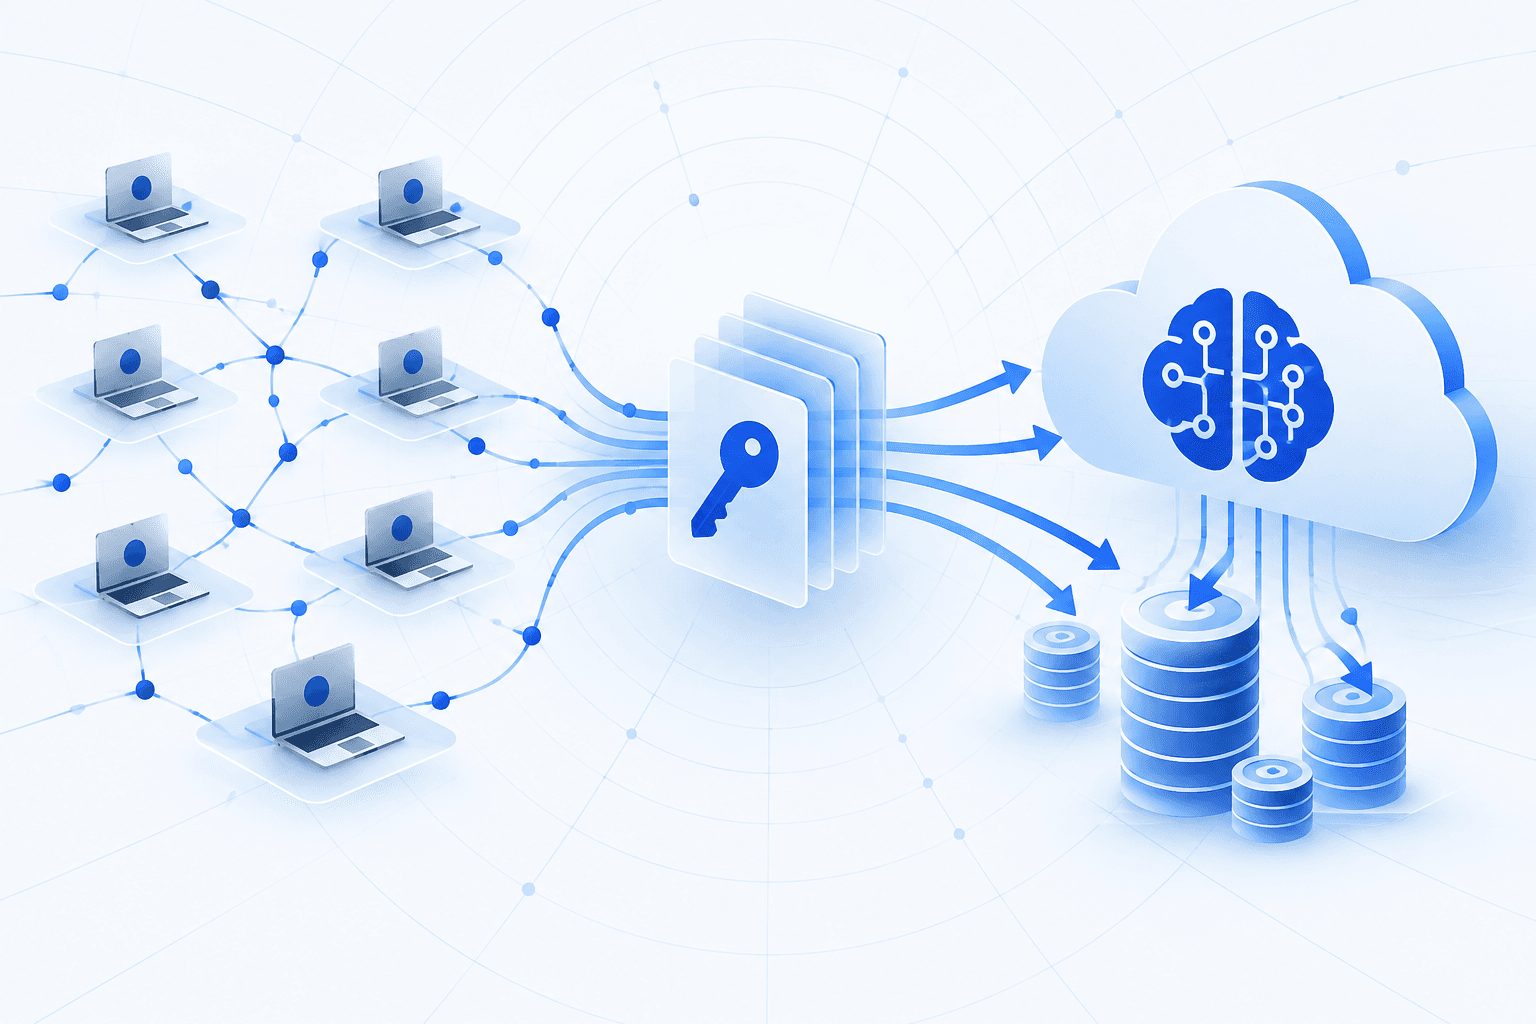
x47.c's "AI API drain" capability uses valid stolen or exposed API keys to send repeated billable requests directly to OpenAI, xAI, and compatible AI providers, exhausting a victim's credits while potentially leaving the victim-facing application functional. The activity represents a denial-of-wallet attack; organizations should revoke exposed AI keys, investigate anomalous usage and billing, enforce spending caps and limits on automatic top-ups, remediate infected endpoints, and maintain layered application- and network-level DDoS protections.