MacSync macOS Stealer Adds Backdoor and iCloud-Based Delivery
Malware Intelligence · 11 sources · Updated 1mo ago · First seen Sep 24, 2026
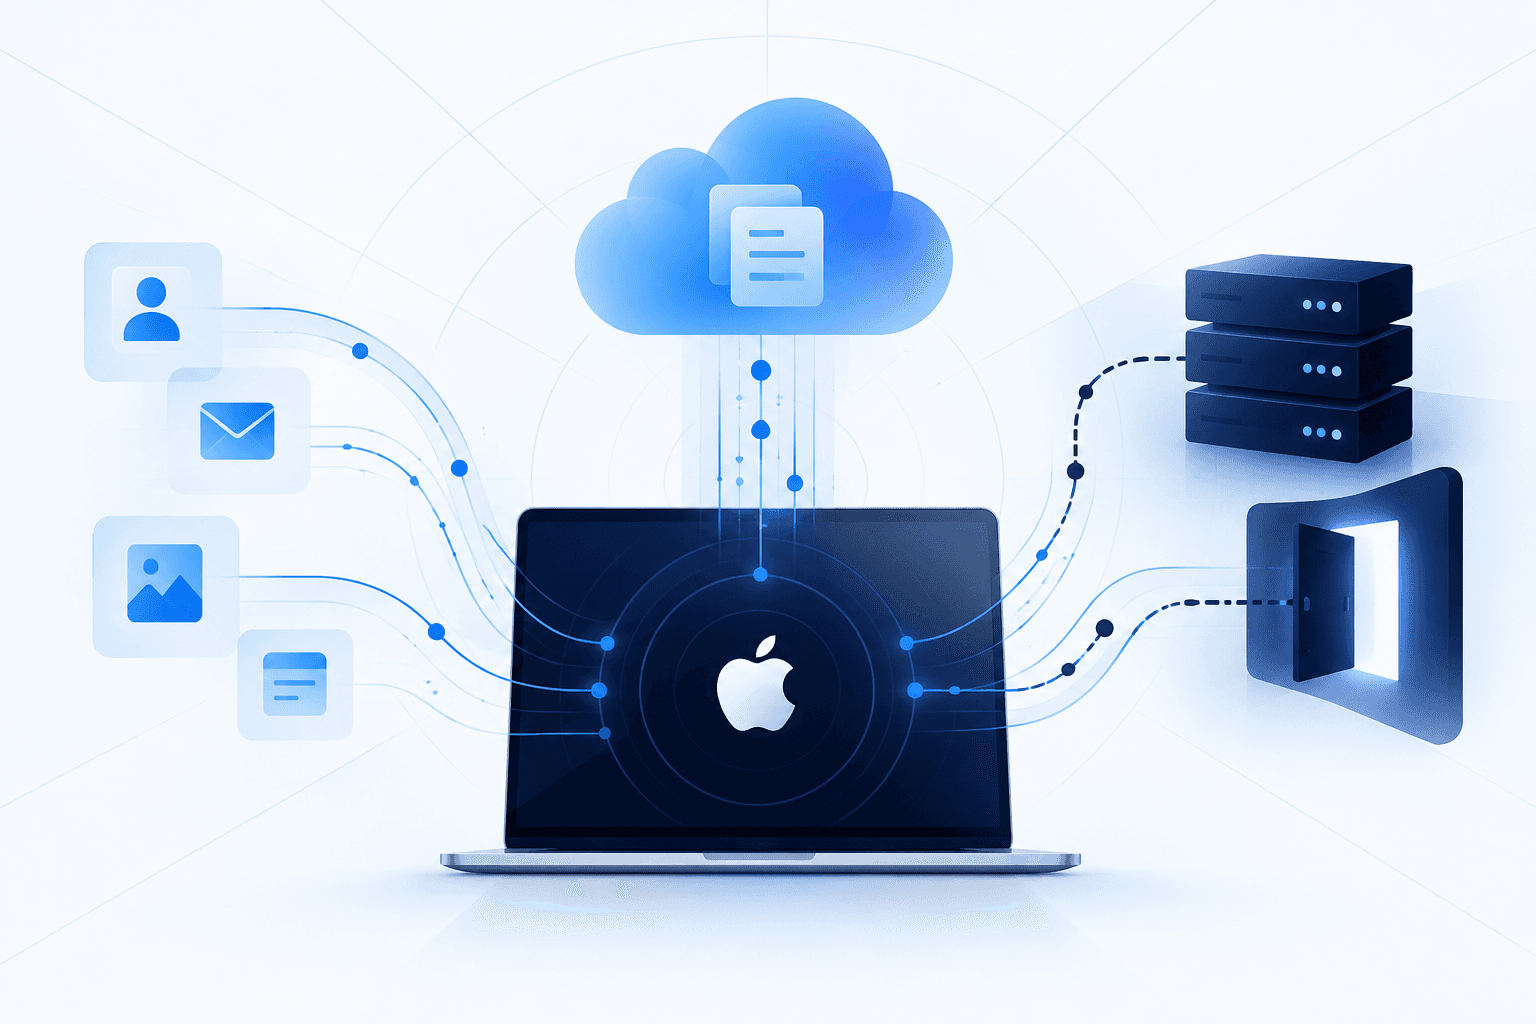
A new MacSync malware-as-a-service campaign targets macOS cryptocurrency users and developers with trojanized DMG applications, binary loaders, and droppers. Originally advertised as Mac.c in 2025, the stealer has progressed from AppleScript payloads to Swift and Objective-C binaries and now uses Apple iCloud Calendar and file-hosting infrastructure to retrieve subsequent payloads.
MacSync collects browser and cryptocurrency-wallet data, credentials, Keychain-related material, Telegram data, cloud and developer configuration files, system details, and shell histories. It persists through LaunchAgents, modified ZSH settings, global Git hooks, Login Items, and restoration scripts while suppressing user notifications; its backdoor can receive C2 tasks to install browser extensions, replace Ledger wallet software, repeat collection, and potentially intercept browser traffic.