Mallory
← Back to News
leaked-secret-api-keyoperational-disruptioncloud-misconfigurationcredential-access-method

Storm-3168 Used Compromised Azure Service Principals to Destroy Cloud Resources

Breach & Incident Intelligence · 8 sources · Updated 2mo ago · First seen Sep 25, 2026
Storm-3168 Used Compromised Azure Service Principals to Destroy Cloud Resources

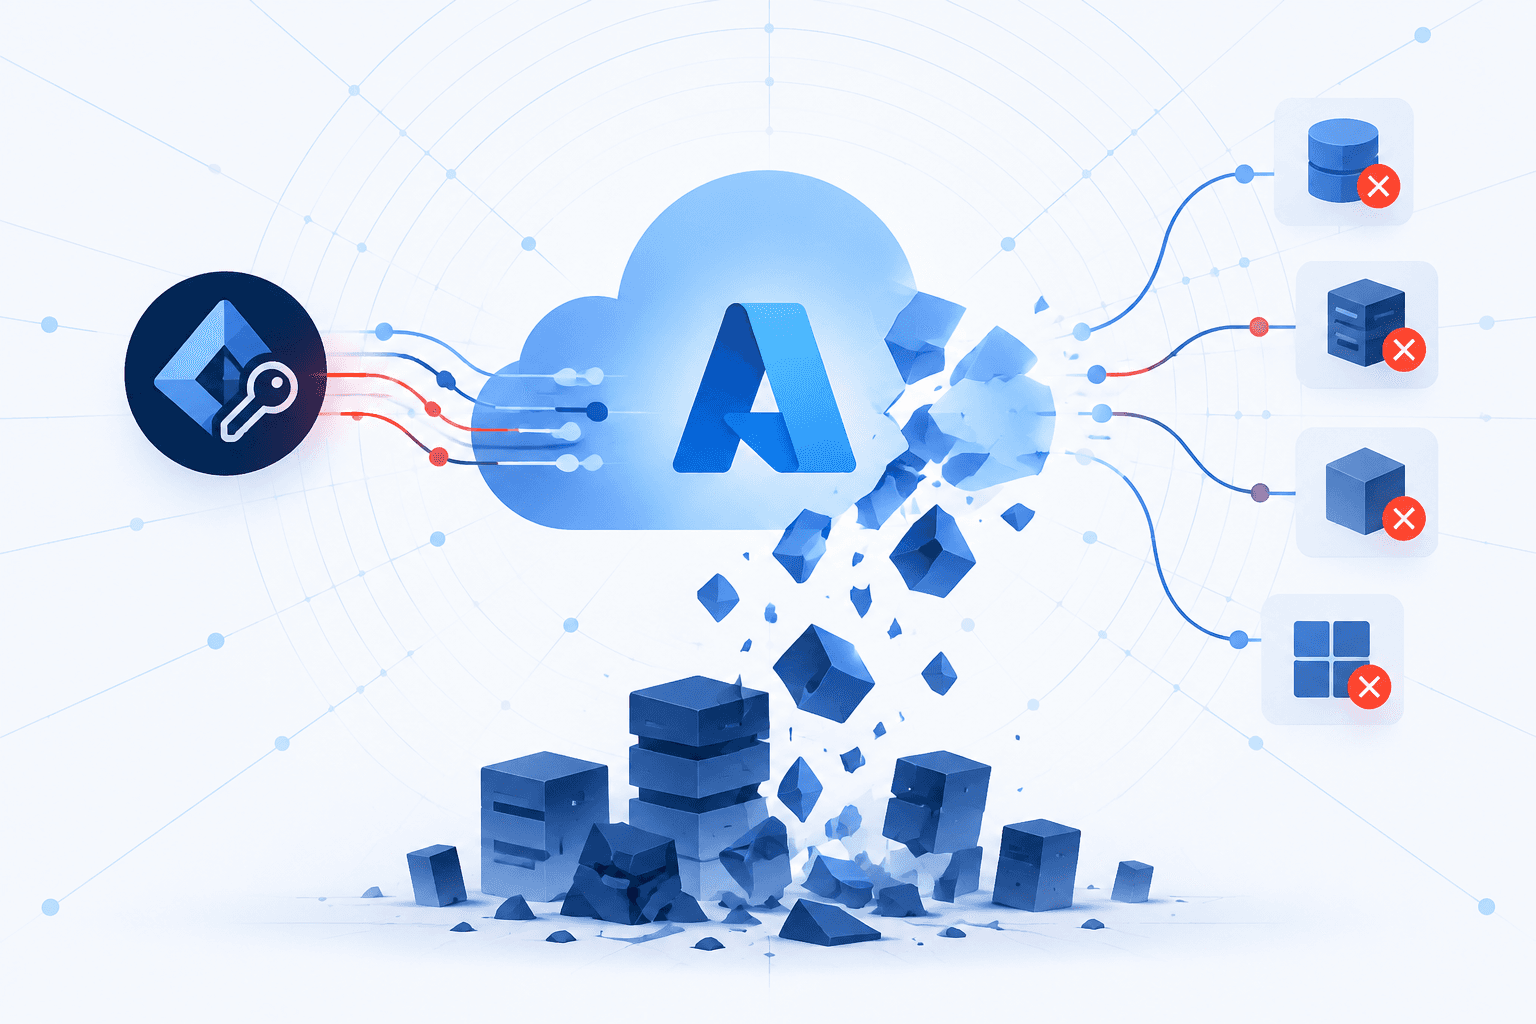
Microsoft attributed destructive Azure activity to JADEPUFFER, tracked as Storm-3168, after the actor used two compromised service principals within one tenant to conduct broad reconnaissance and delete Azure Storage accounts and associated application resources. The operation also attempted to delete SQL databases and recovery-protection controls, an attack pattern consistent with impairing an organization’s ability to recover from a ransomware event.

The actor successfully retrieved keys for more than 30 Azure Storage accounts, which could enable data access or exfiltration, though Microsoft observed neither confirmed data theft nor a ransom note. One compromised service principal’s client ID, secret, and tenant ID had been publicly exposed in a GitHub issue, but Microsoft could not verify that it enabled the intrusion. Microsoft assessed that parallel use of identities and tokens indicated automated or scripted execution, and urged organizations to rotate exposed credentials, enforce least privilege for workload identities, and protect backup and recovery resources.
Is this vendor in your chain?See attribution, scope, and your downstream exposure.
Check the blast radius
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

11 events · Jun 2026 – Jul 2026
  1. Reported Sep 29, 20262mo ago

    Storm-3168-linked infrastructure indicators are reported

    Reported indicators associated with Storm-3168-linked App Service probing and malicious Azure Resource Manager requests include 45.131.66[.]106, 34.153.223[.]102, and 64.20.53[.]230. The underlying probing activity was already documented, but these specific network indicators were not captured in the existing timeline.

    Storm-3168 Deletes Azure Resources in 7-Minute Destructive Cloud Attack
  2. Reported Sep 28, 20262mo ago

    JADEPUFFER exploits Langflow and deploys ransomware

    In an earlier Sysdig-documented campaign, JADEPUFFER exploited Langflow vulnerability CVE-2025-3248, collected and reused credentials, moved laterally, and established persistence. The operation encrypted Nacos service configuration files using MySQL AES_ENCRYPT(), deleted original database tables, and left a Bitcoin ransom demand.

    Напаѓачи поврзани со JADEPUFFER користеле компромитирани Service Principals за бришење Azure ресурси | MKD-CIRT | Национален центар за одговор на компјутерски инциденти
  3. Reported Sep 28, 20262mo ago

    Storm-3168-linked infrastructure probes Azure App Services of several customers

    Microsoft detected repeated probing by infrastructure linked to Storm-3168 against Azure App Services belonging to several customers, indicating activity beyond the previously documented destructive intrusion into one Azure tenant.

    JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources
  4. Reported Sep 25, 20262mo ago

    Service-principal secret exposed in public GitHub issue

    An employee of the affected organization exposed the client ID, client secret, and tenant ID for one compromised Azure service principal in plaintext in a public GitHub issue. The issue was later edited, but the secret remained available in its public edit history; Microsoft could not confirm that it was used for the intrusion.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
  5. Jul 2026

    Sysdig identifies JADEPUFFER as an agentic ransomware operation

    Sysdig discovered JADEPUFFER in July 2026 and described it as the first documented agentic ransomware operation.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
  6. Jun 2026

    Microsoft identifies coordinated use of five service-principal tokens

    Microsoft observed five distinct tokens for the compromised service principal used in deletion and storage-key activity. Four tokens supported deletion operations, including two active concurrently that split Storage and SQL targets, while a fifth token conducted storage inventory and key retrieval; Microsoft said the pattern suggested coordinated automation.

    Storm-3168 Deletes Azure Resources in 7-Minute Destructive Cloud Attack - Cyber Accord
  7. Jun 2026

    Compromised identity retrieves Azure Storage account keys

    About 30 minutes after the final destructive action, the compromised service principal made more than 30 successful ListKeys requests, including against Azure Site Recovery-related storage accounts. The retrieved keys could potentially enable access to or exfiltration of storage data.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
  8. Jun 2026

    Storm-3168 attempts to impair SQL and recovery protections

    During the destructive sequence, the actor attempted parallel deletion of Azure SQL databases and attempted to remove Azure Site Recovery and Azure Backup protection locks. The SQL deletion attempts failed because the actor used an unsupported API version, and the recovery-lock deletion attempts were unsuccessful.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
  9. Jun 2026

    Storm-3168 deletes Azure storage and application resources

    Less than one second after a failed ListKey request against a nonexistent storage account, the second service principal began destructive activity. It attempted more than 100 Azure Storage account deletions, successfully deleting most targets, and also deleted an Azure Key Vault, Function App, and App Service plan; resource locks and deletion protection blocked some storage-account deletions.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
  10. Jun 2026

    Second service principal expands Azure discovery

    About 90 minutes after the initial enumeration began, a second compromised service principal enumerated virtual machines and resource groups across two subscriptions in five seconds. Sixteen hours later, it enumerated App Service configuration stores and unsuccessfully searched for Azure OpenSearch resources.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
  11. Jun 2026

    First compromised service principal reconnoiters Azure tenant

    In early June 2026, a compromised service principal performed more than 300 successful Azure read operations over about 15 hours and 30 minutes, enumerating virtual machines, subscriptions, resource groups, and other resources.

    Storm-3168: Agentic-driven cloud attacks using compromised service principals - Malware News - Malware Analysis, News and Indicators
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Threat actors

2 linked

Malware

1 linked

Affected products

5 linked
Azure FunctionsAzure Key VaultAzure App ServiceAzure Sql DatabaseAzure Virtual Machines

Observables

3 linked

Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?See attribution, scope, and whether this vendor sits anywhere in your supply chain.
Get the Full Incident Picture
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.