Elementor CSRF Flaw Lets Attackers Create WordPress Administrator Accounts
Vulnerability Disclosure · 6 sources · Updated 1mo ago · First seen Sep 25, 2026
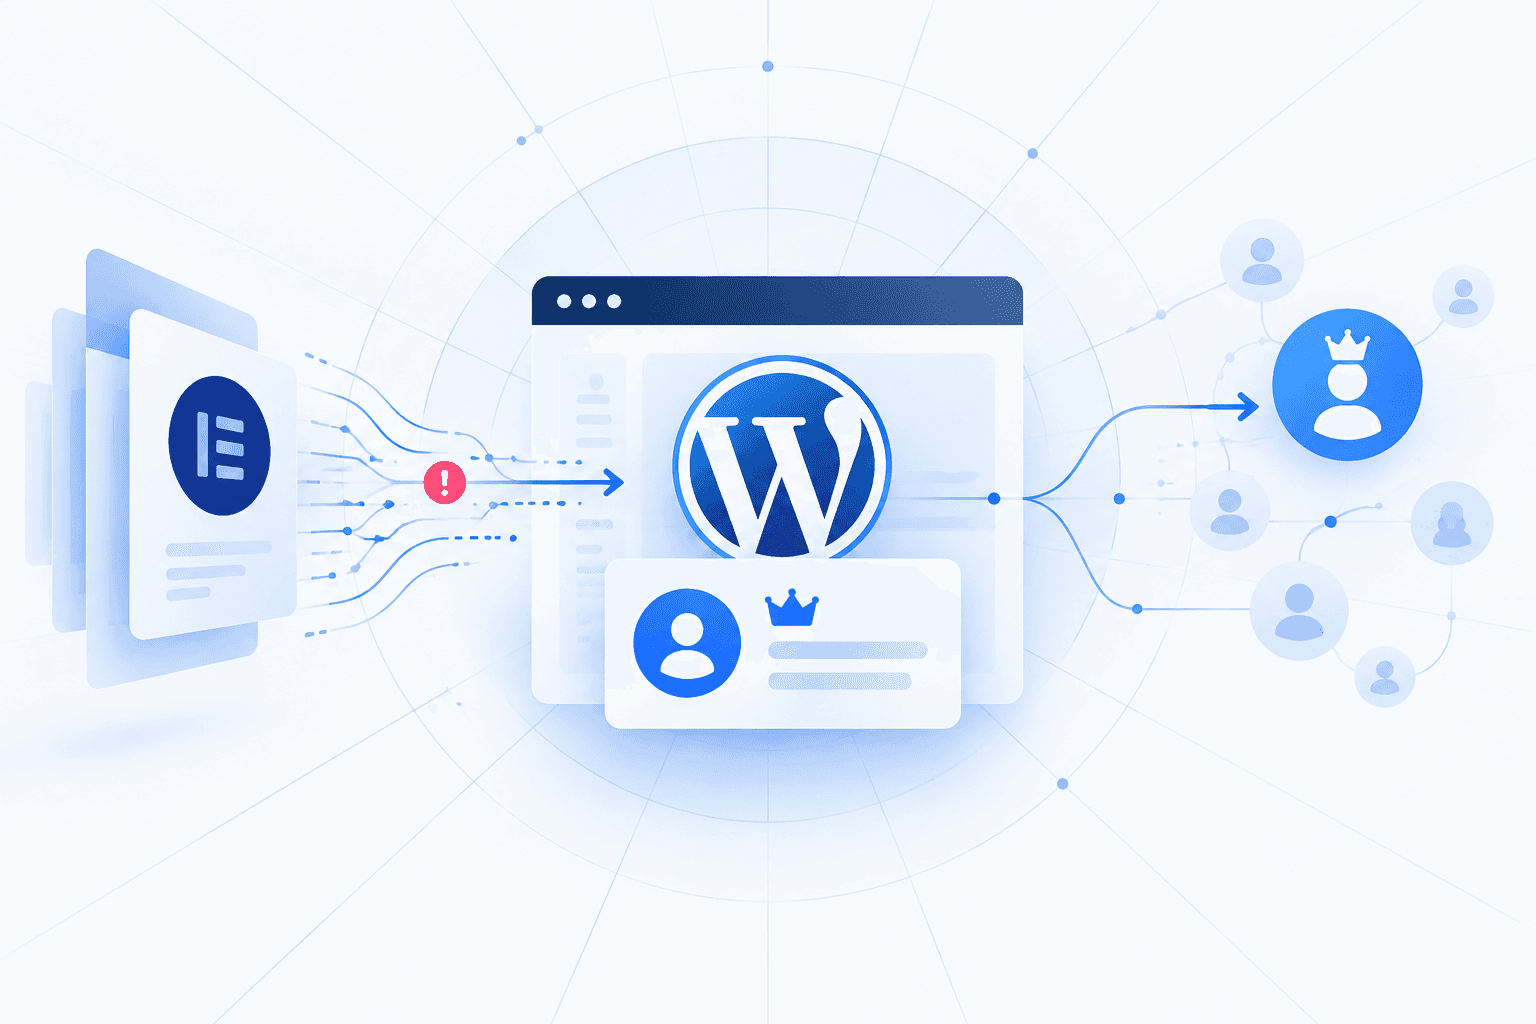
Elementor Website Builder versions 4.3.0 and 4.3.1 contain a cross-site request forgery (CSRF) flaw that can enable an unauthenticated attacker to create an administrator account on a WordPress site. Exploitation requires convincing a logged-in WordPress administrator to follow a malicious link, causing the victim’s authenticated session to submit a REST API account-creation request.
The issue stems from the Editor Events module bypassing WordPress REST nonce validation when a raw request URI includes elementor/v1/events/; attackers can append that path in query parameters to target other REST endpoints. Elementor fixed the vulnerability in version 4.3.2; organizations running the affected releases—potentially up to 2 million sites—should update immediately and review administrator accounts for unauthorized additions.