PolinRider Reinfects GitHub Repositories Through Compromised Contributor Accounts
Supply Chain Risk · 5 sources · Updated 2mo ago · First seen Sep 26, 2026
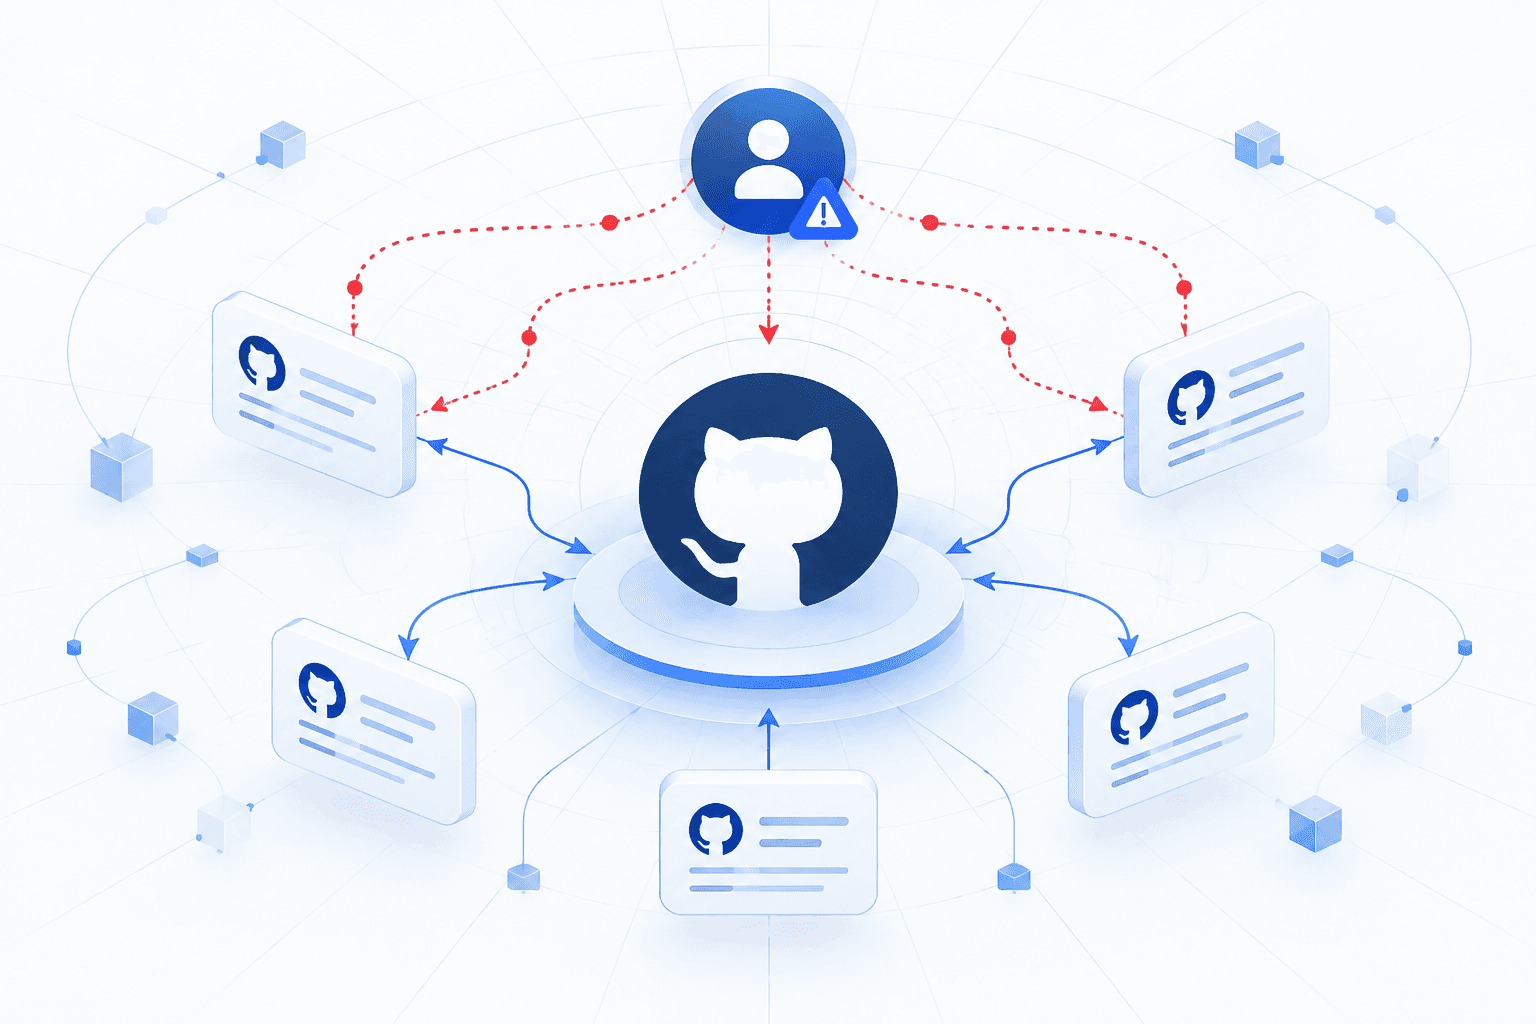
PolinRider operators compromised developer endpoints and used legitimate contributor credentials to repeatedly force-push malicious commits into three Binary-Mindz GitHub repositories. The supply-chain campaign embedded obfuscated JavaScript in fake Font Awesome .woff2 files and triggered execution through VS Code folder-open tasks and altered executable configuration files, including eslint.config.mjs and prisma.config.ts. Cleanup limited to repositories failed at least three times because other infected contributors reintroduced the code in rewritten commits retaining trusted authors, messages, and timestamps.
The operators deployed and evolved multiple payload variants—fa-solid-400.woff2, fa-solid-500.woff2, and fa-solid-900.woff2—apparently testing detection evasion. The 500 variant used an Ethereum NullReceiver dead-drop wallet to resolve command-and-control infrastructure, while the more obfuscated 900 variant adopted a legitimate Font Awesome filename and project-specific nested paths. A social-media post claimed the activity traced to North Korea, but provided no supporting technical evidence or independent attribution details.