Mallory
← Back to News
phishing-campaign-intelligenceremote-access-implantloader-delivery-mechanisminitial-access-method

Phishing Purchase Requests Deliver Remcos RAT via Office Exploit

Social Engineering & Fraud · 2 sources · Updated 2mo ago · First seen Sep 29, 2026
Phishing Purchase Requests Deliver Remcos RAT via Office Exploit

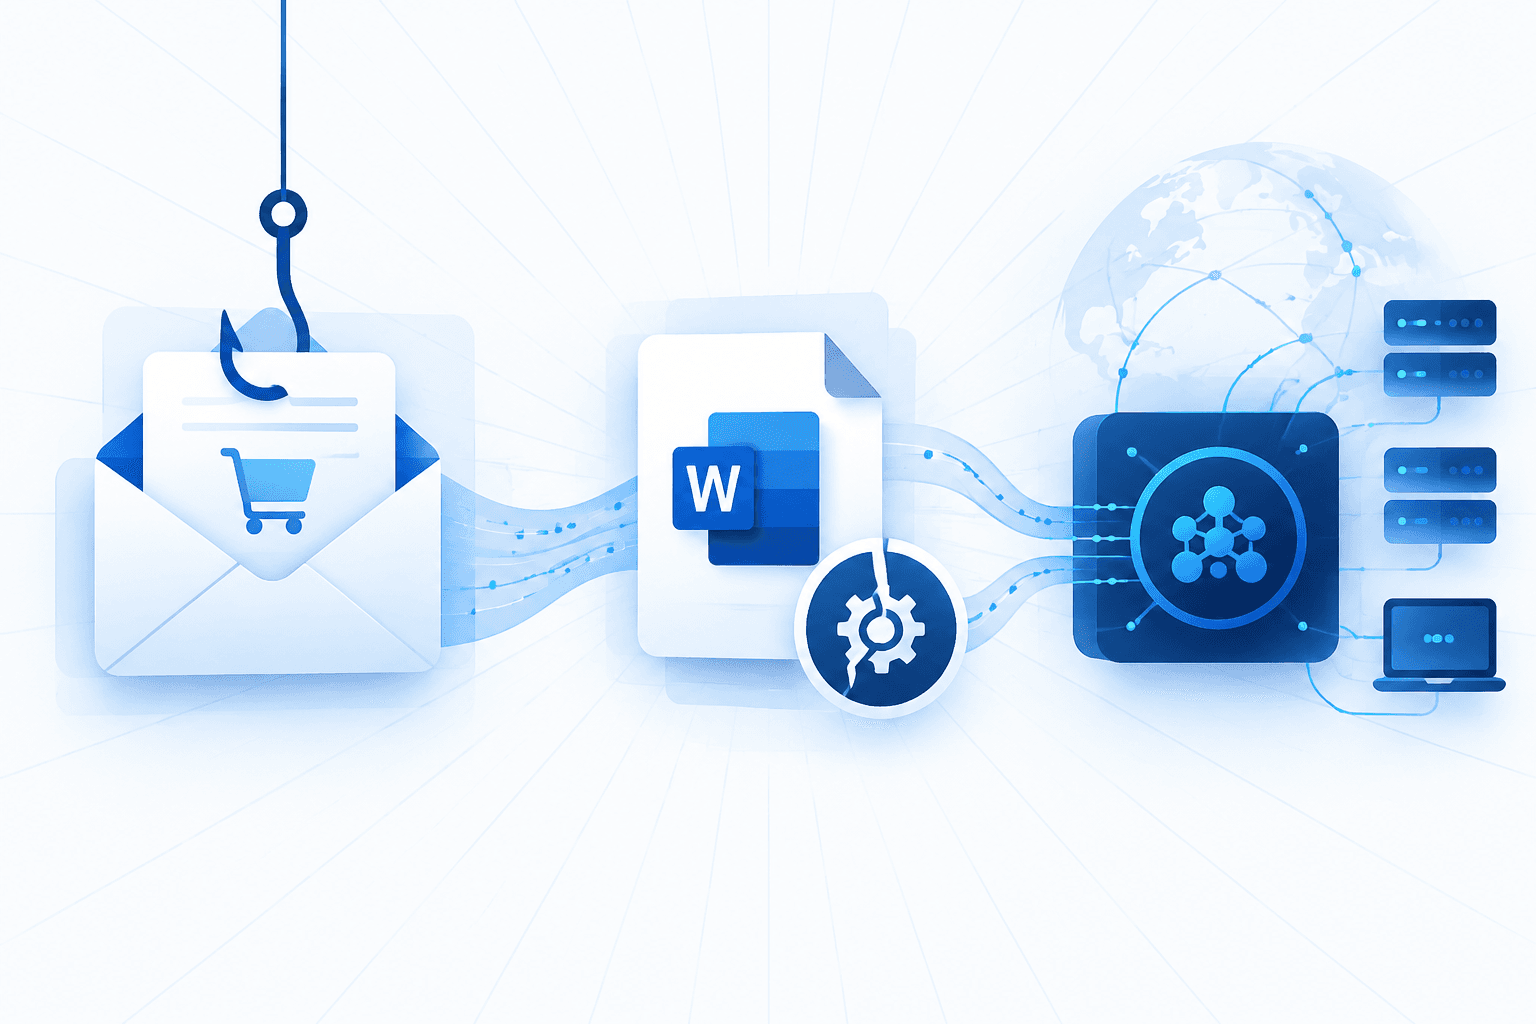
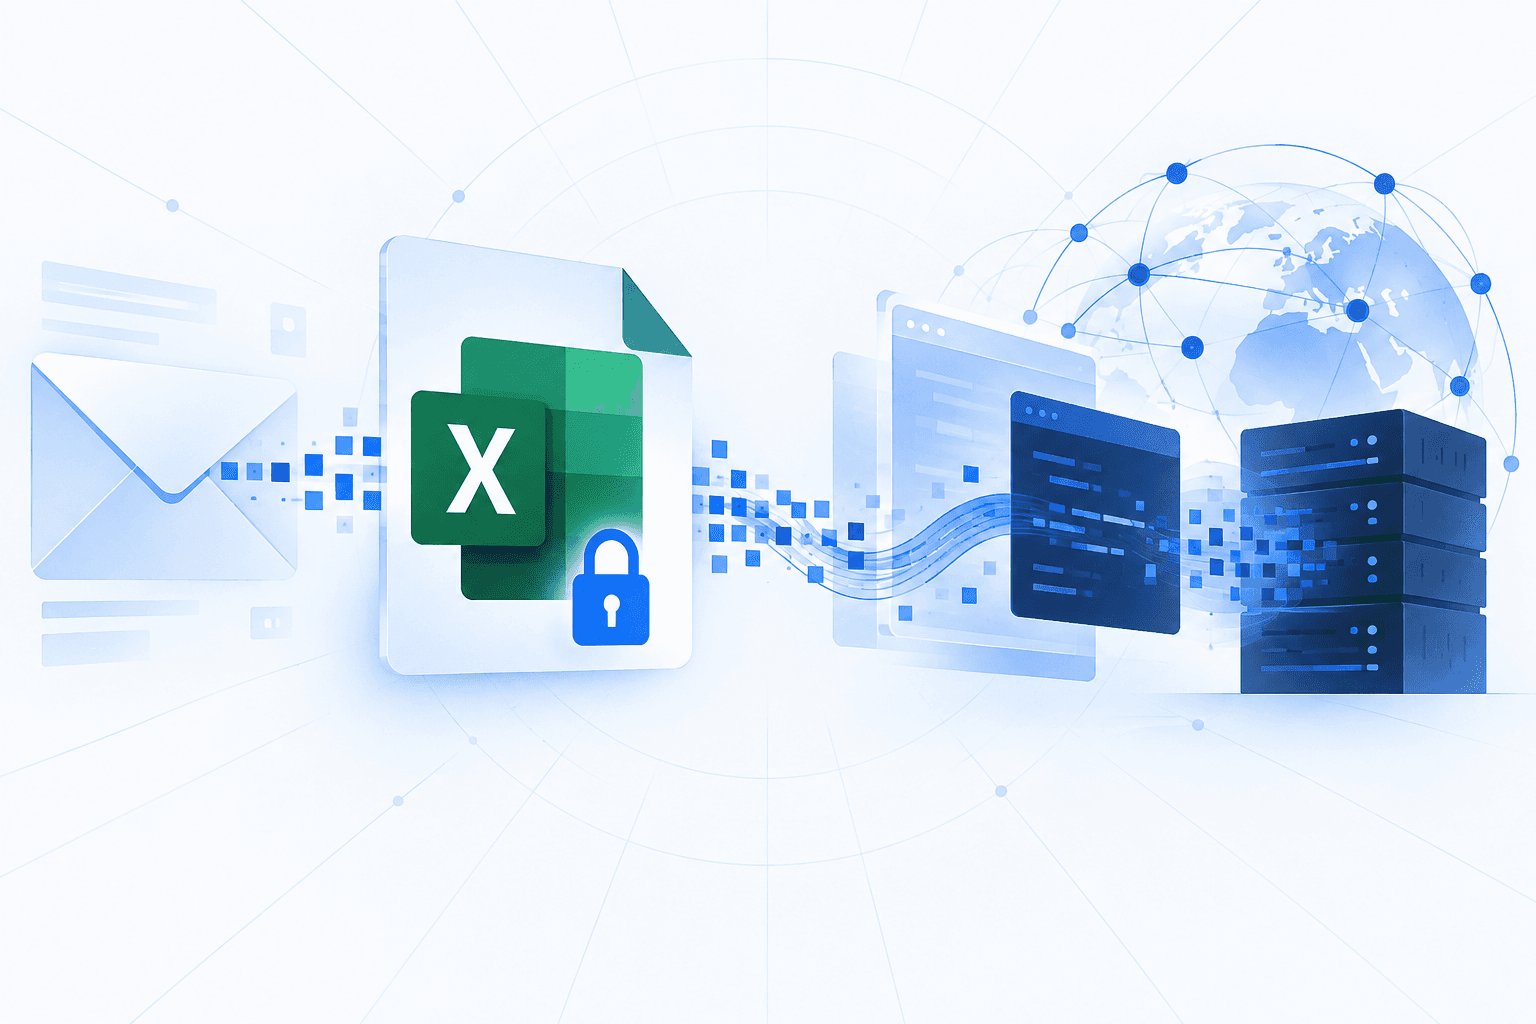
A phishing campaign impersonated employees of a South Korean company and sent project-material purchase-request emails carrying malicious XLS attachments. The spreadsheet displayed a credible decoy purchase form but exploited the Microsoft Office OLE2Link remote-code-execution flaw, CVE-2017-0199, to retrieve a malicious HTA payload.

The HTA invoked WMI Win32_Process.Create to launch obfuscated PowerShell, which downloaded a steganographic PNG containing an in-memory .NET loader. The loader deployed Remcos RAT, giving operators remote command execution and the ability to collect system and user data, log keystrokes, capture screens, manipulate files, and exfiltrate data through command-and-control infrastructure.
Is your org in this campaign?Get the infrastructure and lures behind it.
Hunt this campaign
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event
  1. Reported Sep 27, 20262mo ago

    Phishing campaign uses project-material purchase request XLS lures

    A phishing campaign impersonated employees of a South Korean company using project-material purchase-request forms to induce recipients to open malicious XLS attachments. The documents exploited CVE-2017-0199 to retrieve an HTA payload, ultimately deploying Remcos RAT for remote commands, data collection, keylogging, screen capture, and exfiltration.

    Beware of Phishing Emails That Disguise Themselves as Project Material Purchase Requests - ASEC
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Observables

10 linked

Indicator values are masked on this page. View all 10 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
Hunt This Campaign
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.