Mallory
← Back to News
remote-access-implantphishing-campaign-intelligencedefense-evasion-methodloader-delivery-mechanism

Encrypted Excel Phishing Delivers Fileless Remcos RAT via CVE-2017-0199

Active Exploitation · 1 source · Updated 1mo ago · First seen Sep 11, 2024
Encrypted Excel Phishing Delivers Fileless Remcos RAT via CVE-2017-0199

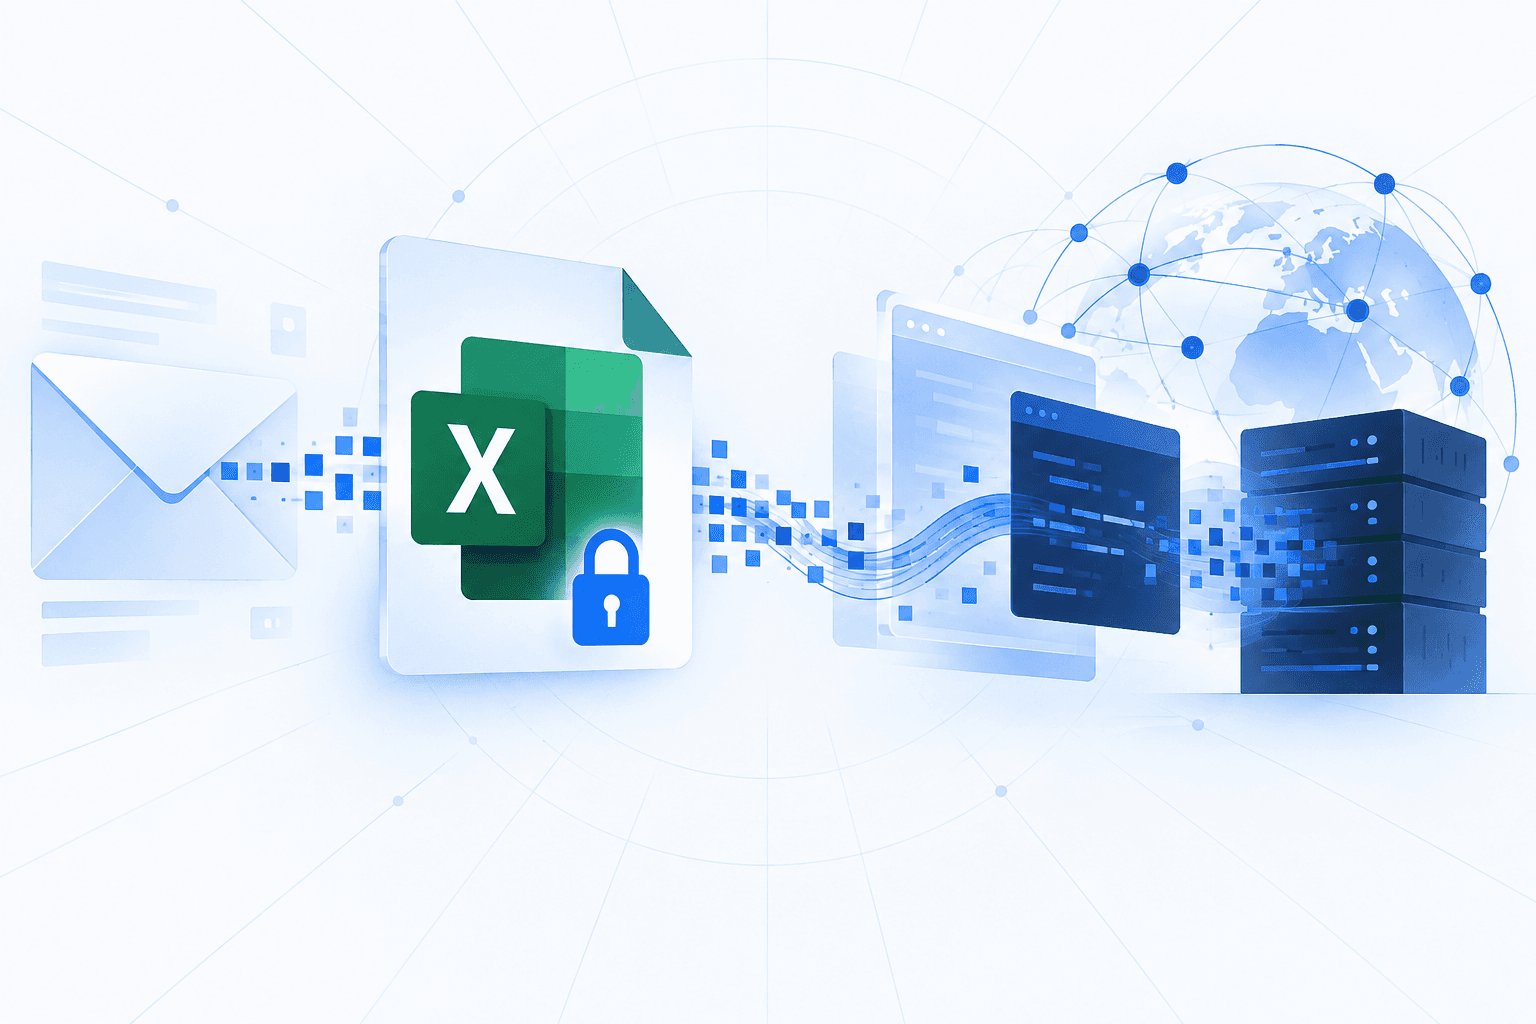
Trellix researchers identified a phishing campaign using encrypted Excel documents to deliver a fileless variant of Remcos RAT. The documents exploit CVE-2017-0199, with embedded OLE objects initiating an HTA-based execution chain that combines obfuscated PowerShell, VBScript, and payloads disguised as image files. The attackers load the dnlib.dll library into memory, construct a .NET payload from Base64-encoded data, and inject it into the legitimate RegAsm process.

The resulting infection enables persistent remote access and data exfiltration. Although the payload executes in memory, Trellix identified Remcos-related filesystem artifacts, including a keylogger file, providing additional detection opportunities. Defenders should verify remediation of CVE-2017-0199 and monitor Office-triggered HTA and script execution, suspicious RegAsm activity, and the reported Remcos artifacts rather than relying solely on detection of malware written to disk.
This is being exploited nowSee which actors are running it and whether you're in range.
Check your exposure
Event timeline

How this story unfolded

Events from the most recent confirmed update back to the earliest known activity.

1 event · Sep 11, 2024
  1. Sep 11, 20242y ago

    Trellix discloses Excel-based attack chain delivering fileless Remcos RAT

    Trellix published an analysis of a phishing campaign using encrypted Excel documents and CVE-2017-0199 to execute an obfuscated HTA, VBScript, and PowerShell delivery chain. The attack loads dnlib.dll into memory, constructs a Remcos RAT payload, and injects it into RegAsm; testing revealed Remcos-related memory strings and a keylogger file, but no specific victim or confirmed data theft was identified.

    Unmasking the Hidden Threat: Inside a Sophisticated Excel-Based Attack Delivering Fileless Remcos RAT
Linked entities

Related entities

Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.

Open in app →

Malware

1 linked

Affected products

3 linked
ExcelMicrosoft OfficeRemcos

Observables

17 linked

Indicator values are masked on this page. View all 17 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.

Do you run this?Correlate live exploitation activity against the software you actually run, and see where you're exposed.
See Who's Exploiting This
Mallory platform

See the full picture, correlated to your attack surface.

This page covers what’s public. Mallory adds the parts that aren’t: which of your assets are affected, which threat actors are using it right now, and what to deploy next.

Exposure mappingMap indicators from this story to your assets and identify affected systems in minutes.
Threat actor evidenceEvery observed campaign, victim, and pivot linked to actors named in this story.
Associated malwareMalware, exploits, and IOCs connected to the activity described here.
Detection signaturesYARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Scheduled alertsGet matching new stories delivered to your team as they break, not the next morning.
AI threadsAsk questions about this story and take action on the answers.