
Loading story…
Anthropic introduced the Claude Compliance API, enabling enterprise security and compliance teams to route Claude telemetry into more than 100 third-party monitoring, governance, and incident-response tools. For Claude Enterprise customers, the API can expose detailed records of chats, uploaded files, projects, prompts, responses, tool calls, sign-in activity, administrative changes, and selected Claude Code and Cowork session data, helping organizations identify sensitive-data exposure and policy violations.
The capability is designed to strengthen oversight of AI-agent activity and integrations that may introduce excessive permissions or unapproved MCP servers, connectors, plugins, and skills. Claude Platform customers receive activity, administrative, and system telemetry but not prompt or model-response content. On Claude Enterprise, only the Primary Owner can enable the API and create organization access keys; availability of individual vendor integrations ranges from private preview and beta to planned general availability through January 2027.
Track how attackers are adapting to this technology.
1 event from the most recent confirmed update back to the earliest known activity.
Anthropic introduced the Claude Compliance API, enabling Claude Enterprise and Claude Platform customers to send Claude activity telemetry to more than 100 security and compliance vendors. Enterprise feeds can include conversation, upload, project, Claude Code and Cowork data, while Platform feeds exclude prompts and model responses.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
Follow how adversaries are adapting to this technology, and where it touches your stack today.
2 references tracked. Mallory keeps watching after this page renders.
cybersecuritynews.com
Open sourcehelpnetsecurity.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Anthropic rolled out expanded *Claude Cowork* capabilities, adding **enterprise workflow plugins** intended to push agentic AI beyond software development into functions such as marketing, HR, legal, and finance, positioning Claude as a broader automation layer inside organizations. Coverage characterized the move as part of a wider shift toward AI-driven workflows in the enterprise, with implications for CIO governance, adoption patterns, and how teams operationalize AI outside engineering. Separately but related to the same product-direction narrative, commentary highlighted Anthropic formalizing **security-oriented features inside Claude**—including a prominent “**suggest fix**” capability aimed at moving from vulnerability detection to automated or semi-automated remediation—prompting market speculation about pressure on certain security-tool segments (particularly code-vulnerability discovery and remediation tooling). Other items in the set were not incident- or vulnerability-driven: one was generic SAST remediation guidance, and several were general-interest or business-trend pieces (e.g., an AI model blogging, AI-native software market dynamics, and an AI-agent governance/AX article) without specific, actionable cybersecurity event details.
Jun 29, 2026
Anthropic announced **Claude Code Security**, an embedded capability in *Claude Code* that scans customer codebases for vulnerabilities and suggests patches, initially rolling out to a limited set of enterprise/team customers for testing. The company said the feature was stress-tested via internal red-teaming, Capture-the-Flag exercises, and collaboration with **Pacific Northwest National Laboratory**, and positioned it as a way to reduce reliance on manual security reviews as AI-assisted “vibe coding” increases and attackers also use AI to accelerate weakness discovery. In parallel, Anthropic released **Claude Sonnet 4.6**, emphasizing improved coding performance, stronger “computer use” capabilities, and expanded developer tooling (e.g., adaptive/extended thinking modes, beta context compaction, and API tools for web search/fetch and code execution). Separate commentary highlighted the security risk of **agentic coding assistants** (e.g., *Claude Code*, *Cursor*, *GitHub Copilot*) operating with broad privileges—file access, shell execution, and secret handling—and argued that the emerging **Model Context Protocol (MCP)** ecosystem needs stronger, future-proof identity controls; additional industry guidance promoted **MLSecOps** as a way to integrate security into AI/ML development lifecycles, though it did not report a specific incident or vulnerability.
Jun 29, 2026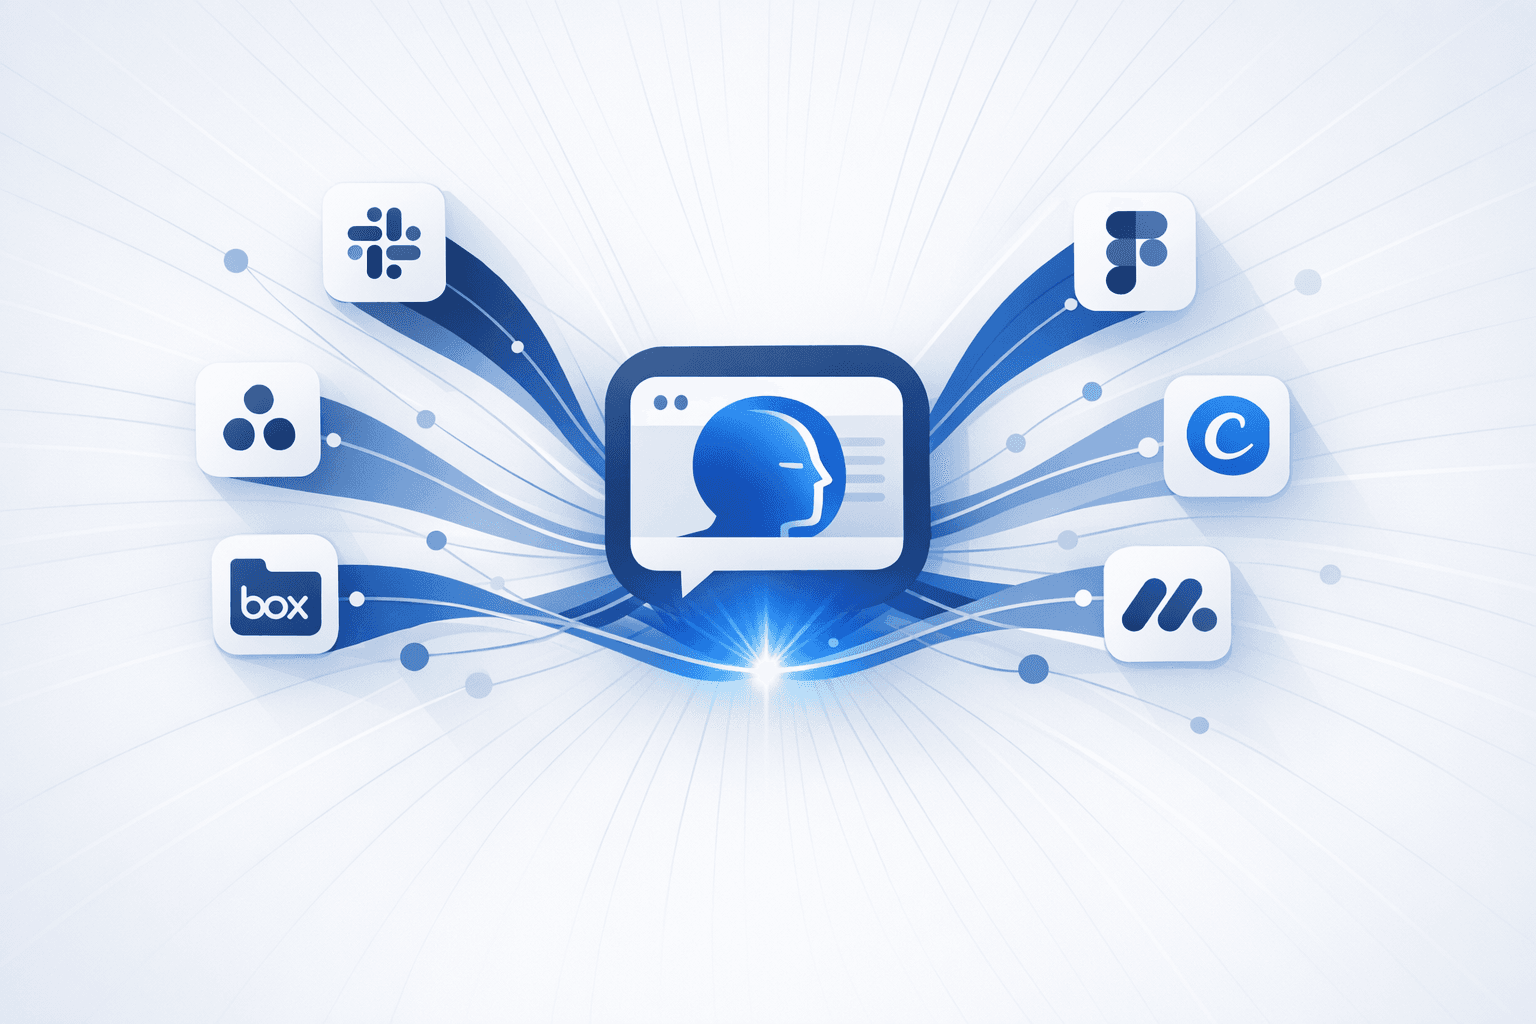
Anthropic released an update that lets **Claude** interact with third-party workplace applications *inside* the chat interface using the open **Model Context Protocol (MCP)**, reducing the need to switch between separate app tabs. The capability supports interactive embedded experiences (e.g., project boards, dashboards, design canvases, messaging) so users can view and edit content from services such as **Slack, Asana, Box, Canva, Figma, Hex, and monday.com** directly within Claude, including workflows like drafting incident communications or updating task timelines. The implementation is powered by an MCP extension described as **MCP Apps**, which allows an MCP server to provide an interactive UI that can render and accept user actions within an AI product. ZDNET characterized the move as part of Anthropic’s broader push to make Claude a primary work interface, building on earlier “connector” approaches that primarily moved data via prompts; the new approach enables more direct, app-native style interaction within the Claude conversation. A separate ZDNET piece offering general “IT playbook” guidance for the AI era does not provide substantive details about this specific Claude/MCP integration update.
Jun 29, 2026