
Loading story…
Threat actors used Facebook advertisements impersonating a cryptocurrency exchange and promising digital-asset rewards to distribute the Node.js-based JSCEAL malware. Victims were routed to convincing counterfeit exchange sites that profiled browser, campaign, and operating-system information before serving platform-specific installers. AhnLab reported roughly 1,500 Windows and macOS infections in South Korea during August and September 2026.
On Windows, the campaign used a malicious BAT loader to invoke PowerShell, create scheduled-task persistence, add a Microsoft Defender exclusion, and execute JavaScript or V8 bytecode through an embedded Node.js runtime. On macOS, a fraudulent PKG installer downloaded shell scripts, collected and validated the user's password, exfiltrated host and clipboard data, registered a LaunchAgent for persistence, and launched additional JavaScript-based payloads. Organizations should treat cryptocurrency-reward advertising as a likely social-engineering lure and block or investigate related counterfeit exchange downloads.
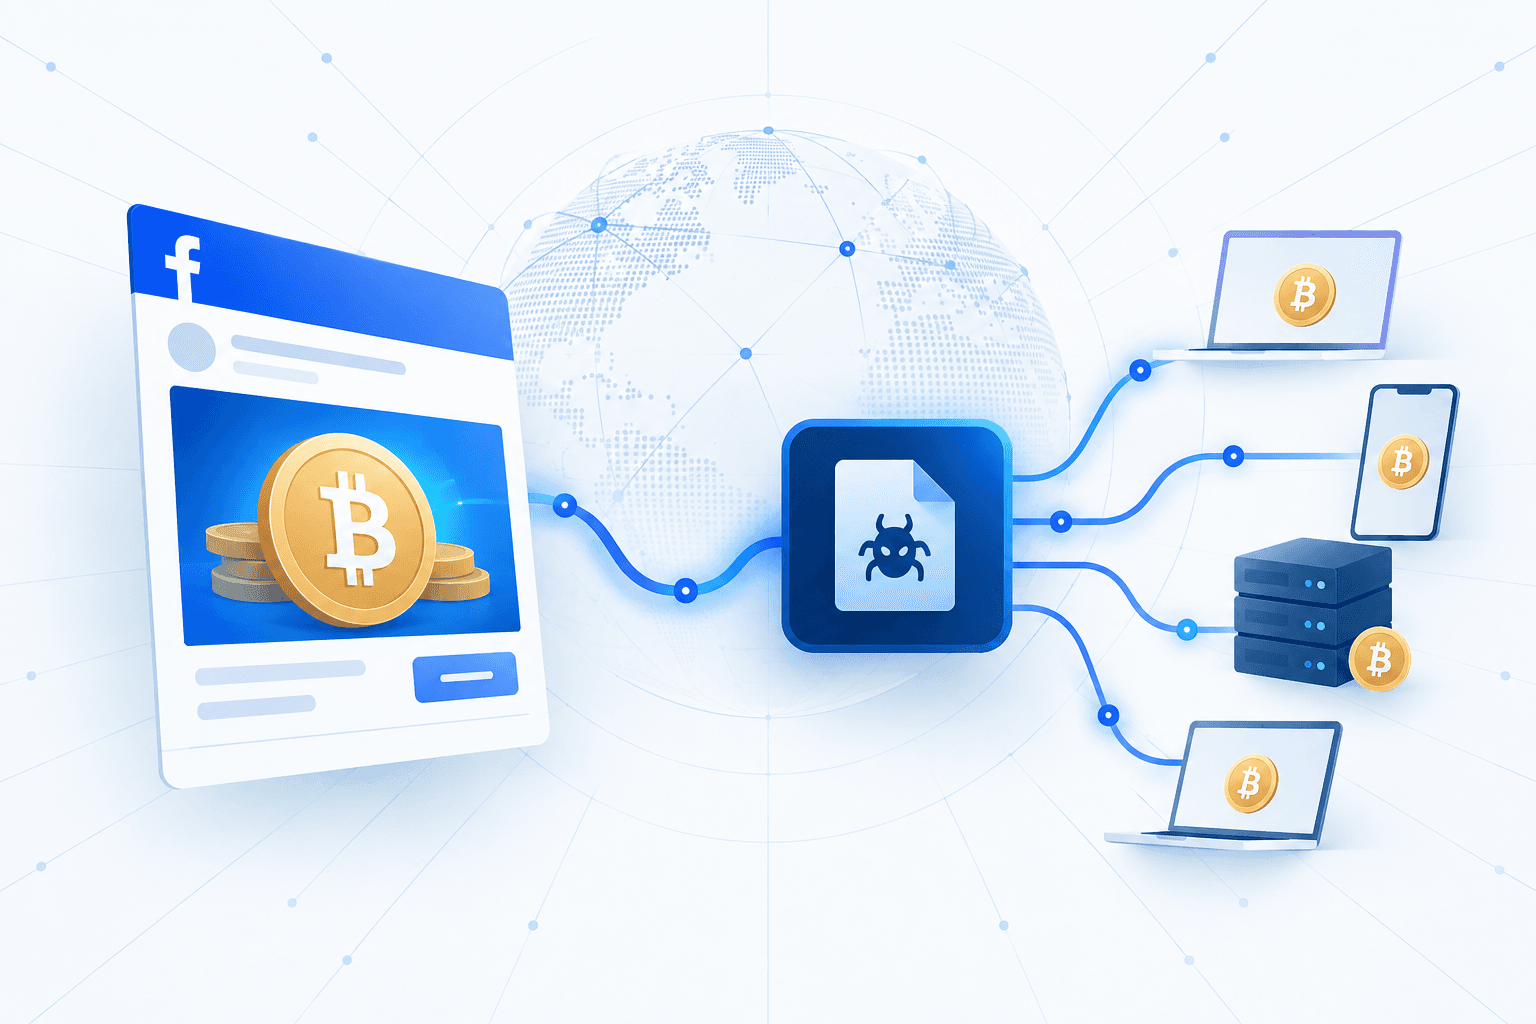
Get the infrastructure and lures behind it.
1 event from the most recent confirmed update back to the earliest known activity.
Threat actors used Facebook advertisements impersonating a cryptocurrency exchange and promising cryptocurrency rewards to distribute Node.js-based JSCEAL malware. Approximately 1,500 Windows and macOS systems in Korea were confirmed infected during August and September 2026.
Get the infrastructure, lures, and IOCs behind this campaign, ready to push into your email and identity stack.
2 references tracked. Mallory keeps watching after this page renders.
malware.news
Open sourceasec.ahnlab.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Check Point Research analyzed **JSCeal**, an actively developed Node.js/V8-based infostealer that steals browser credentials and cookies, Google OAuth tokens, cryptocurrency-account data, keystrokes, screenshots, and active-window information. Stolen browser cookies can enable attackers to reconstruct victim sessions, while the malware can automate elements of Google authentication with compromised passwords and collect newly issued Android-scoped OAuth tokens. JSCeal also installs an attacker-controlled root certificate and operates a local HTTPS interception proxy, enabling manipulation of traffic and content associated with cryptocurrency platforms including Binance, Bybit, Ledger, and Kraken. Recent versions adopted renamed and obfuscated launchers, a newer Node/V8 runtime, and AES-256-CBC encryption wrapping Brotli-compressed payloads; observed macOS targeting indicates that its operators are continuing to broaden platform coverage.
Sep 7, 2026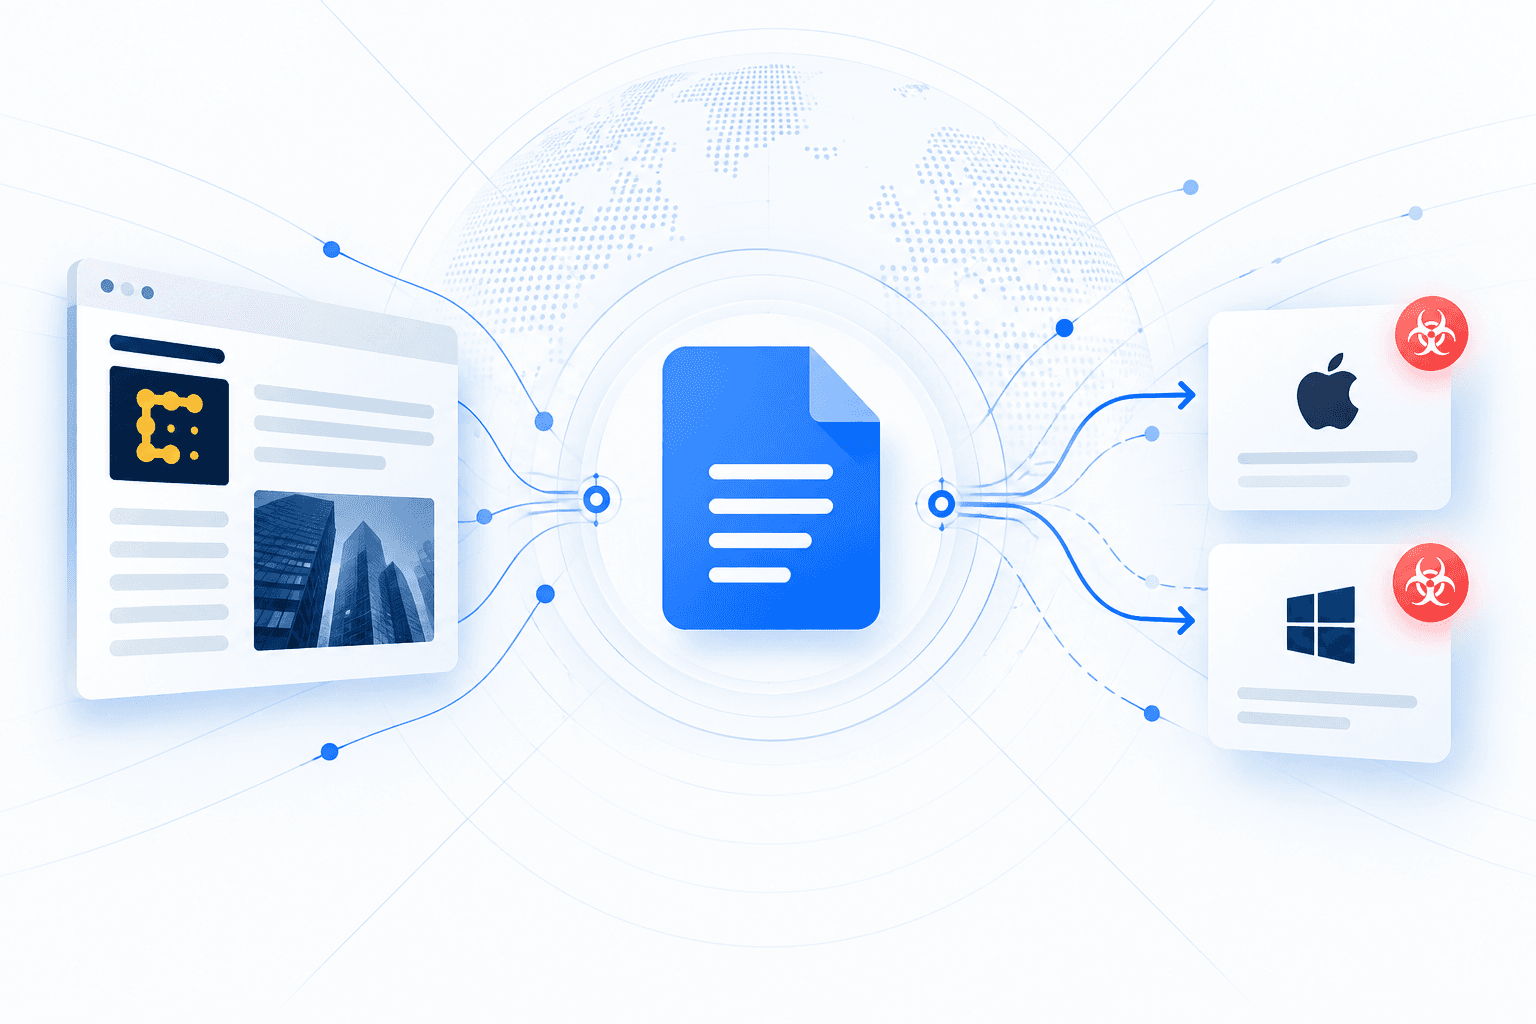
A threat actor impersonated a CoinDesk marketing executive in X direct messages, using post-Black Hat and DEFCON cryptocurrency-conference lures to target security researchers. The messages linked to legitimate Google Docs containing container-bound Google Apps Script that profiled visitors and sent their IP address, geolocation, browser details, and cryptocurrency-wallet-extension data to the operator through Telegram. The campaign routed victims to operating-system-specific malware: macOS users received a variant of the AMOS infostealer, while Windows users were served an encoded PowerShell loader chain and installers signed with three stolen or fraudulently issued certificates. Recovered Windows components included a malicious NetSupport Manager deployment, a persistent rogue local certificate authority capable of TLS interception, and a Ledger-wallet-focused implant. Russian-language comments and C2 artifacts indicate the operator may be Russian-speaking, but no threat group has been attributed.
Sep 14, 2026
U.S. agencies and private researchers linked multiple cryptocurrency-focused malware campaigns to North Korea’s **Lazarus Group**/**HIDDEN COBRA**, including the **AppleJeus** family delivered through fake but functional trading and wallet applications for **Windows** and **macOS**. CISA reports said variants including **Celas Trade Pro**, **JMT Trading**, **Kupay Wallet**, and **CoinGoTrade** were distributed from spoofed or seemingly legitimate websites such as `celasllc.com`, `jmttrading.org`, and `kupaywallet.com`, often with GitHub-hosted installers. The applications presented benign trading interfaces while secretly installing updater, daemon, or backdoor components that collected host information, established persistence, and fetched encrypted second-stage payloads from attacker-controlled infrastructure. The malware gave operators remote access to victim systems in cryptocurrency exchanges, financial services firms, and related organizations, with capabilities including command execution, file upload and transfer, reconnaissance, and payload staging. CISA tied the campaigns to Lazarus through infrastructure and code overlap with known implants such as **FALLCHILL**, **HOPLIGHT/MANUSCRYPT**, and the **CrashReporter** backdoor, while Proofpoint documented related Lazarus activity using phishing documents, JavaScript downloaders, malicious `LNK` and `CHM` files, and backdoored cryptocurrency apps to deploy **PowerRatankba**, a custom **Gh0st RAT** variant, and **RatankbaPOS**. Together, the reporting shows a sustained Lazarus effort to steal cryptocurrency and gain access to crypto-sector networks by masquerading malware as legitimate trading software.
Aug 15, 2026