Midnight Blizzard Abuses Guest Wi-Fi Captive Portals to Steal Credentials and Deploy Malware
Attack Tradecraft · 2 sources · Updated 25d ago · First seen Oct 6, 2026
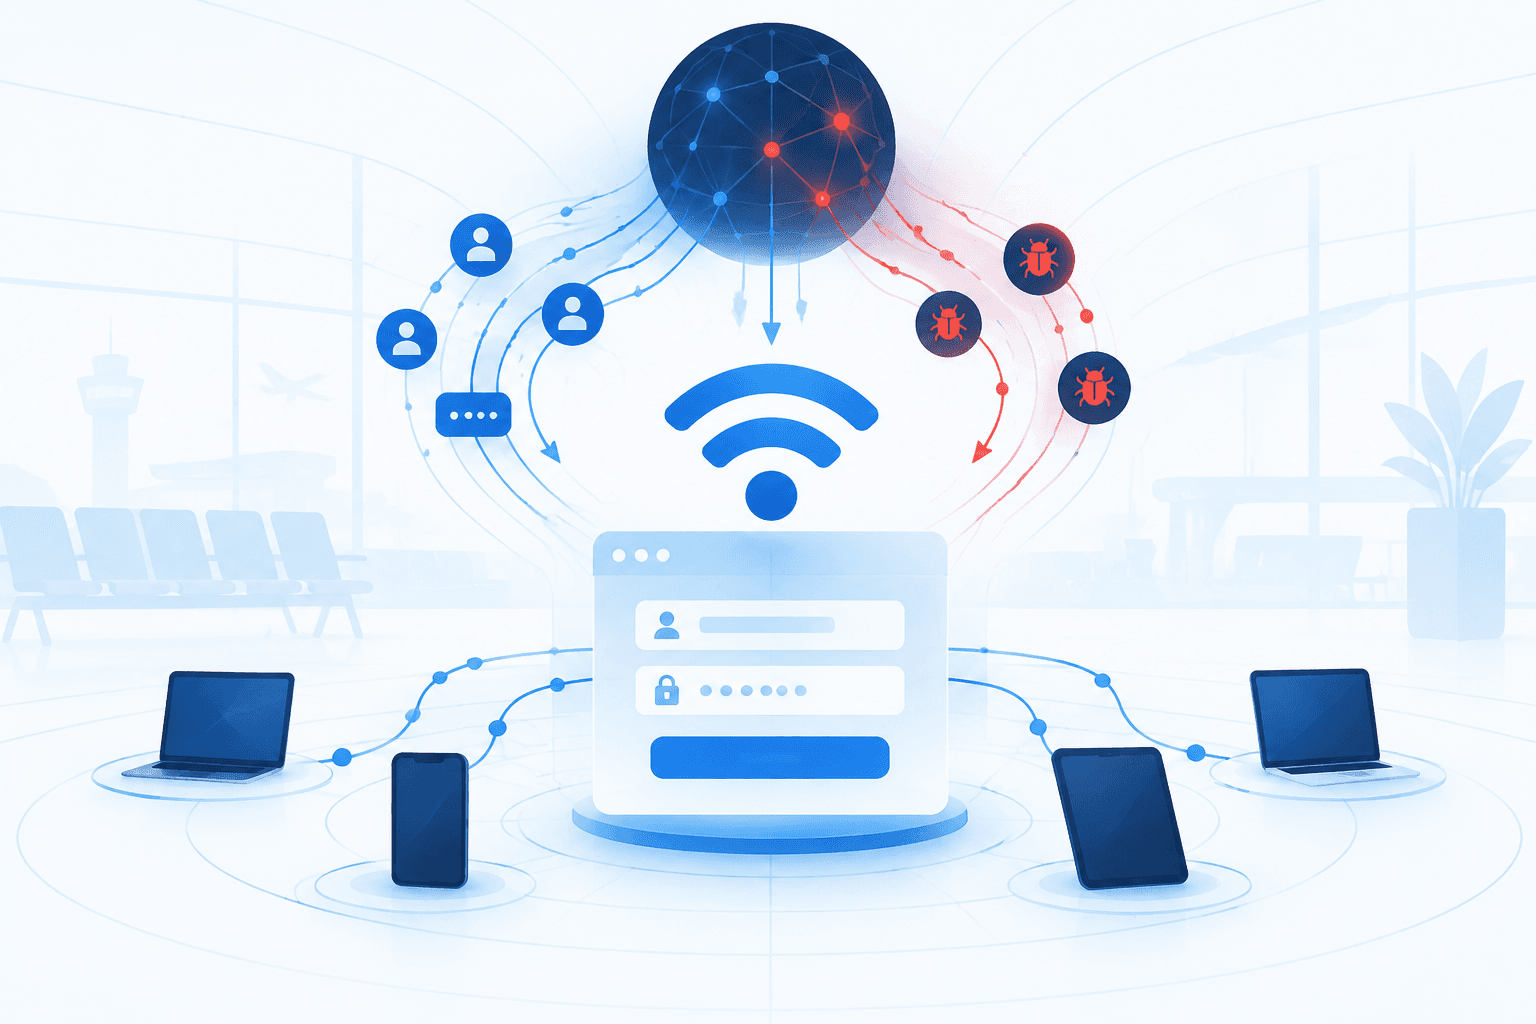
Microsoft attributed the CaptiveCrunch campaign to Storm-2945, an operational sub-cluster of Midnight Blizzard, which manipulates hotel and other guest-network captive portals to compromise travelers across several countries. Victims are redirected to fake updates, ClickFix prompts, and phishing pages that deliver the CornFlake remote-access trojan and ChocoShell infostealer or capture credentials and cloud session tokens. The campaign also uses adversary-in-the-middle and device-code phishing, creating paths from compromised traveler devices into corporate accounts.
Microsoft first observed the network manipulation in May 2026. An October 5 update reported renewed activity beginning September 29, including a Rust variant of CornFlake described as consistent with continued AI-assisted malware development. Organizations should advise travelers to use trusted connectivity and avoid downloads or remediation prompts presented by captive portals, deploy phishing-resistant authentication, restrict device-code authentication, and investigate reported campaign infrastructure and malware artifacts for signs of device or account compromise.