
Loading story…
Lazarus used a compromised Korean website to selectively infect visitors through vulnerable INITECH INISAFE CrossWEB EX software, according to AhnLab. The attackers subsequently exploited CVE-2021-26606 in Dream Security MagicLine4NX to compromise internal systems, used RDP, and attempted SSH access. Their activity included malicious thread injection into ftp.exe, service-based backdoor persistence, and firewall changes allowing communication over TCP port 60012. Separate reporting from Symantec identified Lazarus targeting the chemical sector; the supplied references do not establish that those targets were part of the same intrusion campaign.
AhnLab documented bring-your-own-vulnerable-driver (BYOVD) activity in which Lazarus deployed rootkit malware that used vulnerable drivers to modify kernel memory and disable anti-malware software, including AhnLab V3. This defense-evasion technique undermines endpoint protection after attackers obtain access. AhnLab recommended updating or removing the vulnerable software and enabling V3’s behavior-based detection. Defenders should also investigate unexpected driver loading, antivirus disruption, suspicious service creation, and unauthorized firewall rules permitting traffic on port 60012.
See which actors are running it and whether you're in range.
11 events from the most recent confirmed update back to the earliest known activity.
AhnLab ASEC published a separate analysis describing Lazarus's use of a Bring Your Own Vulnerable Driver rootkit attack to disable security software.
INITECH issued a vulnerability notice for INISAFE CrossWEB EX V3, the software Lazarus exploited to infect visitors to a compromised website.
Symantec reported that Lazarus used WMI to invoke MagicLine4NX on a remote system before injecting a malicious thread.
AhnLab ASEC published an analysis documenting Lazarus exploiting an INITECH process to infect systems.
A Dream Security notice documented CVE-2021-26606, a buffer overflow affecting MagicLine4NX version 1.0.0.17 and earlier that permits remote arbitrary command execution.
AhnLab published malware hashes, attacker infrastructure, and legitimate websites abused for command and control. It recommended updating or removing vulnerable INISAFE and MagicLine4NX software and enabling V3's behavior-based detection to block anti-malware-disabling activity.
In the documented execution chain, an injected thread in ftp.exe created a rootkit that deployed vulnerable DLL and driver files and registered them as a service. The rootkit obtained kernel-memory read and write capabilities and modified kernel memory to disable anti-malware programs, including AhnLab V3.
Lazarus attempted to log into SSH servers on internal systems using the root account; the report does not establish that these attempts succeeded.
After gaining access, Lazarus registered a backdoor as a service to maintain control of compromised systems. The attackers changed the host firewall to permit the backdoor's communications over TCP port 60012.
Lazarus exploited CVE-2021-26606 in Dream Security MagicLine4NX to compromise systems within internal networks and also accessed internal systems through RDP. The attackers used the MagicLine4NX process to inject a malicious thread into ftp.exe.
Lazarus modified a Korean website so malicious behavior activated only for visitors from selected IP addresses. Visitors running vulnerable INISAFE CrossWEB EX software could have SCSKAppLink.dll downloaded and executed through INISAFECrossWebEXSvc.exe.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. View all 30 in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
Correlate live exploitation activity against the software you actually run, and see where you're exposed.
2 references tracked. Mallory keeps watching after this page renders.
asec.ahnlab.com
Open sourcesymantec-enterprise-blogs.security.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
Lazarus targeted South Korean organizations through watering-hole attacks and spearphishing, abusing vulnerable local security software including **INITECH INISAFE CrossWeb EX** and **DreamSecurity MagicLine** to gain initial access and execute malware. AhnLab linked one 2022 wave to a signed INITECH process, `inisafecrosswebexsvc.exe`, after a malicious `SCSKAppLink.dll` was injected to fetch additional payloads from attacker-controlled infrastructure. Across multiple campaigns, victims included defense, finance, media, IT, public-sector, manufacturing, logistics, and pharmaceutical organizations, with reports describing more than 100 incidents and repeated use of compromised Korean websites, IP filtering, staged loaders, DLL side-loading, Windows service abuse, and persistence via the LSA Security Packages registry path. After compromise, Lazarus deployed backdoors including **NukeSped** and in some cases escalated to kernel-level evasion using a **bring your own vulnerable driver** technique. AhnLab said the group abused the signed but vulnerable `ene.sys` driver, and in some variants Dell's `CVE-2021-21551` driver path, to obtain arbitrary kernel memory access and disable security controls in memory, including file and registry callbacks, process and thread monitoring, WFP network filters, and ETW tracing. The activity also involved lateral movement through WMI, and sometimes RDP or SSH, plus credential theft, keylogging, screen capture, SOCKS tunneling, port forwarding, and internal reconnaissance, underscoring a sustained espionage-focused campaign that also created opportunities for supply-chain access and financial theft.
Aug 15, 2026
The North Korea-linked **Lazarus Group** expanded its long-running **Operation DreamJob** espionage campaign by using recruiter-themed lures, impersonation sites, and trojanized PDF software to compromise defense, aerospace, aviation, and UAV-related organizations in Europe, India, and other regions. Researchers said victims were sent tailored job descriptions through email, messaging platforms, and password-protected archives, then tricked into opening decoy documents with modified PDF readers that delivered malware including **ScoringMathTea**, **MISTPEN**, **ForestTiger**, and related loaders. ESET and Mandiant linked the activity to cyberespionage and theft of proprietary technology, with particular interest in drone manufacturing know-how and other sensitive defense-sector information. Check Point reported that the campaign escalated access by exploiting **`CVE-2026-68820`**, a zero-day local privilege escalation flaw in Microsoft **AFD.sys**, to deploy the **FudModule** rootkit with **SYSTEM** privileges and reduce endpoint detection visibility; Microsoft patched the issue on August 11, 2026. The operation also abused vulnerable **Roundcube** servers via **`CVE-2025-49113`** and installed the **RelayShell** PHP webshell to convert compromised web servers into command-and-control relay nodes, while compromised organizations were reused to spear-phish additional targets. Across the reporting, Lazarus showed a consistent pattern of evolving DreamJob tradecraft through trojanized open-source software, encrypted payload staging, DLL proxying, and use of trusted third-party infrastructure to improve stealth and credibility.
Aug 15, 2026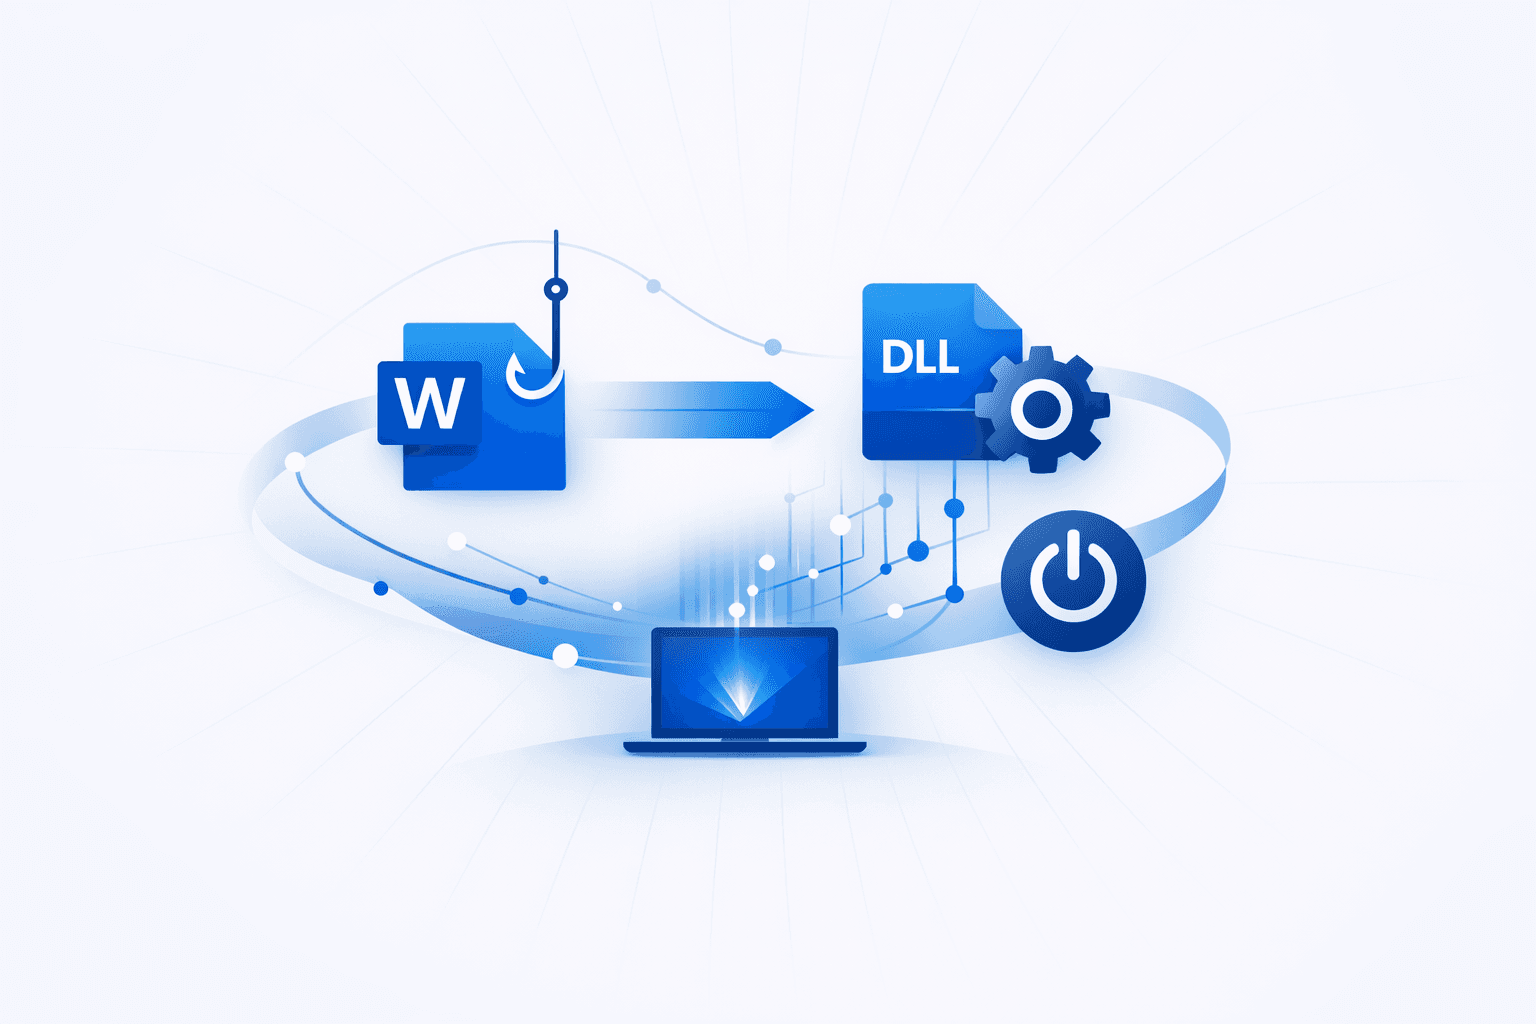
The **Lazarus Group** ran a spearphishing campaign that delivered malicious Microsoft Word documents to targets in aerospace, defense, research, and financial sectors, including organizations linked to Boeing, BAE Systems, Lockheed Martin, and the Republic of Korea Army. The infection chain used remote template injection to fetch an external `DOTM` file, whose macro dropped a lure document and a malicious DLL such as `onenote.db` into the victim’s `AppData` path, then executed the implant while showing a decoy file to reduce suspicion. Related reporting describes similar Lazarus lures sent in spoofed emails, with separate payloads for 32-bit and 64-bit systems and reconnaissance-focused first-stage malware. The implant executed through **`rundll32.exe`** and established persistence via the Windows **Startup folder**, techniques widely tracked in MITRE ATT&CK as `T1218.011` and `T1547.001`. Once active, it collected host, process, and disk information, compressed or encrypted the data, and exfiltrated it over HTTP POST using compromised or attacker-controlled infrastructure, including IIS/Plesk-hosted domains such as `elite4print.com` and `astedams.it`. Analysts linked the activity to Lazarus based on recurring tradecraft, lure themes, victim profiling, and overlap with operations such as **Operation Dream Job**, where the group similarly abused `rundll32.exe` and autostart mechanisms for stealthy execution and persistence.
Aug 15, 2026