Attackers Exploit Apache CouchDB RCE to Deploy Kinsing Miner and Rootkit
Active Exploitation · 2 sources · Updated 21d ago · First seen May 11, 2022
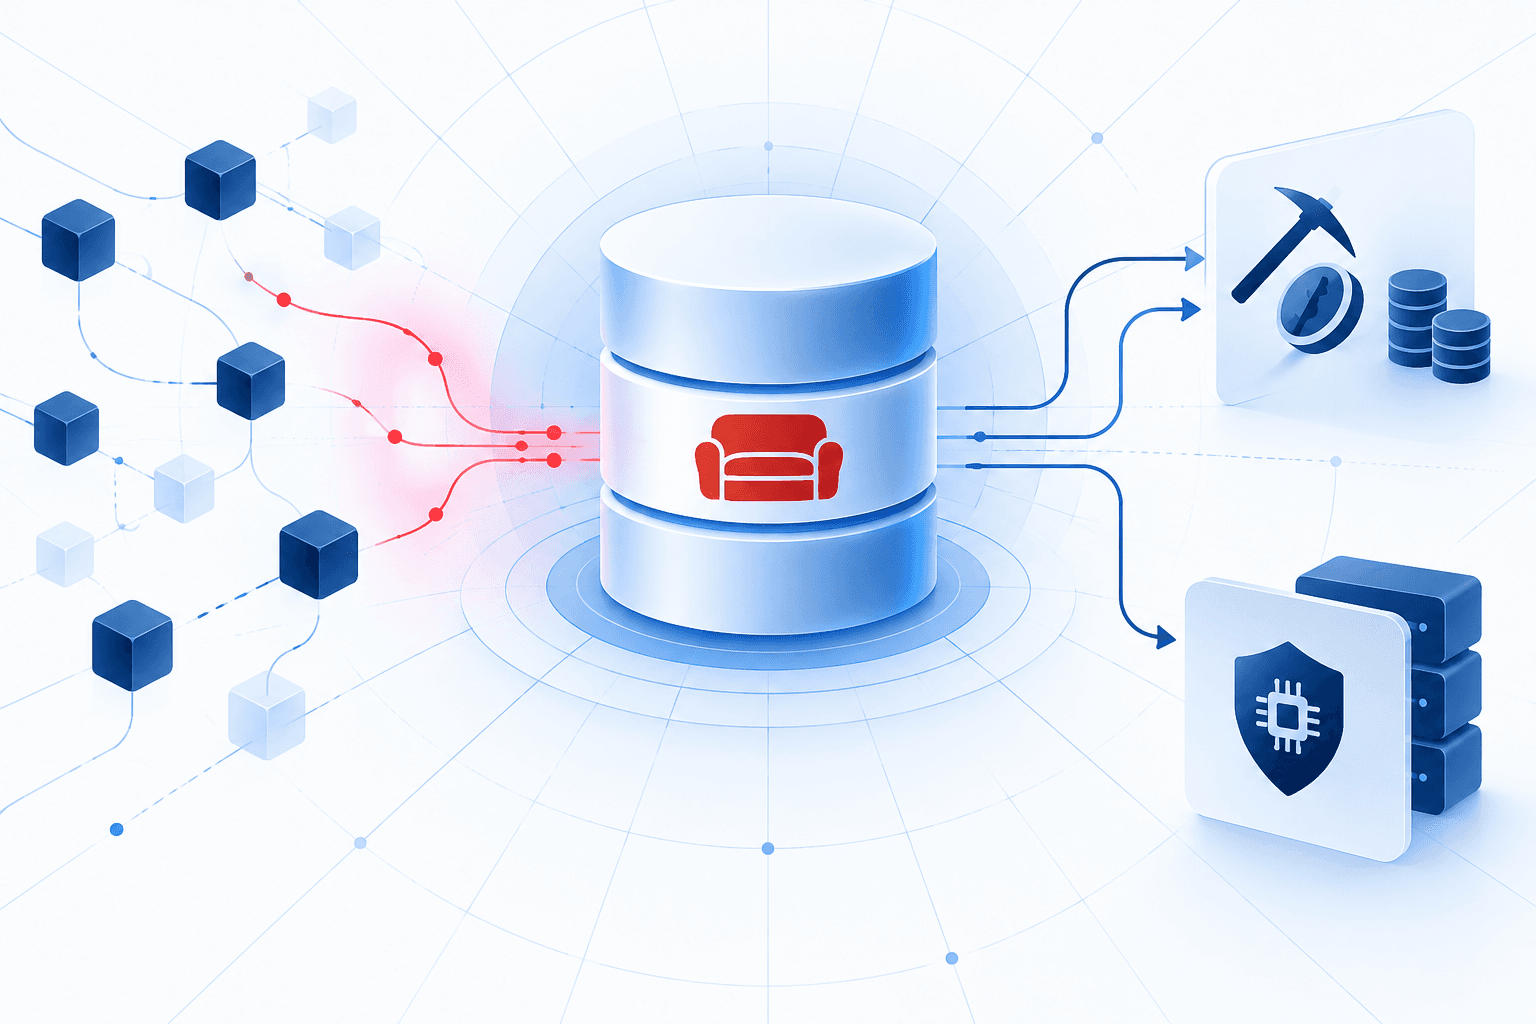
Attackers exploited CVE-2022-24706, a critical Apache CouchDB remote code execution vulnerability, to install Kinsing cryptocurrency-mining malware on improperly secured servers. CounterCraft observed exploitation shortly after a public exploit became available on May 11, 2022, following the vulnerability’s April disclosure. Exposed Erlang distribution ports and a default authentication cookie allowed unauthenticated attackers to execute commands and download a malicious shell script.
The script deployed Kinsing and the libsystem.so rootkit, attempted to disable defenses, removed competing miners, and established persistence through systemd and cron. Kinsing acted as a watchdog and deployed the cryptocurrency miner at /tmp/kdevtmpfsi. Earlier Trend Micro research had documented Kinsing’s use of rootkits, showing that this campaign combined a newly disclosed entry point with an established malware technique. Organizations running CouchDB should apply the relevant security updates, restrict access to Erlang distribution ports, replace default authentication cookies, and investigate unexpected services, cron entries, and mining processes.