
Loading story…
Kaspersky’s Global Emergency Response Team identified a PAYLOAD extortion campaign whose operators took control of an Active Directory environment without deploying ransomware or encrypting files. The attackers used a malicious Group Policy Object (GPO) to distribute a ransom note, alter workstation wallpapers and lock screens, display a login banner, and disable local administrator accounts. The incident illustrates how attackers can exploit centralized administrative control to pressure victims without relying on encryption.
Kaspersky described the campaign against the backdrop of evolving ransomware tactics in 2026, highlighting extortion based on infrastructure control and threats to expose confidential information. Backups can reduce the leverage of file encryption but cannot eliminate the reputational, security, and regulatory consequences of stolen data; the supplied reporting does not establish whether data was stolen in this incident. Recommended defenses include regular backups, prompt patching, multifactor authentication, endpoint monitoring, external exposure management, least privilege, and employee training. For defenders, the malicious GPO also underscores the importance of monitoring changes to domain policies and protecting privileged Active Directory access.
TTPs, infrastructure, and targeting history in one profile.
2 events from the most recent confirmed update back to the earliest known activity.
Kaspersky’s Global Emergency Response Team discovered PAYLOAD during an incident investigation. The attackers used their control of the victim’s infrastructure and access to confidential information as leverage rather than demanding payment for decryption.
PAYLOAD operators took control of a victim organization’s Active Directory environment without deploying ransomware or encrypting files. They used a malicious Group Policy Object to distribute a ransom note, change workstation wallpapers and lock screens, display a login banner, and disable local administrator accounts.
Vulnerabilities, threat actors, malware, products, organizations, and breaches Mallory has linked to this story.
See this adversary's TTPs, infrastructure, and targeting history, correlated against your exposure.
3 references tracked. Mallory keeps watching after this page renders.
kaspersky.com
Open sourcekaspersky.ru
Open sourcesecurelist.ru
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
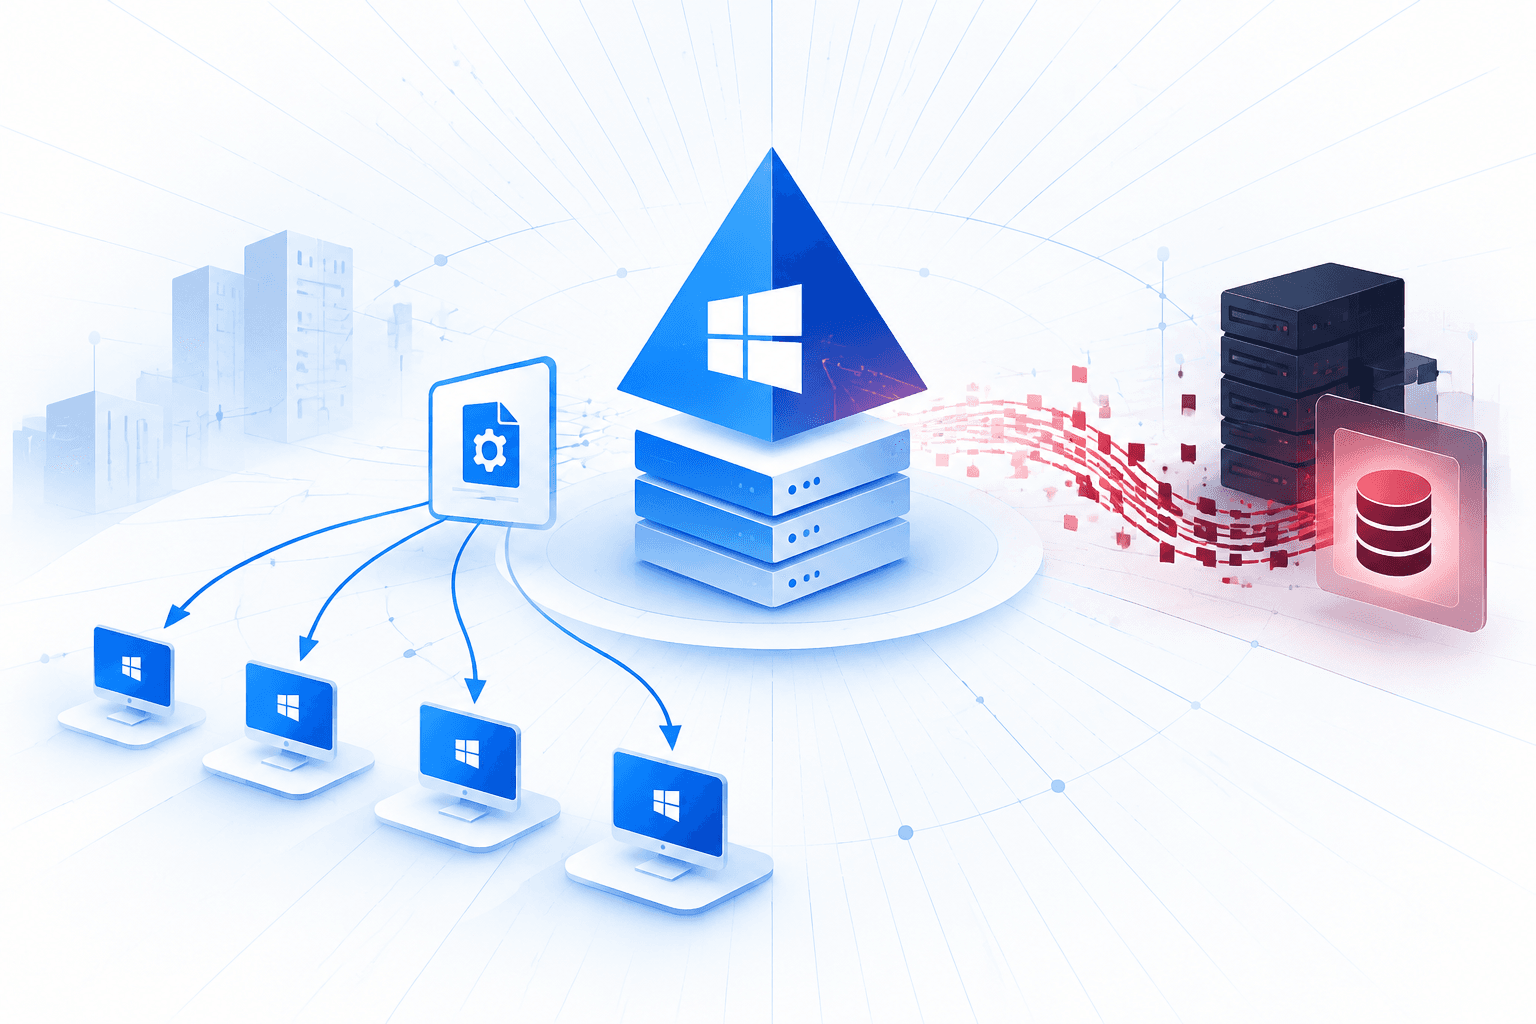
A PAYLOAD ransomware affiliate compromised a Middle Eastern manufacturing organization in April 2026 using a valid domain credential through a FortiGate SSL VPN. After obtaining domain-admin-equivalent Group Policy permissions, the actor linked malicious GPOs at the Active Directory domain root to distribute ransom notes, alter endpoint wallpapers and lock screens, set a ransom logon banner, disable local Administrator accounts, and disable Windows Firewall. Investigators found no encrypted Windows files, persistent endpoint malware, or active malicious processes; Active Directory and SYSVOL served as the attack control plane. The attackers exfiltrated data from file servers and other systems, later publishing it on the dark web, while an ESXi-targeting PAYLOAD sample was identified on Linux servers. The intrusion reflects the growth of **encryptionless extortion**, in which operators steal data and coerce victims without necessarily deploying file-encrypting malware. Extortion activity reached 6,182 reported incidents in 2025, while ransomware leak sites claimed 4,737 victims; attackers commonly combine stolen credentials, privilege escalation, legitimate administrative tooling, and centralized deployment mechanisms such as Group Policy. Organizations should prioritize MFA and monitoring for remote access, least-privilege controls over GPO administration, auditing of domain-root GPO changes and SYSVOL, rapid credential containment, and defenses against data exfiltration alongside endpoint ransomware controls.
Sep 24, 2026
Enterprise ransomware operations increasingly prioritize identity compromise, lateral movement, and data theft over immediately visible encryption. In Q4 2025, attackers used legitimate administration tools including RDP, SSH, PSExec, and native management utilities for lateral movement in 65% of observed cases; confirmed data exfiltration occurred in 94% of incidents, while encryption was confirmed in 68%. Defense evasion targeted endpoint protections, identity telemetry, and logging, and credential abuse increasingly relied on reuse, replay, inherited access, and trusted relationships. Cloud and SaaS environments have further reduced defender visibility and enabled faster, quieter exfiltration. Stolen data is also becoming a durable criminal asset rather than a one-time leak: at least 10 extortion groups were reportedly analyzing, indexing, categorizing, and reselling exposed enterprise data by July 2026, using analysts, scripts, machine learning, or LLM-assisted workflows. The compromise of The Gentlemen's Rocket.Chat infrastructure exposed a structured affiliate operation targeting Fortinet VPNs, using `CVE-2024-55591`, stolen credentials, proxy-chained movement, custom G-BOT infrastructure, repurposed Velociraptor, and AI tools for negotiation and data triage. Follow-on artifacts showed `rclone`, Synology NAS, and MEGA-based exfiltration and potential Active Directory exposure, underscoring the need to revoke exposed credentials comprehensively, hunt for data-transfer tooling, harden repositories, and monitor stolen data for resale and downstream social-engineering or supply-chain abuse.
Sep 28, 2026
Ransomware operators have repeatedly used tools and policy abuse to disable Microsoft Defender before encrypting Windows environments. DFIR reporting documented the freeware utility **Defender Control** being used in real intrusions by groups such as **Dharma**, **Phobos**, and **Crysis**, typically after access through exposed RDP, to turn off Defender through registry edits, service changes, driver unloading, and local group policy modifications. Separately, **LockBit 2.0** automated the same objective at enterprise scale by creating malicious Active Directory group policies on a domain controller, disabling Defender across domain-joined systems, and launching ransomware via scheduled tasks after enumerating hosts with AD and LDAP queries. More recent intrusions show the tactic evolving beyond simple utilities into **BYOVD** and broader policy abuse. WithSecure reported that the **CrazyHunter** ransomware actor used the vulnerable **Zemana Anti-Logger** driver `zam64.sys` to disable both Windows Defender and Trend Micro during attacks on Taiwanese hospitals and industrial organizations, including the Mackay Memorial Hospital incident. The operation also used publicly available tooling such as **SharpGPOAbuse** for lateral movement and persistence, reinforcing that defense evasion through Defender tampering and group policy manipulation remains a practical, low-barrier technique for ransomware actors ranging from smaller crews to more organized operators.
Aug 14, 2026