
Loading story…
A U.K. cryptocurrency trader posting as “realist” reported that intruders restrained him with tape and threatened him with knives at his home, stealing cryptocurrency and a Rolex in a robbery he valued at approximately $800,000. Solana transaction records show substantial USDC and SOL transfers through a wallet he identified as holding stolen funds, but do not establish who controlled the addresses or whether the transfers were coerced. The reported incident describes physical coercion—a “wrench attack”—rather than an established technical compromise of a Ledger device. The Defiant has not independently confirmed the assault, police attendance, or total loss.
Hudson Rock raised a possible connection to a recent Revolut customer-data breach after the victim confirmed he was a Revolut customer; Malware News also carried the report. According to Hudson Rock, attackers used compromised Italian government email credentials to socially engineer Revolut into releasing customer dossiers containing physical addresses and financial profiles. No evidence establishes that the robbers used the breached data, and the proposed connection remains speculative. The reports highlight the potential physical-security consequences of exposing financial profiles alongside home addresses, making protection of sensitive customer data and verification of official information requests important safeguards.
See the actors and campaigns active against you right now.
7 events from the most recent confirmed update back to the earliest known activity.
At 9:41 p.m. ET, the wallet Realist identified sent 718,735 USDC to an address beginning DN2cCPNJ. The transfer occurred after his initial public account of the robbery.
Transaction records show the identified wallet sent 20 SOL at 9:19 p.m. ET and another 326.13 SOL at 9:20 p.m. ET to an address beginning DWMDdqJU. The transfers do not establish the recipient's identity or involvement in the alleged robbery.
Realist said intruders restrained him with tape, threatened him with knives, and stole cryptocurrency and a Rolex in a robbery he valued at approximately $800,000. The Defiant dates his initial post to October 12, while Hudson Rock and its syndicated account describe the report as occurring on October 13; the assault and total loss were not independently confirmed.
SolanaFM records show that the wallet Realist identified as holding stolen funds received 718,735.80 USDC at approximately 6:58 p.m. ET on October 12. The records do not establish who controlled the wallet or whether the transfer was coerced.
In a follow-up reply on X, Realist confirmed that he banked with Revolut. Hudson Rock raised a possible connection to the customer-data disclosure, but provided no evidence that the robbers used breached Revolut data.
After initially saying he was with police, Realist said officers were at his house collecting footage and that he could not enter because the property was being treated as evidence. The Defiant did not independently confirm police attendance.
According to Hudson Rock, attackers used compromised Italian Ministry of the Interior email credentials to bypass Revolut's verification processes and obtain customer dossiers containing physical addresses and financial profiles. The report does not establish that this disclosure enabled the subsequent robbery.
Vulnerabilities, threat actors, malware, products, organizations, breaches, and observables Mallory has linked to this story. Indicator values are masked here and available in full in the app.
Indicator values are masked on this page. See the values in Mallory Domains, IPs, hashes, and URLs are exportable to your SIEM.
See the adversaries and campaigns active against your sector right now, ranked by what they're exploiting.
3 references tracked. Mallory keeps watching after this page renders.
malware.news
Open sourcethedefiant.io
Open sourcehudsonrock.com
Open sourceMap indicators from this story to your assets and identify affected systems in minutes.
Every observed campaign, victim, and pivot linked to actors named in this story.
Malware, exploits, and IOCs connected to the activity described here.
YARA, Sigma, and Snort rules deployed to your SIEM as soon as they’re published.
Get matching new stories delivered to your team as they break — not the next morning.
Ask questions about this story and take action on the answers.
Other stories Mallory is tracking that overlap on entities, sources, or topic labels.
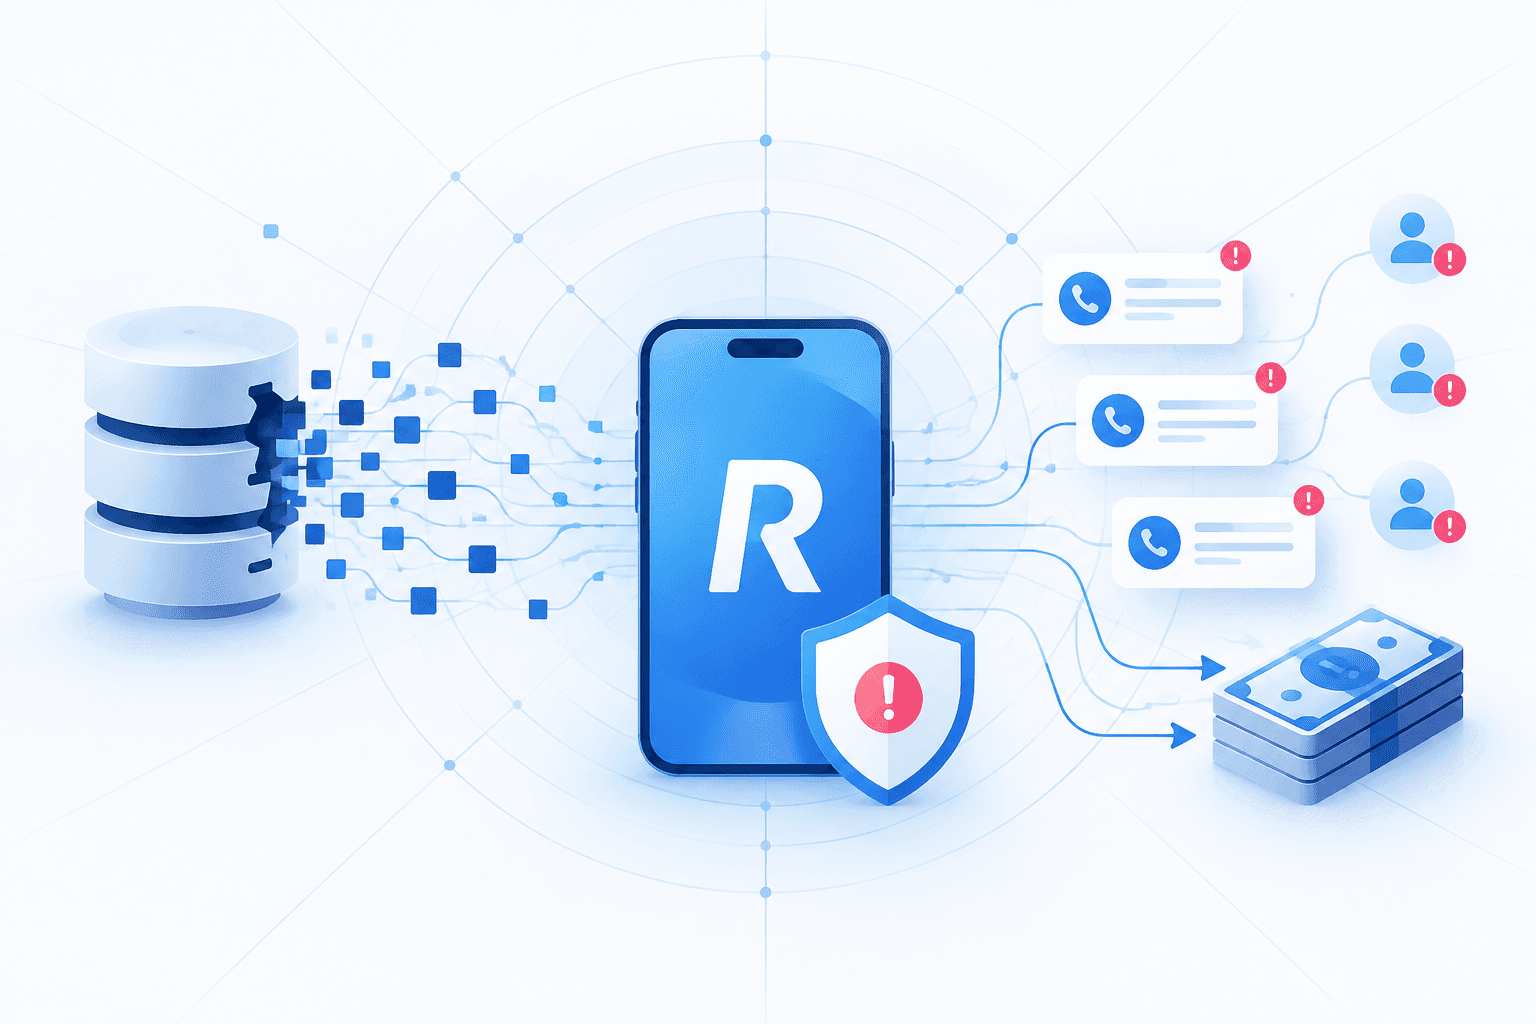
Revolut disclosed that it released customer information to a third party responding to fraudulent requests sent through a spoofed government email domain. Attackers allegedly used infostealer-compromised Italian Ministry of the Interior email accounts to monitor communications for months and issue fake European Investigation Orders seeking KYC records from Revolut’s Lithuanian-regulated entity. The actor calling itself **“IAmNotAVillain”** claims to possess personal, identity-verification, and financial data and has reportedly demanded a **$3 million** ransom, although Revolut said it received no direct demand and that customer funds and its core systems were unaffected. The stolen data has reportedly enabled a targeted SMS-phishing campaign against Revolut customers, including high-net-worth cryptocurrency users selected through blockchain-record analysis. Some smishing messages appeared within legitimate Revolut SMS threads and linked victims to counterfeit pages that mimicked the bank’s live-video identity-verification process before requesting account passwords. Revolut said it blocked the fraudulent address and notified authorities and regulators; customers should treat unsolicited identity-verification or password requests as phishing and verify communications through official Revolut channels.
Sep 25, 2026
Cybercriminals in Europe are increasingly resorting to physical violence, including kidnappings and assaults, to extort cryptocurrency and privileged access from victims. According to CrowdStrike's European Threat Landscape Report and corroborated by multiple security researchers, at least 17 to 18 such incidents have been reported since early 2025, with France experiencing the majority of cases. Notable attacks include the January kidnapping and mutilation of Ledger co-founder David Balland and his wife, as well as a series of violent robberies targeting individuals known to possess significant cryptocurrency assets. Law enforcement has made several arrests, including the alleged ringleader in Morocco, but the threat persists and is evolving. Experts note that these attacks often combine cyber and physical tactics, with criminals using cyberattacks as distractions or to identify high-value targets before launching in-person assaults. The rise of "violence as a service" is forcing organizations and individuals, especially those in the cryptocurrency sector, to reevaluate their security strategies and consider physical protection alongside traditional cyber defenses. Security consultants warn that playbooks for incident response must now account for the possibility of real-world violence accompanying digital threats, marking a significant escalation in the risk landscape for privileged users and executives in Europe.
Jun 29, 2026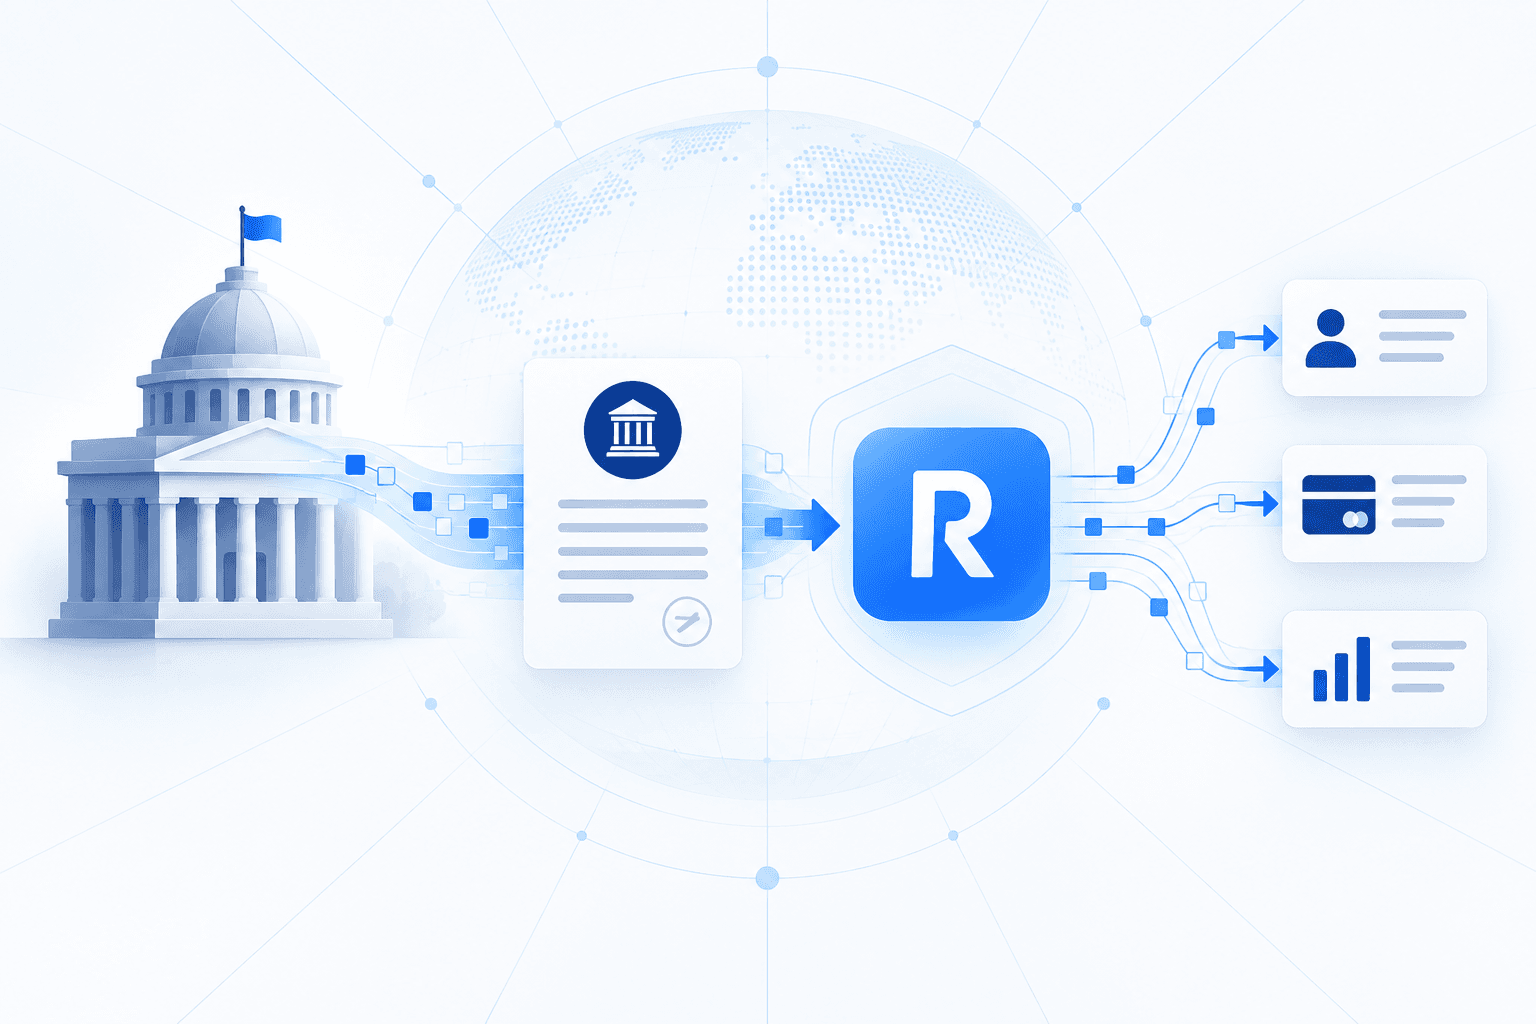
Revolut disclosed that it released sensitive customer information to an unauthorized party after receiving a fraudulent data request impersonating a legitimate government agency. The request reportedly originated from an unauthorized account using an official agency email domain with valid domain-authentication credentials, causing it to be treated as legitimate. The number of affected customers, the impersonated authority, and the precise failure path have not been publicly confirmed. The exposed records reportedly include passport or other KYC identity documents, facial-verification selfies, contact details, account statements, IBANs, withdrawal records, and full transaction histories, including Bitcoin-related activity. Revolut said its core systems, mobile app, customer accounts, and funds were not compromised; it blocked the email source, notified authorities, and contacted affected users. The combined identity and financial data creates elevated risks of identity fraud, targeted phishing and vishing, SIM-swapping, fraudulent account opening or direct debits, extortion, and persistent linkage between customer identities and blockchain addresses.
Sep 18, 2026